Security Audit Tool
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
Alimenter votre agent
La commande propre à l'éditeur. Ce n'est pas un endpoint PlugMCP.
Host a copy with our keys and logs.
npx -y @iflow-mcp/[email protected]Claude Code n'a pas de lien d'installation pour une commande locale. Copiez la commande ci-dessous et exécutez-la dans un terminal.
claude mcp add qianniuspace-mcp-security-audit -- npx -y @iflow-mcp/mcp-security-audit@1.0.4À exécuter dans un terminal.
{ "mcpServers": { "qianniuspace-mcp-security-audit": { "command": "npx", "args": [ "-y", "@iflow-mcp/[email protected]" ] } }}claude_desktop_config.json
URL distante ou commande sur votre machine ? Ce qui distingue les deux installations
Exécuter sur PlugMCP
A new server you create. It is not this listing's official endpoint. Use the publisher install when you want their URL and their credentials.
LancerDe l'éditeur
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
To install Security Audit Tool for Claude Desktop automatically via Smithery:
npx -y @smithery/cli install @qianniuspace/mcp-security-audit --client claude
{
  "mcpServers": {
    "mcp-security-audit": {
      "command": "npx",
      "args": ["-y", "mcp-security-audit"]
    }
  }
}
git clone https://github.com/qianniuspace/mcp-security-audit.git
cd mcp-security-audit
npm install
npm run build
{
  "mcpServers": {
    "mcp-security-audit": {
      "command": "npx",
      "args": ["-y", "/path/to/mcp-security-audit/build/index.js"]
    }
  }
}
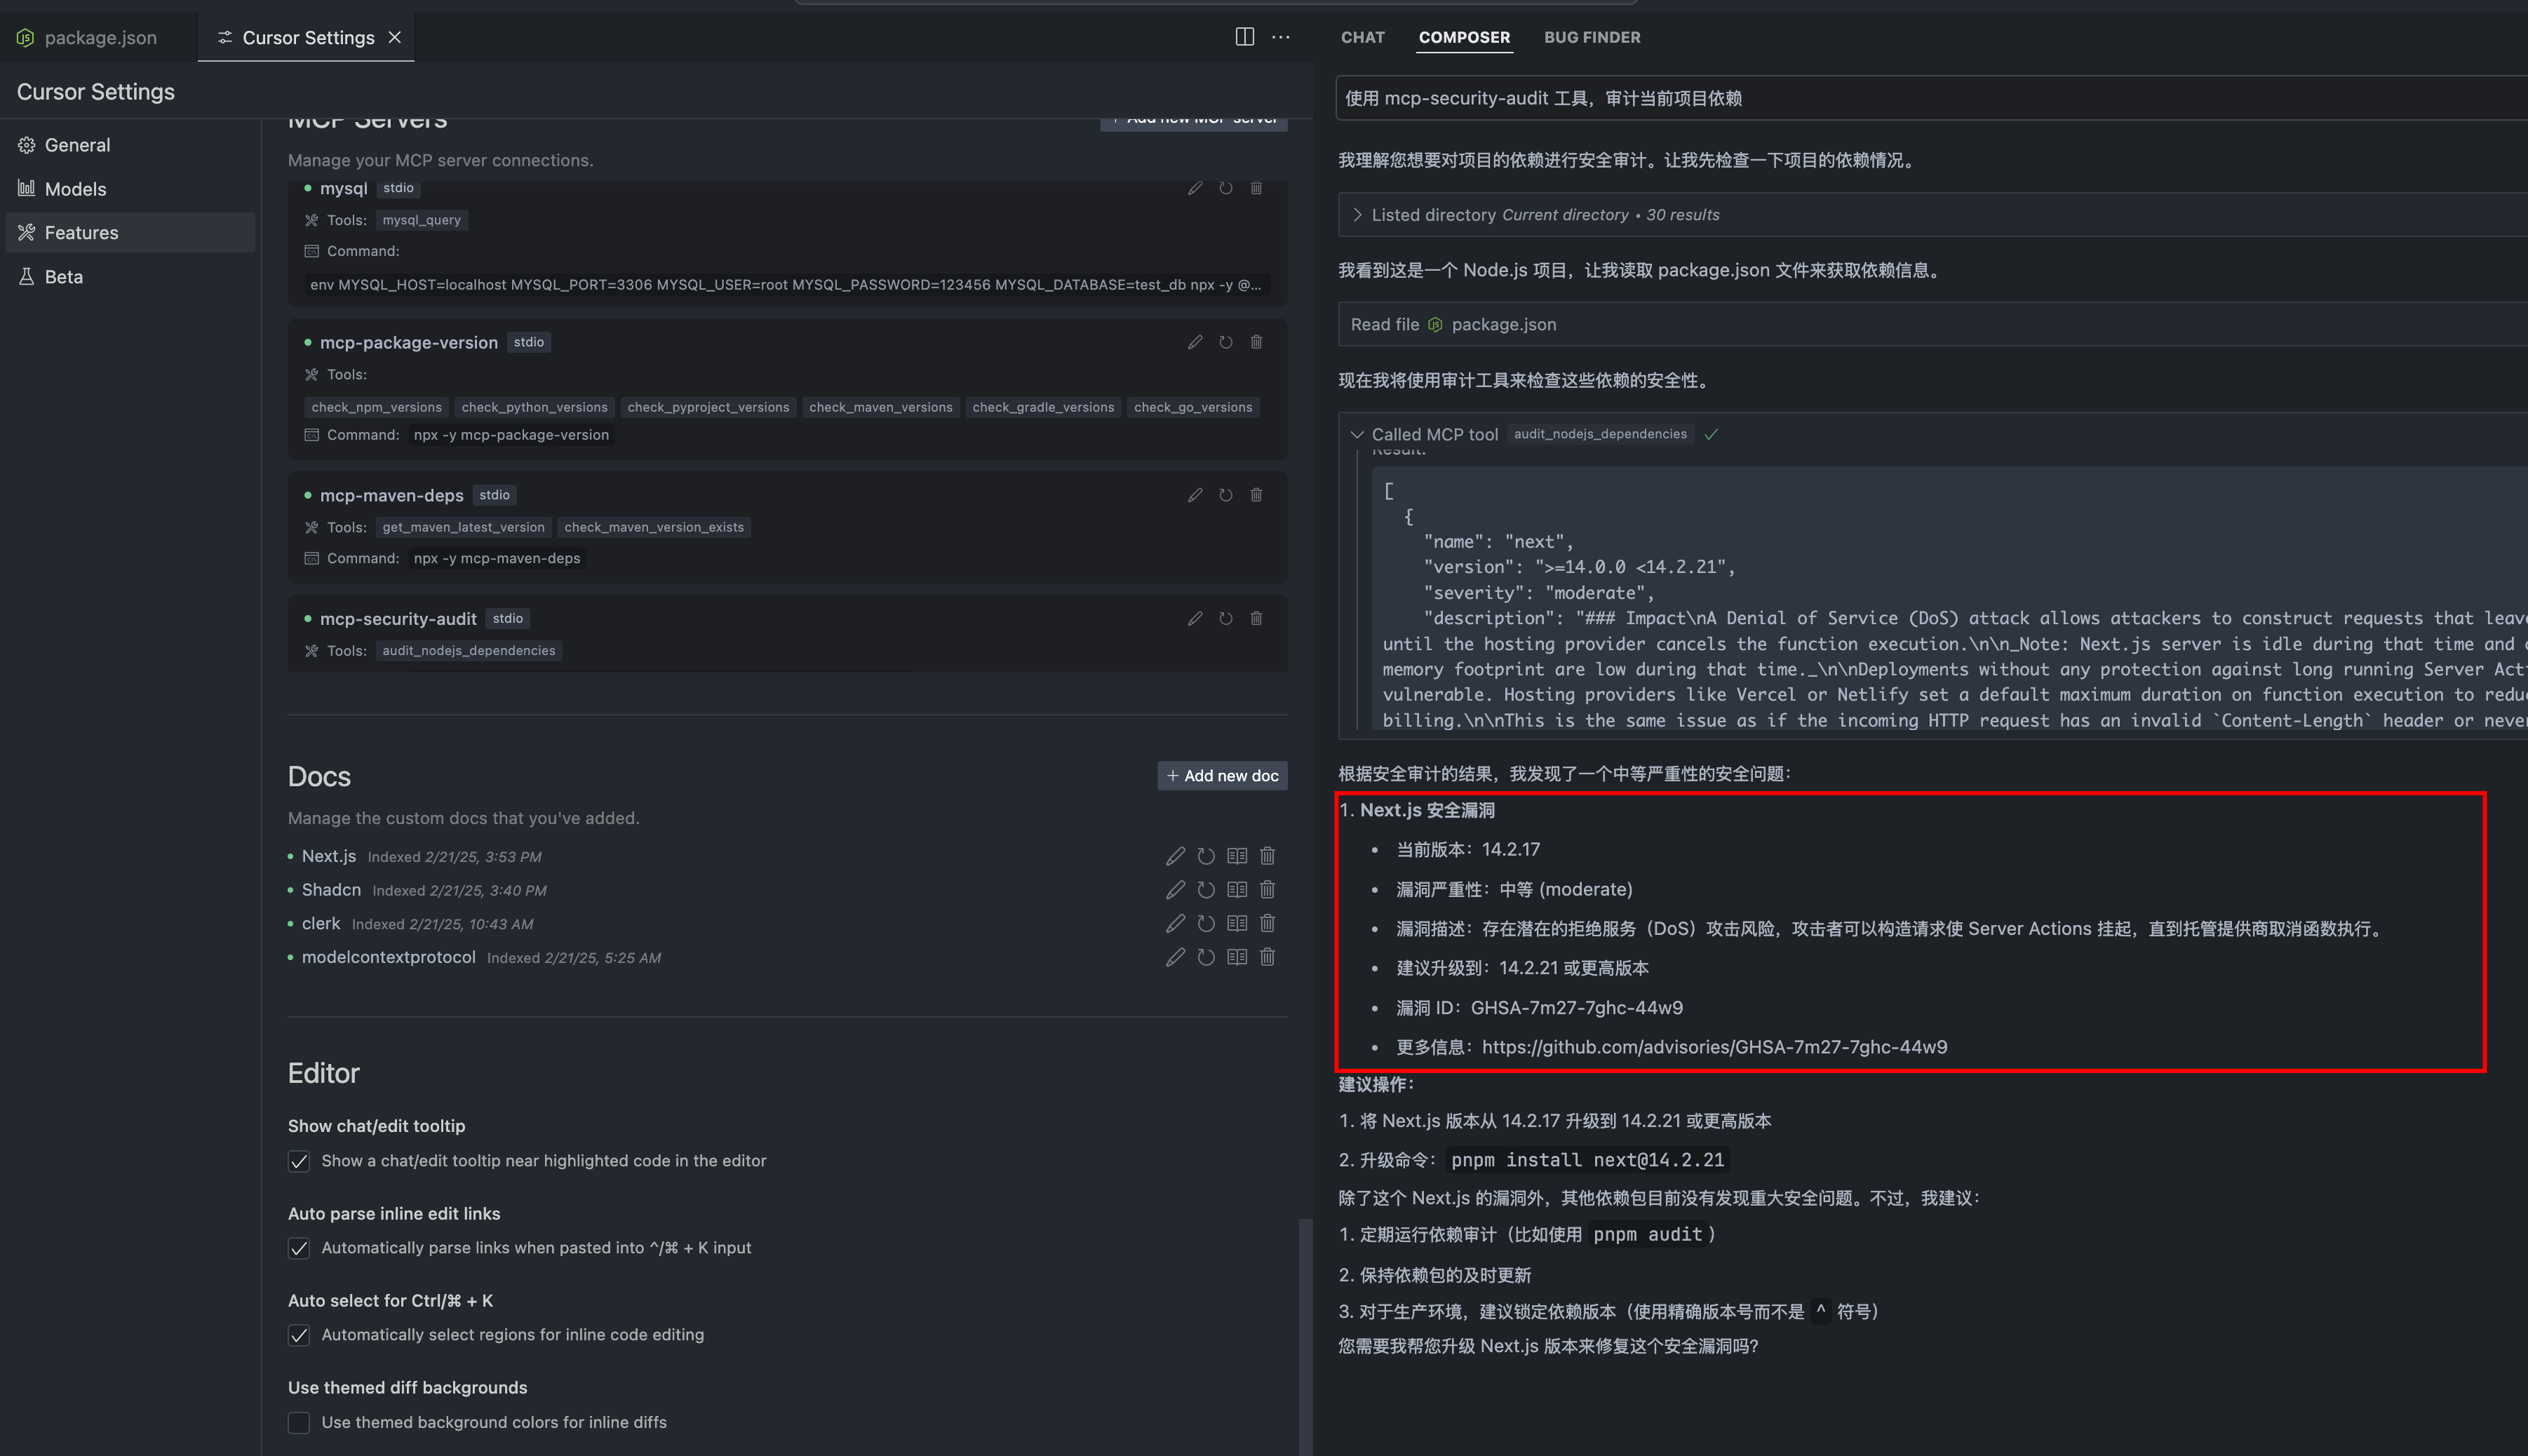
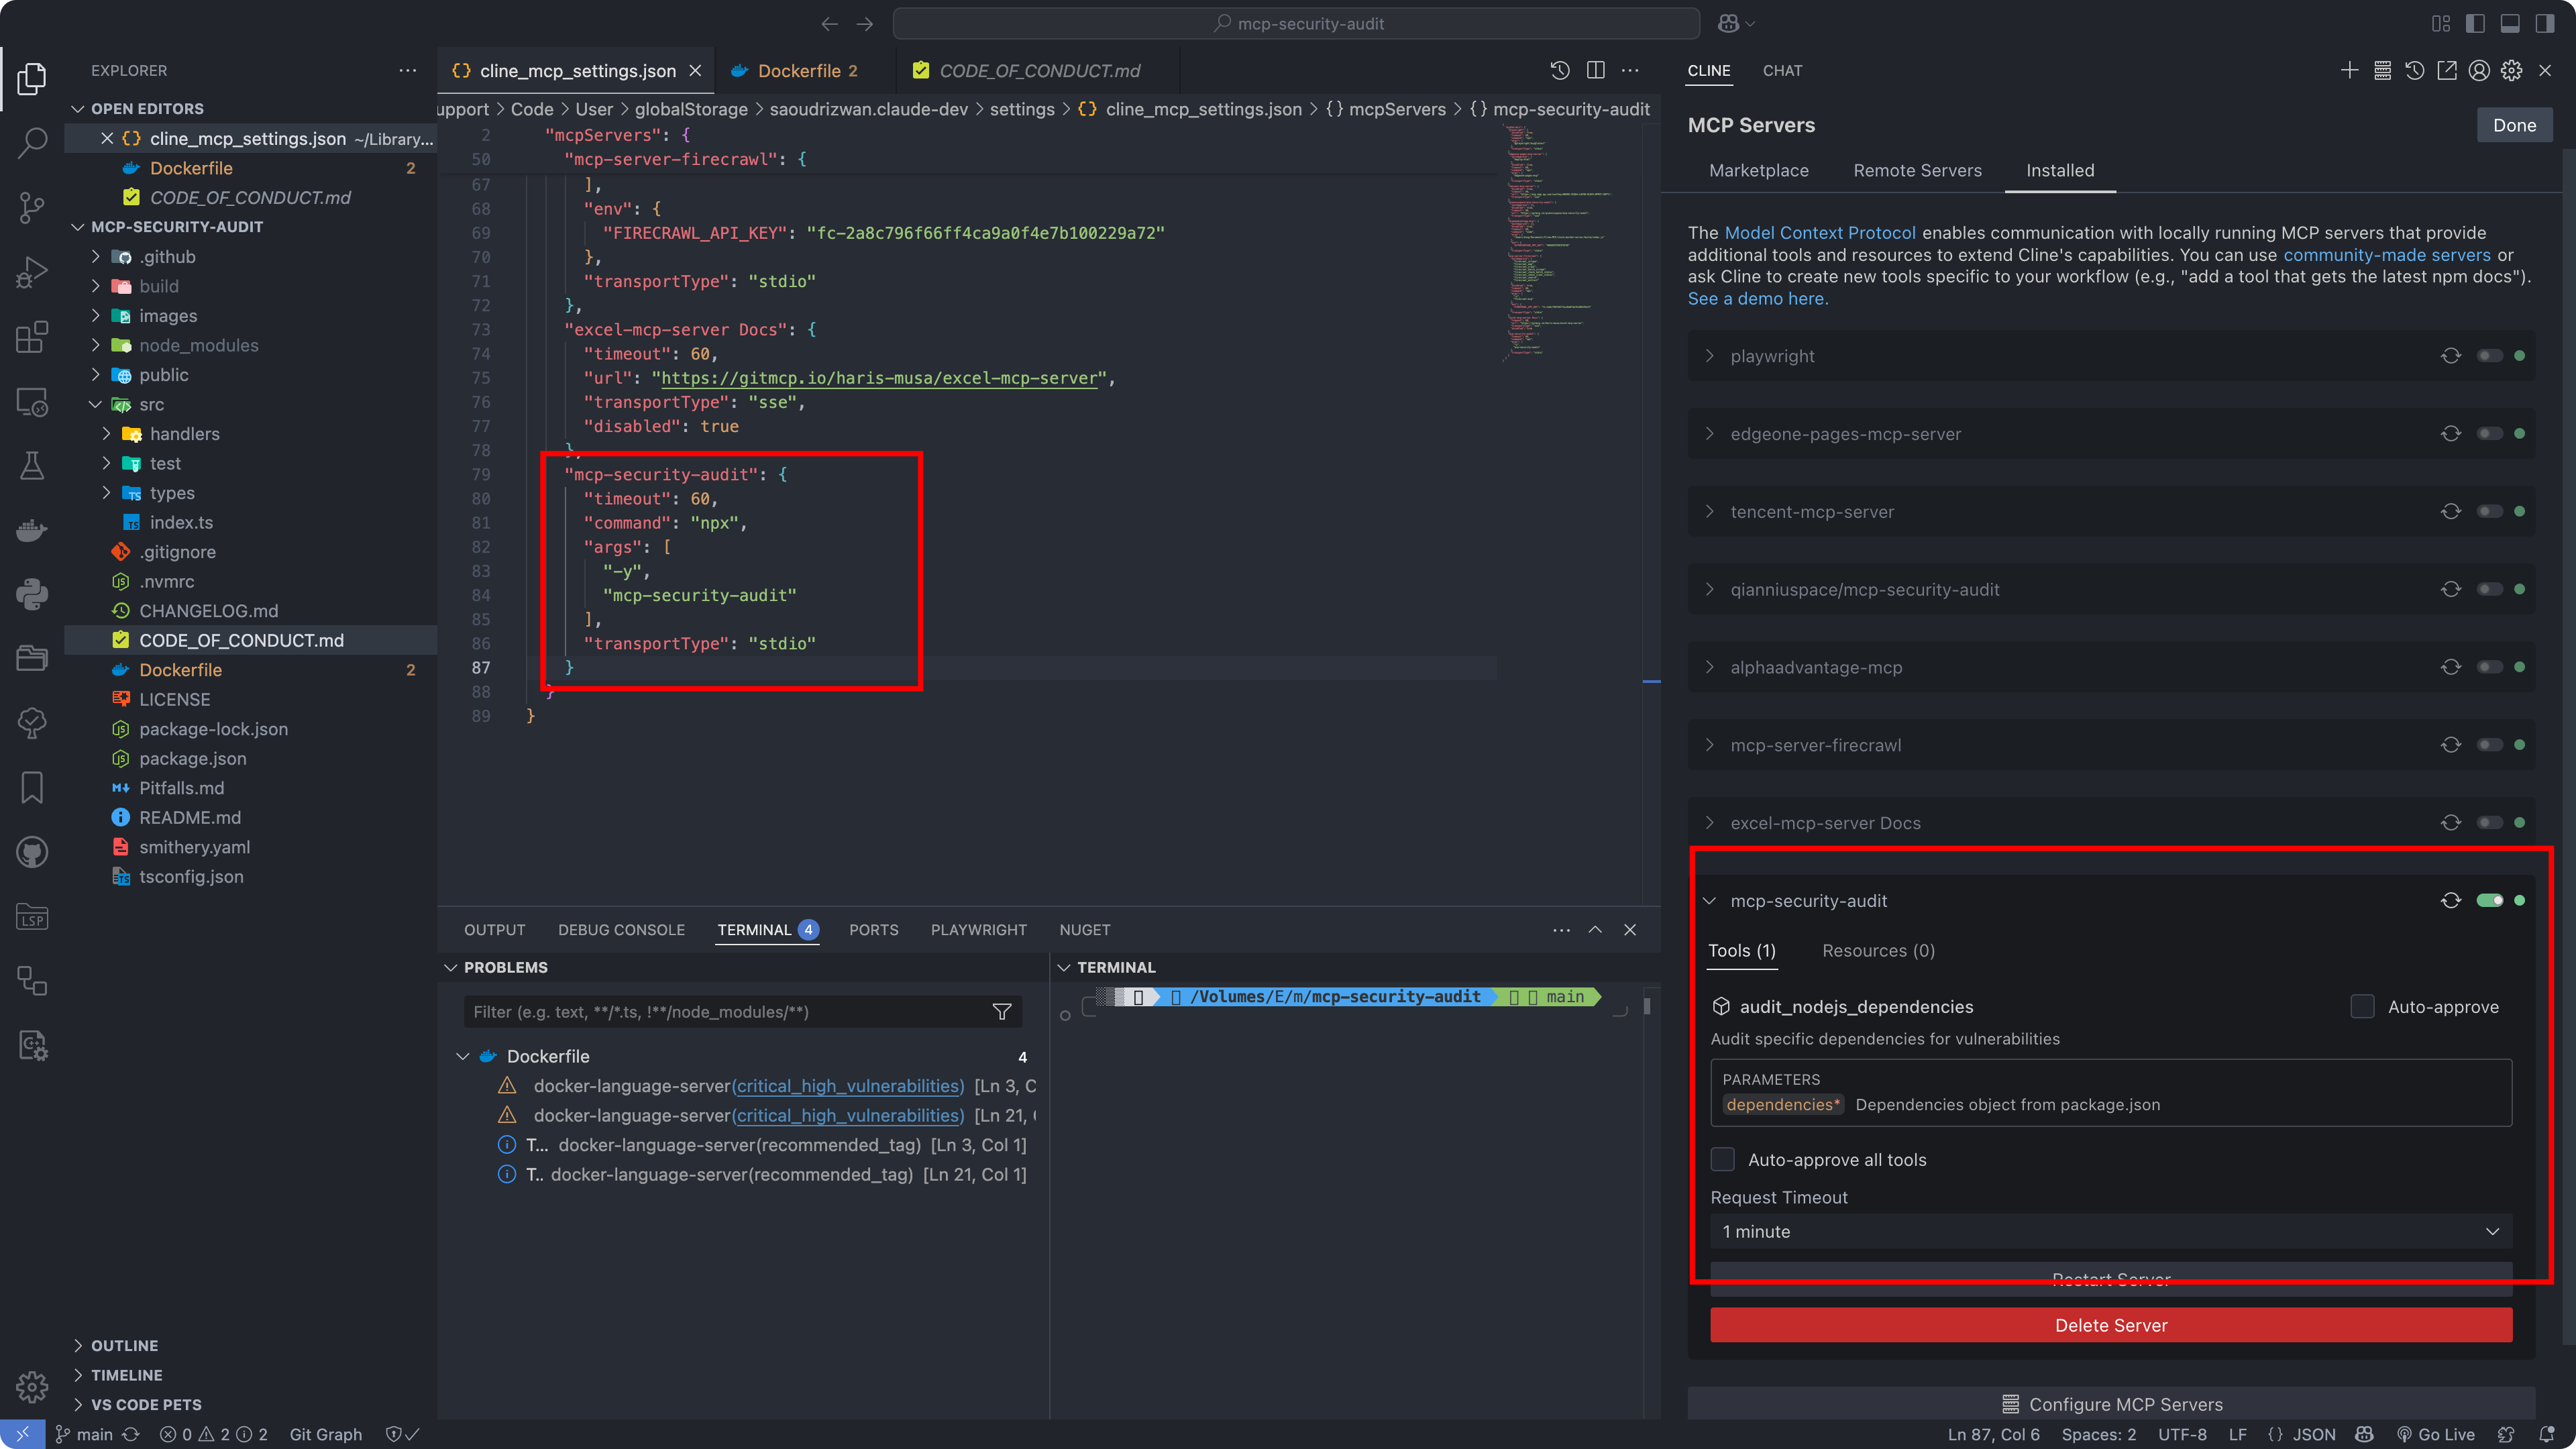
The tool provides detailed vulnerability information including severity levels, fix recommendations, CVSS scores, and CVE references.
{
  "content": [{
    "vulnerability": {
      "packageName": "lodash",
      "version": "4.17.15",
      "severity": "high",
      "description": "Prototype Pollution in lodash",
      "cve": "CVE-2020-8203",
      "githubAdvisoryId": "GHSA-p6mc-m468-83gw",
      "recommendation": "Upgrade to version 4.17.19 or later",
      "fixAvailable": true,
      "fixedVersion": "4.17.19",
      "cvss": {
        "score": 7.4,
        "vector": "CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N"
      },
      "cwe": ["CWE-1321"],
      "url": "https://github.com/advisories/GHSA-p6mc-m468-83gw"
    },
    "metadata": {
      "timestamp": "2024-04-23T10:00:00.000Z",
      "packageManager": "npm"
    }
  }]
}
{
  "content": [{
    "vulnerability": null,
    "metadata": {
      "timestamp": "2024-04-23T10:00:00.000Z",
      "packageManager": "npm",
      "message": "No known vulnerabilities found"
    }
  }]
}
For development reference, check the example response files in the public directory:
Note: The example responses shown above are transformed from the raw npm audit API responses to provide a more structured format. The original npm audit API responses contain additional metadata and may have a different structure.
Contributions are welcome! Please read our Contributing Guide for details on our code of conduct and the process for submitting pull requests.
This project is licensed under the MIT License - see the LICENSE file for details.
ESX ([email protected])
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
{ "mcpServers": { "qianniuspace-mcp-security-audit": { "command": "npx", "args": [ "-y", "@iflow-mcp/[email protected]" ] } }}Outils
Pas encore de liste d'outils. Les serveurs distants en obtiennent une après le premier contrôle d'état.
FAQ
Copiez sur cette page la configuration stdio pour Cursor, Claude Desktop, Claude Code ou VS Code. Elle utilise l'installation de l'éditeur, pas un proxy PlugMCP.
Aucune variable d'environnement requise n'est indiquée sur cette fiche.
MCP Security Audit s'exécute en local via stdio.
Dernière vérification : 2026-10-27. A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.