Local-first security scanner, MCP protocol inspector, dynamic fuzzer, Docker sandbox, and report generator for servers.
에이전트 강화
게시자가 제공하는 설치 방식입니다. PlugMCP 엔드포인트가 아닙니다.
원격 URL인가요, 내 컴퓨터에서 실행하는 명령인가요? 두 설치 방식의 차이
PlugMCP에서 실행
A new server you create. It is not this listing's official endpoint. Use the publisher install when you want their URL and their credentials.
실행
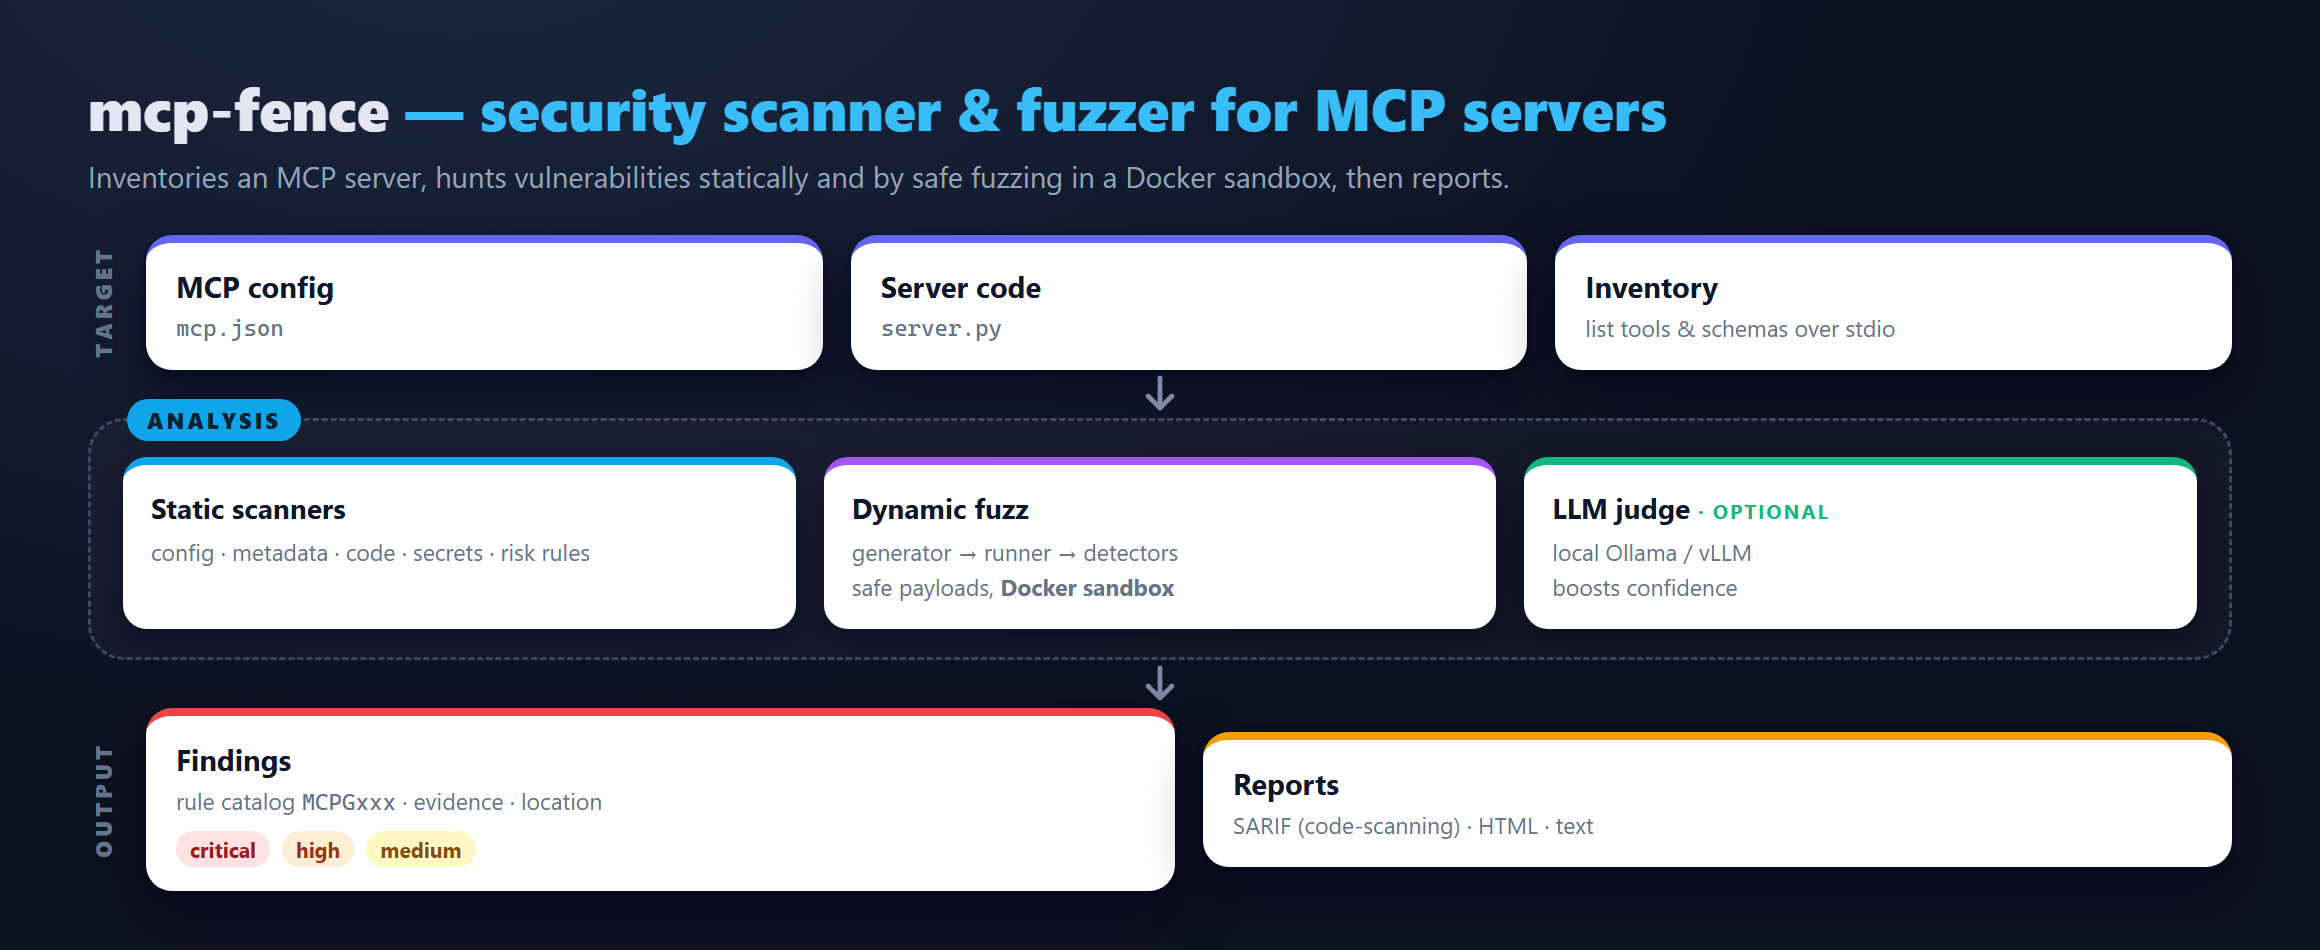
mcp-fence is a developer tool. Point it at your mcp.json (or any
running MCP server you wrote) and it will:
initialize,
tools/list, gathers schemas/annotations.--toy-mode or --allow-unsafe.strict, filesystem-readonly, network-deny, dev).It is non-destructive, local-first, and uses no cloud LLM by default. An optional local-LLM judge can talk to a local Ollama or OpenAI-compatible endpoint.
From PyPI:
pip install mcp-fence
From source (for contributors):
git clone https://github.com/DaoyuanLi2816/mcp-fence
cd mcp-fence
python -m venv .venv
source .venv/bin/activate          # Windows: .venv\Scripts\activate
python -m pip install -e ".[dev]"
Requires Python 3.11+.
# 1. Bring up the bundled examples in your working directory.
mcp-fence init-example ./mcp-fence-examples

# 2. Static scan the intentionally poisoned metadata server.
mcp-fence scan mcp-fence-examples/vulnerable_metadata_server/mcp.json

# 3. Live-inspect the safe baseline.
mcp-fence inspect mcp-fence-examples/safe_server/mcp.json

# 4. Fuzz the arbitrary-file-read server.
mcp-fence fuzz mcp-fence-examples/vulnerable_filesystem_server/mcp.json

# 5. Generate a `docker run` command that sandboxes any of the above.
mcp-fence sandbox mcp-fence-examples/vulnerable_filesystem_server/mcp.json \
    --profile strict --dry-run

# 6. Turn a saved JSON result into an offline HTML report.
mcp-fence scan mcp-fence-examples/vulnerable_metadata_server/mcp.json \
    --format json --output /tmp/scan.json
mcp-fence report /tmp/scan.json --format html --output /tmp/scan.html
mcp-fence 0.1.2 :: scan :: target=mcp-fence-examples/vulnerable_metadata_server/mcp.json
  summary: total=1 score=7/100 verdict=FAIL
  by_severity: high=1
  by_category: secrets=1

# Findings
  SEV   RULE     TITLE                    CATEGORY  WHERE                    DETAIL
  HIGH  MCPG006  Plaintext secret in env  secrets   param=OPENAI_API_KEY     Environment variable `OPENAI_API_KEY` appears to contain a plaintext secret.
Full catalog in docs/rule_catalog.md. Highlights:
Iist_files vs
list_files).shell=True, curl | sh, sudo,
/var/run/docker.sock, --privileged, references to ~/.ssh,
~/.aws.0.0.0.0 + no auth, HTTP without bearer.additionalProperties,
high-risk param names (command, path, url, webhook, …)
without pattern/enum/maxLength.shell=True, os.system), use of
eval/exec, unsafe deserialization (pickle, unsafe yaml.load),
disabled TLS verification, hard-coded secrets.MCP server output flows directly into an LLM's context. Anything in a tool's description, name, or response can be interpreted by the assistant as instructions:
General-purpose SAST / npm-audit / pip-audit don't model any of this. mcp-fence has rules and fuzzers built specifically for it.
echo MCPG_FUZZ_MARKER_8f2a. No rm, mv, chmod, or destructive
primitives are ever emitted.--llm-judge talks to a local
endpoint only.fake_secret.txt inside the bundled examples or any explicit
--traversal-target. They never aim at /etc/shadow or ~/.ssh/.--allow-unsafe is an explicit safety hatch for use inside the
mcp-fence sandbox Docker profile. See SECURITY.md and
docs/sandboxing.md.
For semantic suspiciousness scoring on tool descriptions, enable the optional judge:
ollama pull qwen3:8b
mcp-fence scan mcp-fence-examples/vulnerable_metadata_server/mcp.json \
    --inspect --llm-judge ollama --llm-model qwen3:8b
Sized for a 16 GB GPU (e.g. RTX 4080). Failures are silent: the core
scan completes either way. See docs/local_llm.md.
Drop .github/workflows/mcp-fence.yml
into any repo with an mcp.json. It discovers every mcp.json,
.mcp.json, and claude_desktop_config.json in the repo, merges their
findings into a single SARIF run, and uploads it to GitHub's code
scanning dashboard.
For a single known config path, a minimal equivalent looks like:
- name: install mcp-fence
  run: pip install mcp-fence
- name: scan
  run: mcp-fence scan path/to/mcp.json --format sarif --output mcp-fence.sarif
- uses: github/codeql-action/upload-sarif@v3
  with:
    sarif_file: mcp-fence.sarif
    category: mcp-fence
mcp-fence scan mcp-fence-examples/vulnerable_metadata_server/mcp.json
mcp-fence inspect mcp-fence-examples/safe_server/mcp.json
mcp-fence fuzz mcp-fence-examples/vulnerable_filesystem_server/mcp.json
mcp-fence sandbox mcp-fence-examples/vulnerable_shell_server/mcp.json --profile strict --dry-run
mcp-fence report /tmp/scan.json --format html --output /tmp/scan.html
See docs/roadmap.md. v0.2 adds AST-based source
scanning, HTTP/SSE live inspector, a local SSRF capture server, and a
pre-trained tool-poisoning classifier.
Apache-2.0. See LICENSE.
Local-first security scanner, MCP protocol inspector, dynamic fuzzer, Docker sandbox, and report generator for Model Context Protocol servers.
도구
아직 도구 목록이 없습니다. 원격 서버는 첫 상태 확인 후에 도구 목록이 생깁니다.
FAQ
이 페이지에서 Cursor, Claude Desktop, Claude Code 또는 VS Code용 stdio 설정을 복사합니다. PlugMCP 프록시가 아니라 게시자의 설치 방식을 사용합니다.
이 레코드에는 필수 환경 변수가 등록되어 있지 않습니다.
MCP Fence은(는) stdio를 통해 로컬에서 실행됩니다.
마지막 확인: 2026-10-27. Local-first security scanner, MCP protocol inspector, dynamic fuzzer, Docker sandbox, and report generator for Model Context Protocol servers.
