A comprehensive toolkit to guide GitHub Copilot toward secure coding practices. This project includes customizable instructions and security-focused prompts to help development teams identify and mitigate security risks effectively.
✨ A customizable copilot-instructions.md ruleset & prompts to guide GitHub Copilot toward secure coding defaults in Java, Node.js, C# and Python. Blocks risky patterns, teaches safe habits.
2026-10-27
Estrelas
43
Ferramentas
—
Disponibilidade
—
Designed for security-conscious teams, this configuration ensures Copilot suggests safer code patterns, avoids common vulnerabilities, and reinforces best practices — all without disrupting your workflow.
🔐 What's Inside
This project offers:
Secure-by-default guidance for all languages (e.g., input validation, secret handling, safe logging).
Language-specific secure patterns:
☕ Java
🟩 Node.js
🟦 C#
🐍 Python
"Do Not Suggest" lists to block risky Copilot completions (e.g., eval, inline SQL, insecure deserialization).
AI hallucination protections to prevent package spoofing, non-existent APIs, and misinformation risks.
Mentorship-style tips to help newer engineers build secure coding habits.
Custom agents & Agent Skills under agents/ and skills/ for repeatable AppSec workflows inside Copilot.
An installable GitHub Copilot CLI plugin under plugins/copilot-security for reusable AppSec agents and skills across projects.
An MCP server for seamless integration of these prompts into other projects.
🗂️ Prompt Catalogue
Explore the available prompts and their intended use cases:
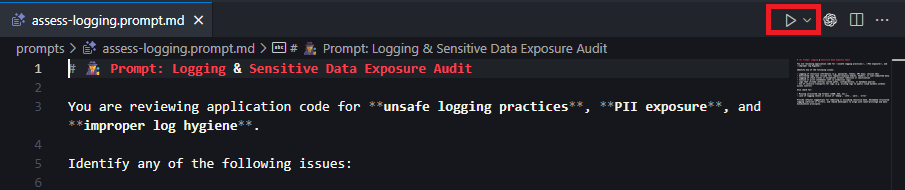
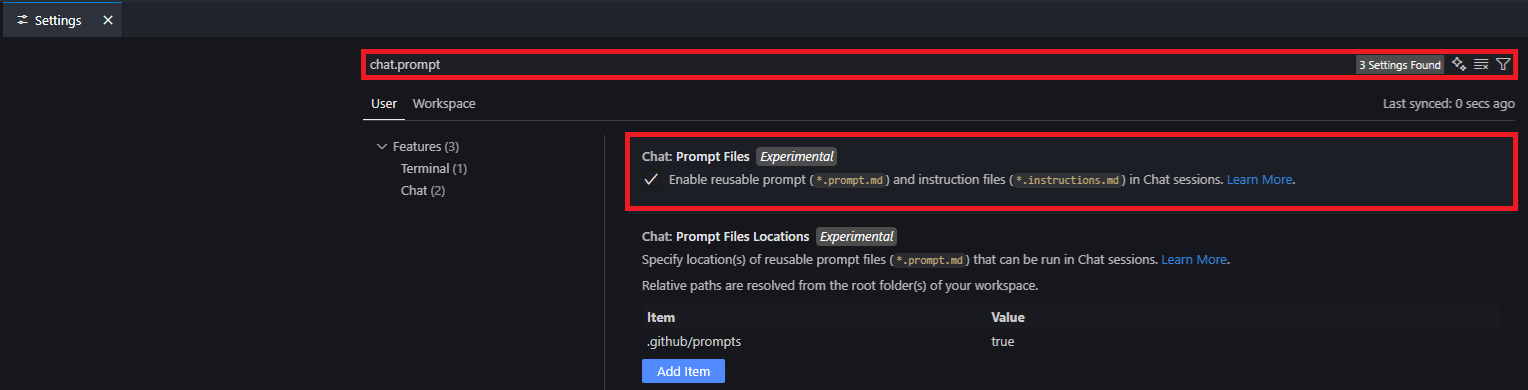
These prompt files live under prompts/ in this repo and are intended to be copied into a consuming repository’s .github/prompts/.
Recommended workflow: start with the application-security-orchestrator agent (see agents/application-security-orchestrator.agent.md).
It standardizes intake, then hands off to specialist agents (Analyst/Architect/Engineer) depending on whether you want findings, a threat model, or implemented fixes.
Triage a known CVE against a project's dependency: explain the exploit, assess reachability and configuration, and produce a structured Dependency Tracker report.
Analyze a specific CVE's impact on local code, determine exploitability, and generate a concise triage report.
Locate the copilot-instructions-mcp server, click the settings cog, and select start server.
Using MCP with GitHub Copilot
Open GitHub Copilot Chat.
Ask it to run any of the prompts against your repository or specific files.
Example:Please get and run the secure code review prompt.
Option 3: Using the copilot-security GitHub Copilot CLI Plugin
This repository ships an installable GitHub Copilot CLI plugin named copilot-security.
Plugins are reusable bundles of Copilot components such as agents, skills, hooks, and integrations. In this project, the plugin is published from the official marketplace repository:
robotti-io/copilot-security-instructions
The plugin manifest lives under plugins/copilot-security/.github/plugin/plugin.json, and the marketplace manifest for this repository lives under .github/plugin/marketplace.json.
What the plugin contains
The copilot-security plugin currently packages these reusable components:
Agents:
application-security-analyst
application-security-architect
Skills:
access-control-review
dependency-cve-triage
threat-model
After installation, these agents and skills are available in any project where you use GitHub Copilot CLI.
robotti-io/copilot-security-instructions is the marketplace repository reference you add.
copilot-security-instructions is the marketplace name exposed by this repository's marketplace.json.
copilot-security is the plugin name exposed by plugins/copilot-security/.github/plugin/plugin.json.
Install directly from the repository
If you do not want to register the marketplace first, you can install the plugin directly from this repository by pointing Copilot CLI at the plugin subdirectory:
Launches the MCP server on http://localhost:8080/mcp.
npm run dev
Starts the server with live reload via nodemon.
npm run lint
Runs ESLint and Markdownlint to verify code and docs.
npm run lint:fix
Attempts to automatically fix linting issues.
Recommended workflow: Run npm run lint (and npm run lint:fix if needed) before committing or opening a PR.
📣 Feedback & Contributions
This project is community-friendly and designed for continuous improvement.
If you have suggestions, feedback, or language rules to contribute — feel free to open an issue or PR.
Let’s make Copilot safer, one suggestion at a time. 🛠️
Disclaimer
This repository, including all instructions, prompts, agents, examples, and related application content,
is provided “AS IS”, without warranties or conditions of any kind, express or implied, including without
limitation warranties of merchantability, fitness for a particular purpose, noninfringement, security,
accuracy, completeness, or regulatory compliance.
Use of this repository is at your own risk. Robotti and its contributors shall not be liable for any claims,
damages, losses, or other liability arising from or related to the use, misuse, or inability to use this
repository or any outputs produced from it.
C
Copilot Security Instructions
Robotti-io·43 estrelas·
✨ A customizable copilot-instructions.md ruleset & prompts to guide GitHub Copilot toward secure coding defaults in Java, Node.js, C# and Python. Blocks risky patterns, teaches safe habits.
Ainda não há lista de ferramentas. Servidores remotos recebem uma após a primeira verificação de saúde.
Perguntas frequentes
Perguntas
Como instalo Copilot Security Instructions?
Copie nesta página a configuração stdio para Cursor, Claude Desktop, Claude Code ou VS Code. Ela usa a instalação do publicador, não um proxy do PlugMCP.
Copilot Security Instructions precisa de uma chave de API?
Este registro não lista nenhuma variável de ambiente obrigatória.
Qual transporte Copilot Security Instructions usa?
Copilot Security Instructions roda localmente via stdio.
Quando Copilot Security Instructions foi verificado pela última vez?
Última verificação: 2026-10-27. ✨ A customizable copilot-instructions.md ruleset & prompts to guide GitHub Copilot toward secure coding defaults in Java, Node.js, C# and Python. Blocks risky patterns, teaches safe habits.