as
Auth infrastructure for coding agents — user pools, secrets vault, token management. As easy as git.
接入你的智能体
發布者自己的指令。不是 PlugMCP 端點。
用我們的金鑰與日誌託管一份副本。
npx -y [email protected]Claude Code 沒有本機指令的安裝連結。複製下方指令並在終端機中執行。
claude mcp add authshore -- npx -y authshore@1.0.4在終端機中執行。
{ "mcpServers": { "authshore": { "command": "npx", "args": [ "-y", "[email protected]" ] } }}claude_desktop_config.json
遠端 URL 還是本機指令? 兩種安裝方式的差異
Your agent can scaffold a whole app in an afternoon — then stalls the moment it needs auth. It hardcodes secrets into .env files it later commits, rolls its own JWT handling, and leaves you wiring up Cognito by hand. AuthShore is the auth layer your agent runs itself: one install, and it provisions user pools, stores secrets encrypted, and mints, validates and refreshes tokens — from the terminal, with no console to click through.
Works with: Claude Code · Cursor · Cline · Windsurf · Aider · Codex · any MCP client
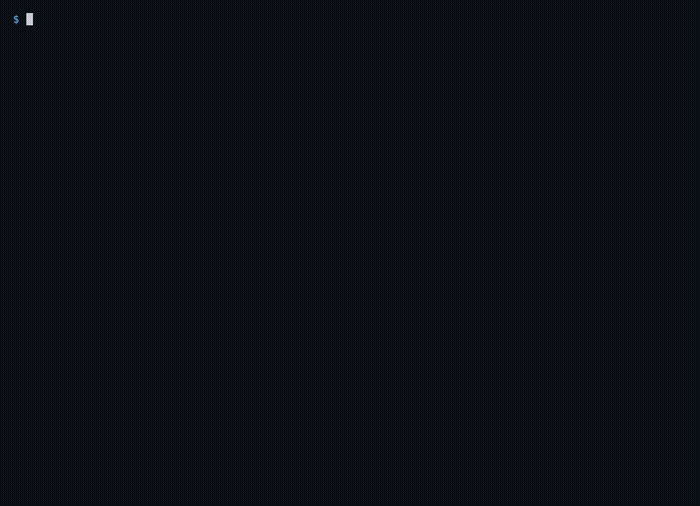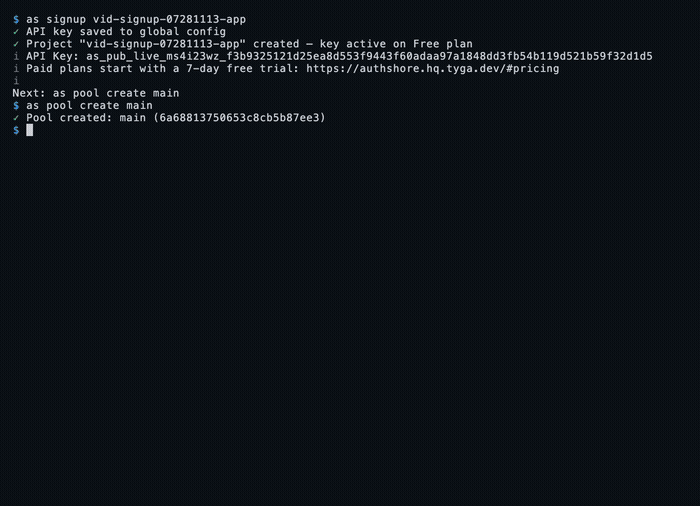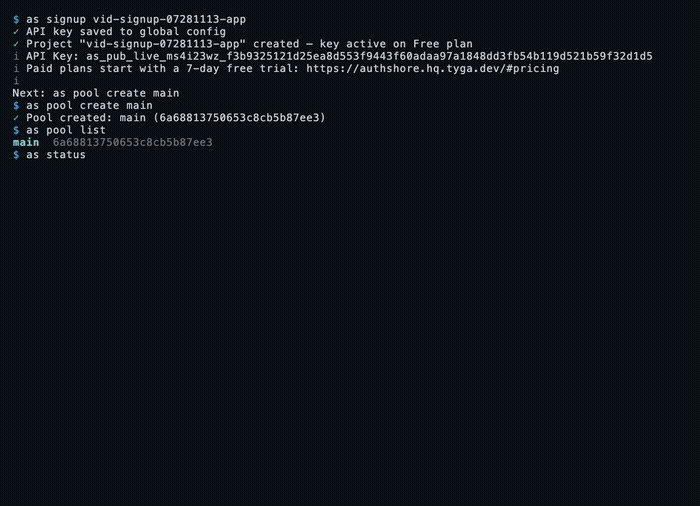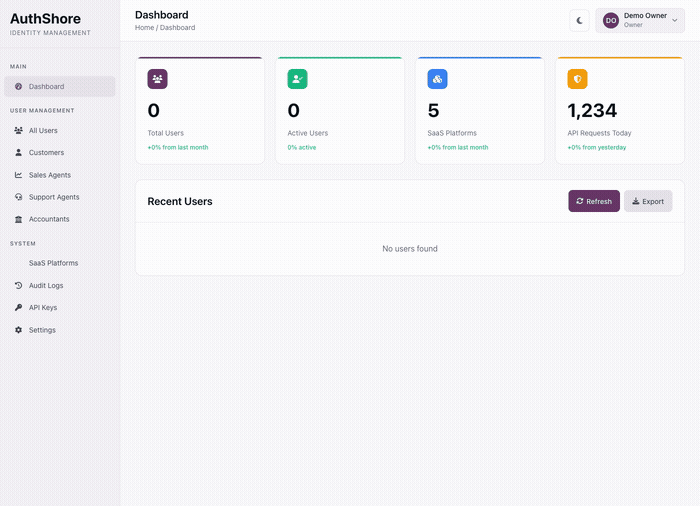
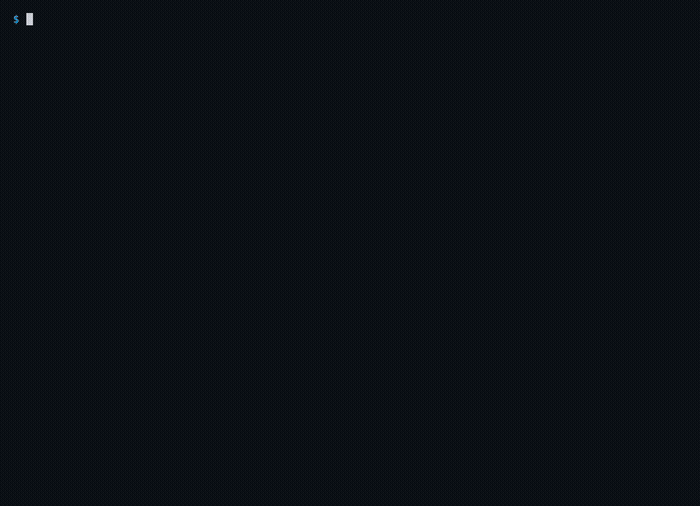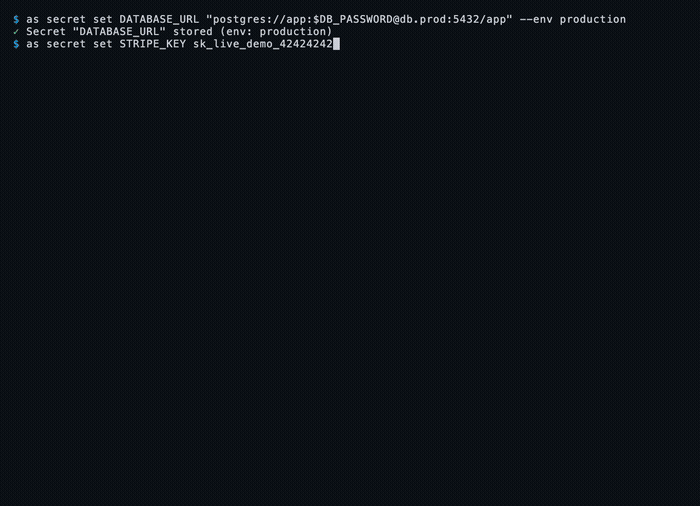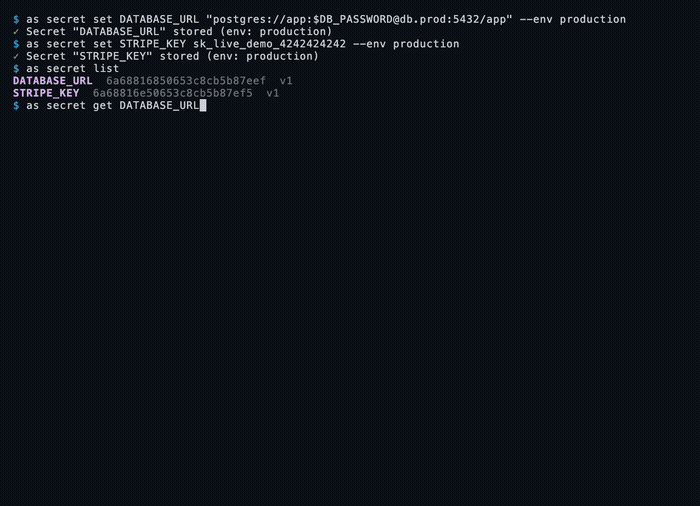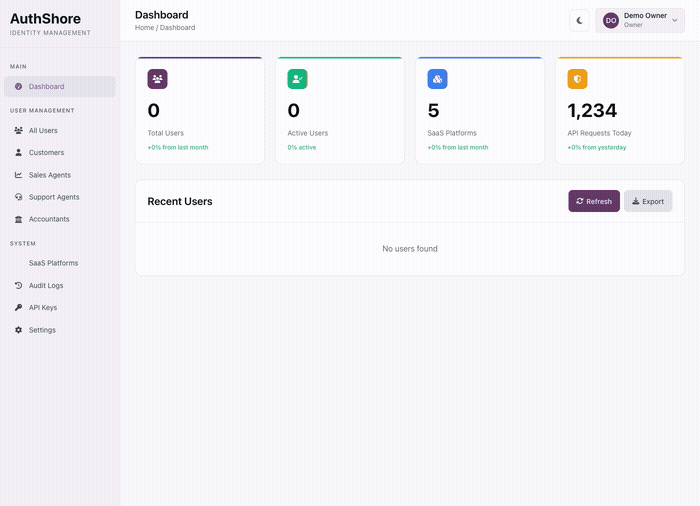
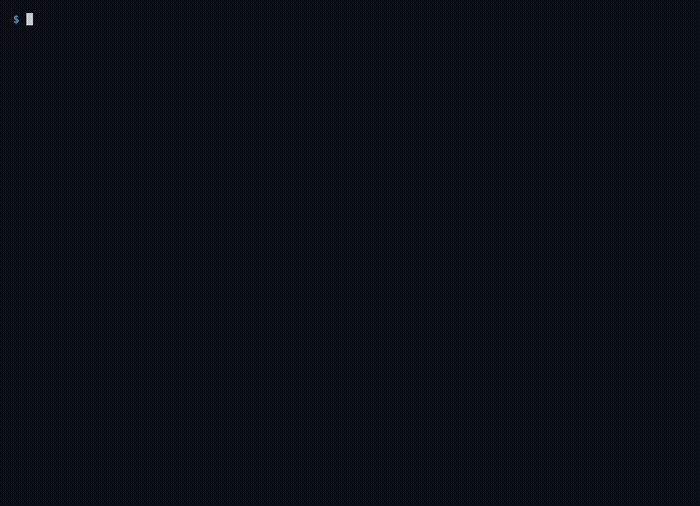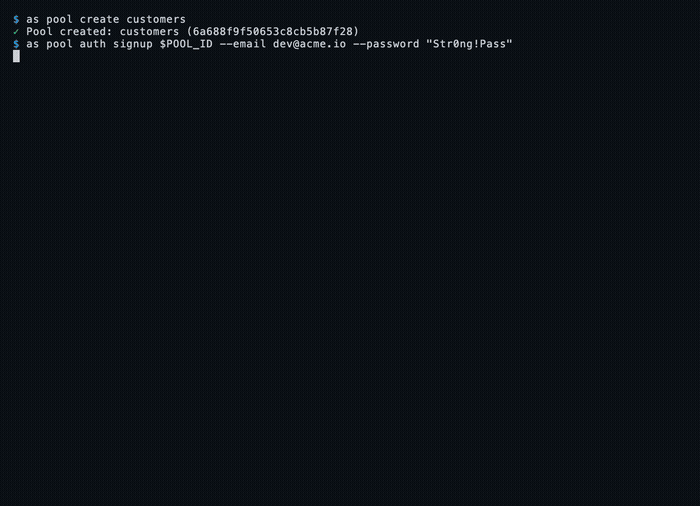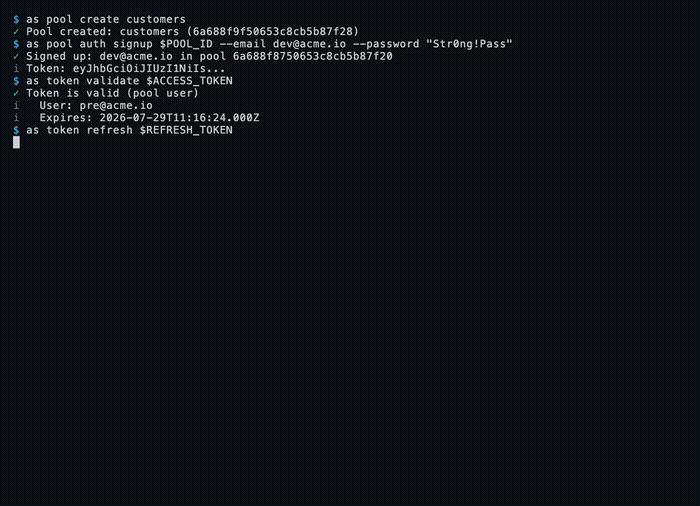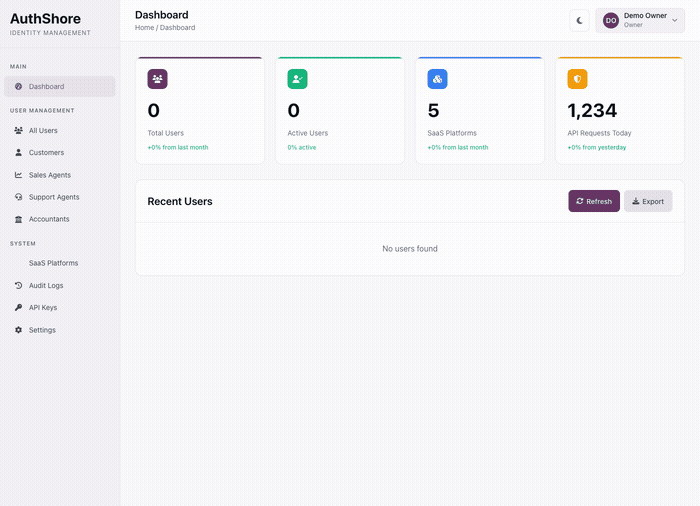
Real terminal sessions against the live API — click a GIF for the full video.
| Zero to auth in 60s | Secrets vault | Tokens & pools |
|---|---|---|
 |  |  |
More demos: authshore.ai/#demo
npm install -g authshore
The npm package is authshore; the command is as.
# 1. Create a project — free plan, API key active immediately, no card
as signup my-project --email [email protected] --local

# 2. Create a user pool
as pool create main

# 3. Store a secret (encrypted at rest, versioned)
as secret set DATABASE_URL "postgres://user:pass@host:5432/db"

# 4. Sign up a user in your pool
as pool auth signup main --email [email protected] --password SecurePass123!

# Full reference
as help
Every project gets isolated user pools your agent manages from the terminal: create pools, add users, run full signup/signin flows that return real JWT pairs.
as pool create main                      # create a pool
as pool list                             # list pools
as pool users <id>                       # list users in a pool
as pool user add <id> --email E --password P
as pool auth signup <id> --email E --password P   # returns access + refresh tokens
as pool auth signin <id> --email E --password P
Encrypted, versioned key-value storage scoped to your project. Your agent stores third-party keys once and reads them at deploy time — nothing sensitive left sitting in the repo.
as secret set STRIPE_KEY "sk_..." --env production
as secret get STRIPE_KEY                 # decrypted read
as secret list
as secret versions STRIPE_KEY            # full version history
as secret delete STRIPE_KEY
The JWT plumbing agents usually hand-roll, done right once.
as token validate <jwt>                  # verify signature + expiry, show claims
as token refresh <refresh-token>         # rotate the pair
as token revoke <token>                  # kill a compromised token
Prefer tools over a CLI? as ships an MCP server. Point Claude Code (or any MCP client) at it and your agent gets 18 native tools: pools, users, secrets, tokens, project status.
claude mcp add authshore --env AUTHSHORE_API_KEY=as_your_key_here -- as mcp-serve
For clients that use a JSON config (Cline, Cursor, Windsurf), pass your API key via the AUTHSHORE_API_KEY environment variable. The MCP server runs outside your project directory, so it will not pick up .authshore/config.json:
{
  "mcpServers": {
    "authshore": {
      "command": "as",
      "args": ["mcp-serve"],
      "env": { "AUTHSHORE_API_KEY": "as_your_key_here" }
    }
  }
}
No key yet? as signup my-project --email [email protected] provisions one in seconds — free plan, no card.
No CLI at all? Claude Web, Claude Desktop, Raycast, or any hosted MCP client can connect straight to our remote server. Same 18 tools, nothing to install:
URL:  https://mcp.authshore.ai/sse
Auth: Authorization: Bearer YOUR_API_KEY
No key? Connect without one: the remote server starts in onboarding mode with an authshore_signup tool that provisions your account and unlocks everything in the same session.
as mcp-serve) or fully remote (mcp.authshore.ai): Claude Code, Claude Web, Cursor, Raycast, any MCP client--json on every command for programmatic parsing.authshore/config.json, auto-loaded, gitignore-friendlyPricing: free plan with an instantly-active API key — no card, no trial clock. Paid plans (Starter $9 / Pro $29 / Scale $99 per month) come with a 7-day free trial via secure Stripe checkout. Details.
as login --key YOUR_KEY --local     # saves to .authshore/config.json (project-local)
as config                           # show active config
as me                               # identity check: which project am I?
API key is resolved in this order (highest priority first):
--key flagAUTHSHORE_API_KEY environment variable./.authshore/config.json (project-local)~/.authshore/config.json (global)Add .authshore/ to your .gitignore.
Add to your CLAUDE.md, .cursorrules, .clinerules, .windsurfrules, or AGENTS.md:
## Auth
This project uses AuthShore for auth: user pools, secrets, tokens.
Use the `as` CLI. Config is in .authshore/config.json (auto-loaded).
If not configured: as login --local --key YOUR_KEY
Run `as help` for the full command reference. Run `as me` before any writes.
Every agent-built app hits the same wall: auth. I watched my agents hardcode secrets, reinvent JWT refresh, and stall on Cognito consoles they can't click. So I built the auth layer the agent runs itself. It's early and I'm iterating fast: if something's rough or missing, open an issue — I read every one.
Proprietary - Tyga.Cloud Ltd. See LICENSE.
AuthShore CLI - auth infrastructure for coding agents. User pools, secrets vault, token management. As easy as git.
{ "mcpServers": { "authshore": { "command": "npx", "args": [ "-y", "[email protected]" ] } }}工具
尚無工具清單。遠端伺服器會在首次健康檢查後取得工具清單。
常見問題
在本頁複製適用於 Cursor、Claude Desktop、Claude Code 或 VS Code 的 stdio 設定。它使用發布者的安裝方式,而不是 PlugMCP 代理伺服器。
這筆記錄未列出必要的環境變數。
Authshore 透過 stdio 在本機執行。
上次檢查時間:2026-11-16。 AuthShore CLI - auth infrastructure for coding agents. User pools, secrets vault, token management. As easy as git.