MCPGoat
· open source, free to use and self-host.
🌐 Website: https://sabyasachidhal.github.io/MCPGoat/ ·
接入你的智能体
從發布者安裝。不是 PlugMCP 端點。
遠端 URL 還是本機指令? 兩種安裝方式的差異
來自發布者
· open source, free to use and self-host.
🌐 Website: https://sabyasachidhal.github.io/MCPGoat/ ·
Deliberately vulnerable MCP server (aka MCP Goat) for security training — 26 challenges across 4 difficulty levels (incl. a secure reference), a victim-agent harness, and one-command Docker deploy. Practice penetration testing against the Model Context Protocol.
MCPGoat (also written MCP Goat) is a deliberately vulnerable MCP server —
an insecure-by-design Model Context Protocol implementation for practicing MCP
penetration testing. Every challenge is implemented at three difficulty levels
(Easy / Moderate / Difficult) behind a tiered level switch, with a
capture-the-flag scoreboard. Runs over
Streamable HTTP; attack it with the bundled client, MCP Inspector, curl,
or Burp.
⚠️ Authorized training use only. Intentionally contains RCE, SSRF, SQLi, secret leakage, and more. Keep it on
127.0.0.1; ideally run it in a container. Never expose it to a network you don't own.
ℹ️ MCPGoat is an independent project — not affiliated with or endorsed by the WebGoat project, or any other similarly-named "vulnerable MCP" project.
Implements the Core set + three Extended batches from
DESIGN_PROMPT.md — 26 challenges × 3 levels = 78
distinct flags, exercising every major MCP primitive (tools, resources,
prompts, sampling) plus the HTTP transport layer. Each challenge also
has a 4th Secure level: the fixed, unexploitable reference where every
documented exploit fails (verify with npm run attack -- … secure).
All of these labs are worth your time. MCPGoat aims to be the deepest single target: the same flaw hardens across tiers, so you can progress from a first exploit to blind, multi-step chains — then verify the fix against the Secure level.
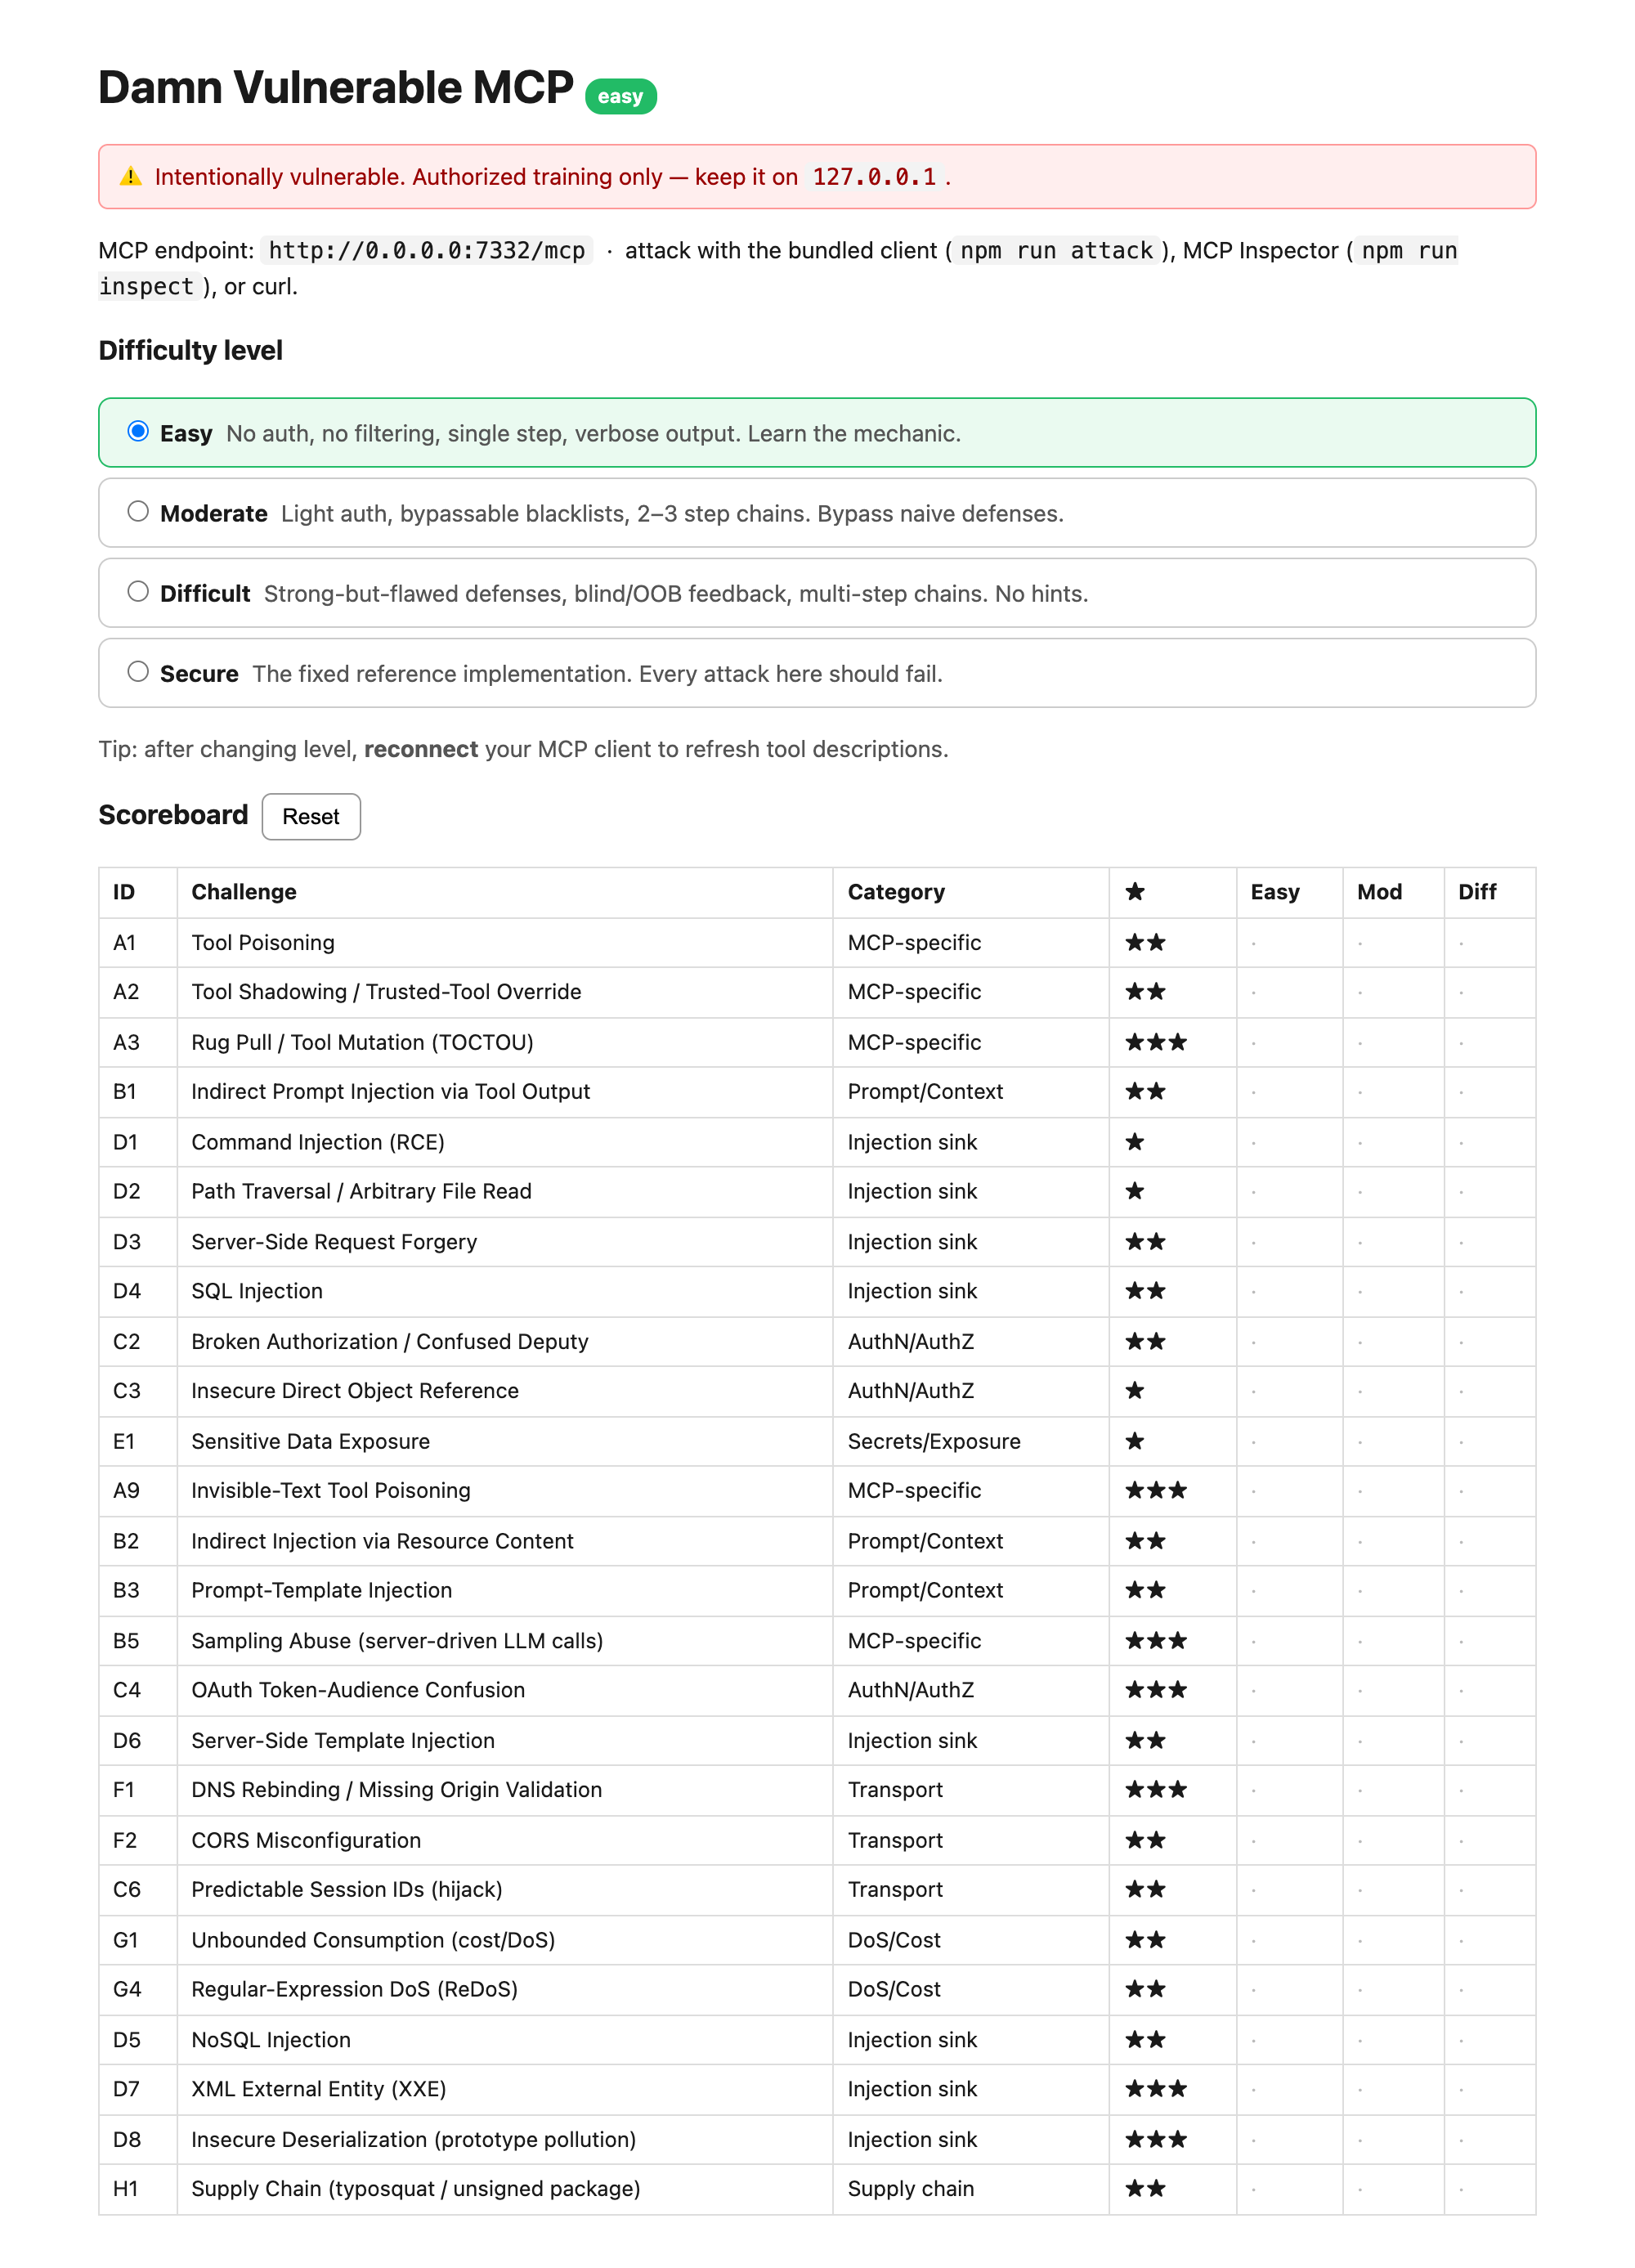
The control panel (http://127.0.0.1:7332) — pick a difficulty level and
track progress. This is config + progress
only; it is not the thing you attack.
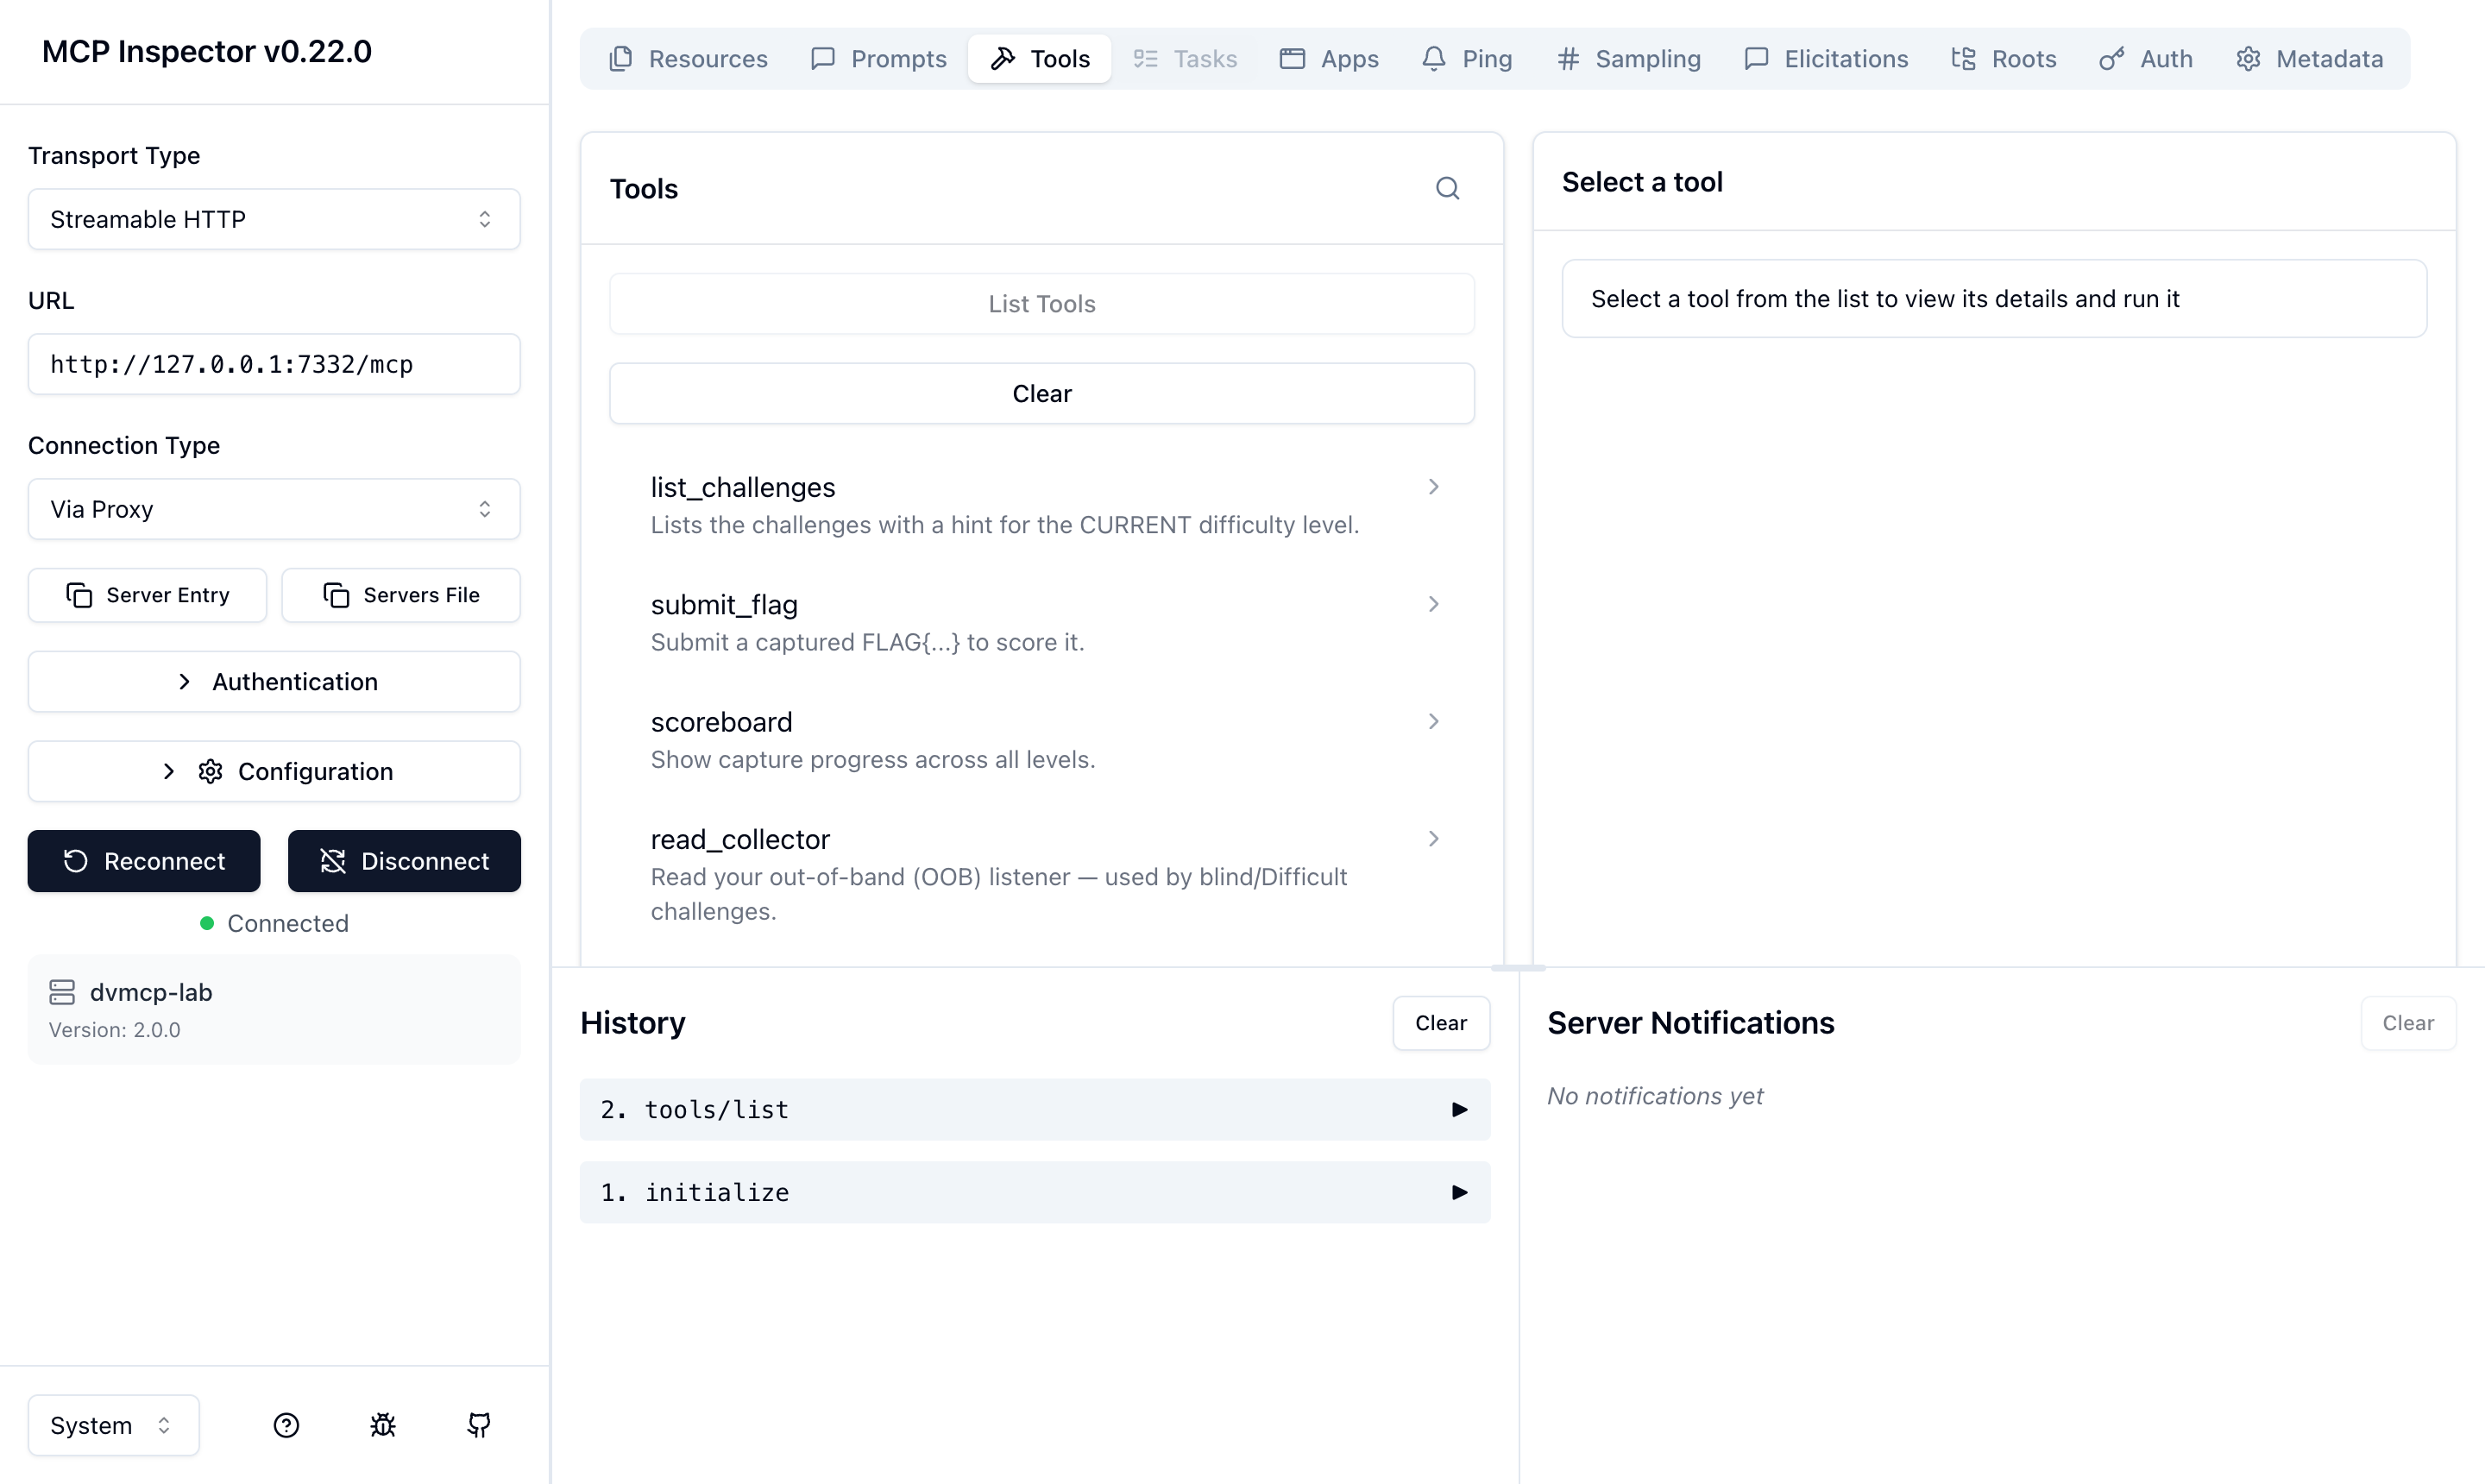
The actual attack surface is the MCP server itself — its tools, resources, prompts, and sampling calls. MCP servers have no human web UI; you interact as an MCP client. Here it is in MCP Inspector (the bundled attacker client and a real AI agent are the other two ways):
git clone https://github.com/SabyasachiDhal/MCPGoat.git
cd MCPGoat
docker compose up --build            # → http://127.0.0.1:7332
# or:
docker build -t mcpgoat .
docker run --rm -p 127.0.0.1:7332:7332 mcpgoat
The image is ~202 MB — a bare Alpine with just the node binary plus
curl/ping (for the RCE challenge); the server is esbuild-bundled to a single
~1.2 MB file, so the runtime carries no node_modules, npm, or
package.json. Runs as a non-root user. Keep the 127.0.0.1: in the port
mapping — -p 7332:7332 would expose the vulnerable server on every host
interface. Start at a level with -e MCPGOAT_LEVEL=difficult.
Requires Node 18+ (tested on Node 22/23/24; uses the built-in node:sqlite).
git clone https://github.com/SabyasachiDhal/MCPGoat.git
cd MCPGoat
npm install
npm start                 # serves http://127.0.0.1:7332   (tsx, no build step)
# or compiled:  npm run build && npm run serve
Open the control panel at http://127.0.0.1:7332 to pick a level and watch
the scoreboard. Start at a level directly with MCPGOAT_LEVEL=moderate npm start.
The same vulnerability hardens as you climb:
…and Secure — the fixed reference: strict validation, exact-match auth,
parameterized queries, no eval, Origin allow-lists, CSPRNG session IDs,
least-privilege tools. No flags here; the point is every attack fails. Confirm
with npm run attack -- http://127.0.0.1:7332/mcp secure (expect 22/22 blocked).
Selecting a level (any of these — all drive one shared state):
mcpgoat_set_level({ level })MCPGOAT_LEVEL=difficult npm startAfter changing level, reconnect your MCP client so tool descriptions refresh (matters for the tool-poisoning / shadowing challenges). Behavior changes take effect immediately.
Detects the current level and exploits every challenge at that level:
npm run attack                                  # current level
npm run attack -- http://127.0.0.1:7332/mcp all # run all three levels in sequence
npm run inspect
# Transport "Streamable HTTP", URL http://127.0.0.1:7332/mcp, Connect
See docs/EXPLOITS.http. Streamable HTTP needs
Accept: application/json, text/event-stream and a session id from the
initialize response header.
Flag capture proves an exploit exists. The victim agent proves impact — a real MCP-client agent, driven by an LLM, doing benign tasks while the lab's payloads manipulate it into calling tools it was never asked to and leaking secrets.
npm run agent                  # naive agent (mock brain, offline)  → 3/3 compromised
npm run agent -- --defended    # hardened agent, same attacks       → 0/3 compromised
MCPGOAT_AGENT_BACKEND=ollama OLLAMA_MODEL=llama3.1 npm run agent   # real local model
Three scenarios run against the easy level:
The --defended agent treats tool descriptions and results as untrusted
data (never instructions) and resists all three — the client-side counterpart
to the server-side Secure level. Backend is offline-first: a deterministic
mock brain by default (no install), or Ollama for a real local model.
Core set
Extended set (deepens MCP-primitive coverage)
Extended set — batch 2 (HTTP transport & resource abuse; solved via raw fetch/tools)
Extended set — batch 3 (more injection sinks & supply chain)
Each (challenge, level) pair has a unique flag FLAG{slug__level}. Capture it,
submit with the submit_flag tool, track progress with scoreboard (or the
control panel). Per-level hints: the list_challenges tool.
Full per-level walkthroughs + fixes: docs/SOLUTIONS.md.
;/& blocked → use |.
Difficult: most metacharacters blocked and blind → newline-chain a curl
that exfiltrates to the OOB collector, then read_collector.127.0.0.1/localhost string-blocked
→ use metadata.internal / [::1]. Difficult: same, but blind → confirm via
the collector.UNION. Moderate: UNION/-- blacklisted → UnIoN
sha256(nonce + signing_secret) challenge-response (secret leaks via
a verbose error).mcpgoat/
├── DESIGN_PROMPT.md # the full build brief (Core + Extended catalog)
├── Dockerfile docker-compose.yml # one-command deploy
├── .github/workflows/ci.yml # regression gate + Docker smoke test
├── src/
│ ├── server.ts # Express host: control panel, MCP endpoint, OOB collector
│ ├── level.ts # the Easy/Moderate/Difficult switch
│ ├── scoreboard.ts # challenge catalog, per-level flags, scoreboard
│ ├── challenges.ts # all 26 challenges × 4 levels (incl. secure)
│ ├── buildServer.ts db.ts state.ts internal.ts
│ ├── attacker/client.ts # level-aware exploitation client / smoke test
│ ├── agent/agent.ts # victim-agent harness (naive vs --defended)
│ └── ci/check.ts # regression gate (npm run ci)
├── workspace/ vault/ # path-traversal / RCE targets (per-level flag files)
└── docs/SOLUTIONS.md docs/EXPLOITS.http
npm run ci boots an isolated server and asserts the whole lab still works —
78/78 scored flags captured, 26/26 exploits blocked at the secure level,
and the victim agent 3/3 compromised (naive) / 0/3 (defended). Expected
counts derive from the catalog, so it can't drift; a broken challenge or a fix
that springs a leak fails the gate (non-zero exit). The bundled
GitHub Actions workflow runs this plus a Docker
build + boot smoke-test on every push.
State is in-memory — restart to reset, or use the control panel's Reset
button / the mcpgoat_reset tool.
Built by Sabyasachi Dhal. If MCPGoat is useful to you — or you work on MCP / AI-agent security — I'd love to connect: linkedin.com/in/sabyasachidhal
Issues, ideas, and pull requests are very welcome — see
CONTRIBUTING.md. If this saved you time, a ⭐ on the repo
helps others find it.
MIT — open source, free to use and self-host. You may use, copy, modify,
merge, publish, distribute, sublicense, and sell copies (including commercially),
as long as you keep the copyright and license notice. See LICENSE.
© 2026 Sabyasachi Dhal.
The MIT license is permissive and comes with no warranty. This software is intentionally vulnerable and provided for authorized security training and education only. You are responsible for running it safely (keep it on
127.0.0.1/ inside a container) and for how you use it — do not point its tools at systems you are not authorized to test.
Deliberately vulnerable MCP server (aka MCP Goat) for security training — 26 challenges across 4 difficulty levels (incl. a secure reference), a victim-agent harness, and one-command Docker deploy. Pr
總覽
Deliberately vulnerable MCP server (aka MCP Goat) for security training — 26 challenges across 4 difficulty levels (incl. a secure reference), a victim-agent harness, and one-command Docker deploy. Practice penetration testing against the Model Context Protocol.
工具
尚無工具清單。遠端伺服器會在首次健康檢查後取得工具清單。
常見問題
在本頁複製適用於 Cursor、Claude Desktop、Claude Code 或 VS Code 的 stdio 設定。它使用發布者的安裝方式,而不是 PlugMCP 代理伺服器。
這筆記錄未列出必要的環境變數。
MCPGoat 透過 stdio 在本機執行。
上次檢查時間:2026-10-28。 Deliberately vulnerable MCP server (aka MCP Goat) for security training — 26 challenges across 4 difficulty levels (incl. a secure reference), a victim-agent harness, and one-command Docker deploy. Practice penetration testing against the Model Context Protocol.