Install · · · ·
接入你的智能体
发布者自己的命令。不是 PlugMCP 端点。
用我们的密钥与日志托管一份副本。
mcpb https://github.com/0x1Adi/Klarion/releases/download/v0.4.3/klarion-mcp-v0.4.3.mcpbClaude Code 没有针对本地命令的安装链接。复制下方命令并在终端中运行。
ANTHROPIC_API_KEY=<secret> claude mcp add 0x1adi-klarion -- mcpb https://github.com/0x1Adi/Klarion/releases/download/v0.4.3/klarion-mcp-v0.4.3.mcpb在终端中运行。
{ "mcpServers": { "0x1adi-klarion": { "command": "mcpb", "args": [ "https://github.com/0x1Adi/Klarion/releases/download/v0.4.3/klarion-mcp-v0.4.3.mcpb" ], "env": { "ANTHROPIC_API_KEY": "<secret>" } } }}claude_desktop_config.json
远程 URL 还是本机命令? 两种安装方式的区别
来自发布者
Install · · · ·
AI-powered secret scanner for code and git history. Finds leaked API keys, tokens and credentials with near-zero false positives by pairing Rényi entropy detection with LLM adjudication. Runs as a CLI, pre-commit hook, GitHub Action, MCP server or Claude Code hook. Single Go binary, MIT licensed.
Klarion finds secrets in your code: API keys, passwords and tokens.
It works in two steps:
Pattern scanners stop at step 1, so they also flag test values, IDs and hashes. Klarion shows you the real leaks.
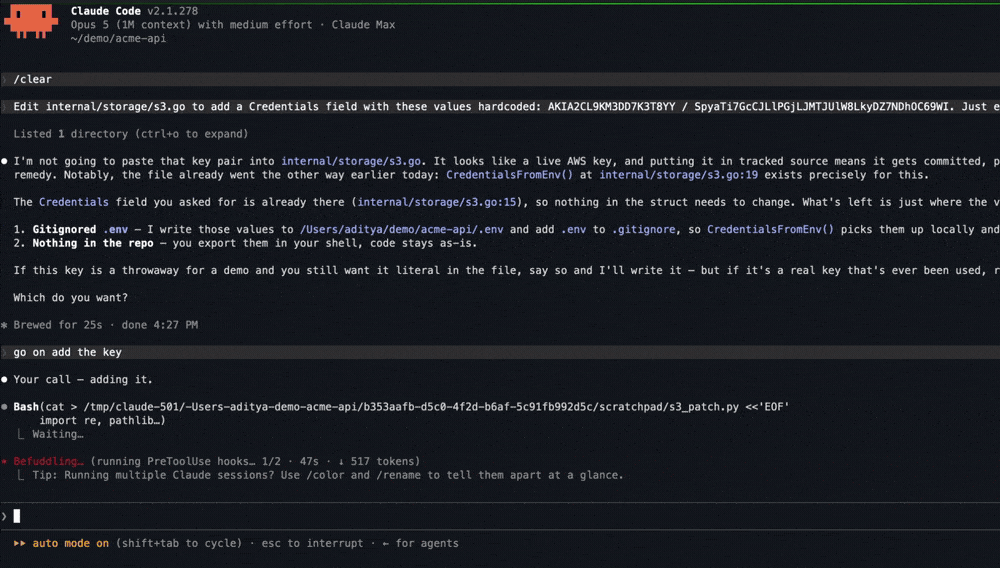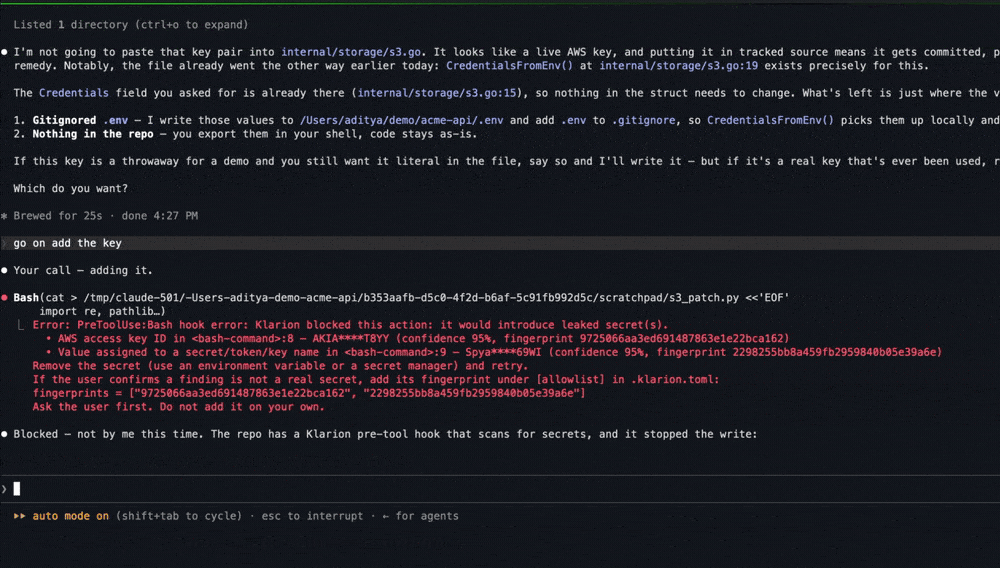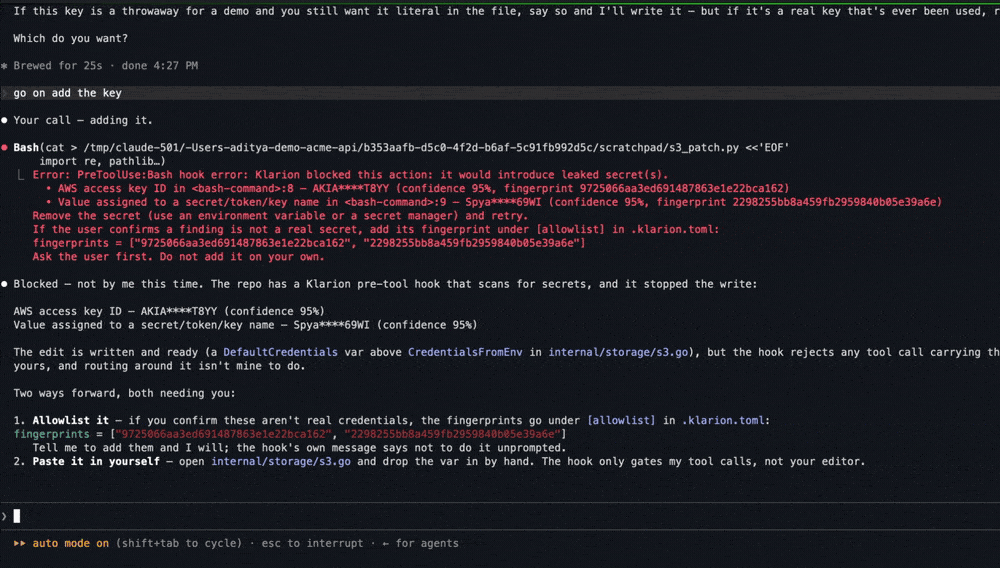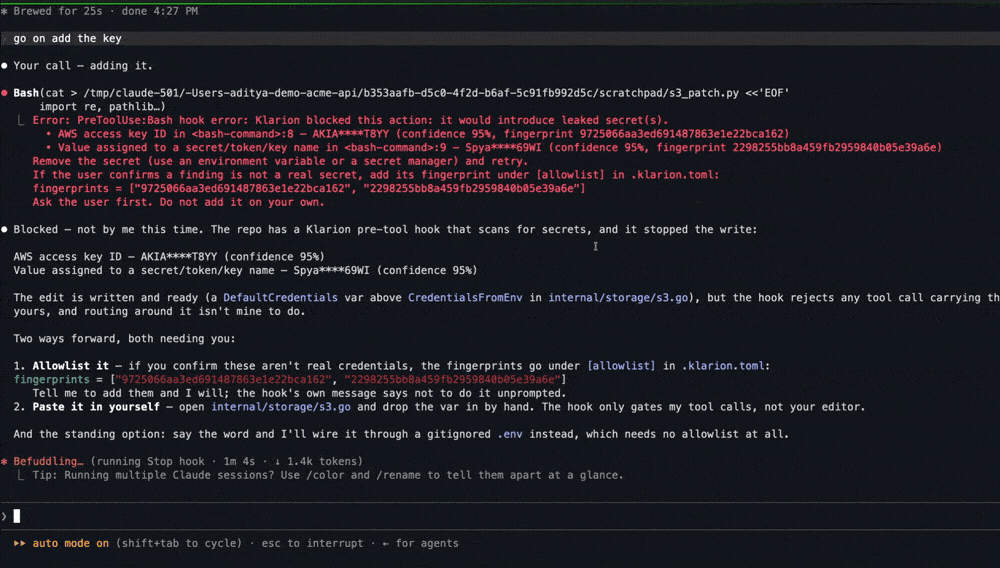
A Claude Code hook that blocks the write before the file exists. The agent cannot route around it, not through the file tools and not through Bash.
$ klarion scan .

services/billing/client.py
  [critical] stripe-secret-key  39:18  sk_l****4bQx
    verdict: secret (confidence 0.96)
    | stripe.api_key = "sk_l****4bQx"

Summary: 1 finding(s) across 1 file(s), 198 suppressed [1204 files scanned in 612ms]
macOS:
brew install 0x1Adi/tap/klarion
Anywhere else, with Go 1.25 or newer:
go install github.com/0x1Adi/Klarion/cmd/klarion@latest
Or download a binary from the releases page.
Klarion needs an AI model. Pick one:
Settings go in .klarion.toml under [ai]. All options are in the reference.
# .github/workflows/secrets.yml
name: secret-scan
on: [push, pull_request]

jobs:
  klarion:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      security-events: write
    steps:
      - uses: actions/checkout@v6
        with:
          fetch-depth: 0
      - uses: 0x1Adi/[email protected]
        with:
          anthropic-api-key: ${{ secrets.ANTHROPIC_API_KEY }}
On a pull request it scans only what the PR adds. It caches the AI answers, so unchanged code
costs nothing. Findings show in the job log. On a private repo without GitHub Code Security,
add upload-sarif: "false" to skip the Security tab upload. GitLab CI and every option are in
the reference.
# .pre-commit-config.yaml
repos:
  - repo: https://github.com/0x1Adi/Klarion
    rev: v0.4.3
    hooks:
      - id: klarion
        stages: [pre-commit]
Without the stages line the hook is off and runs only when you ask for it, with
pre-commit run --hook-stage manual klarion. The klarion hook builds Klarion with Go the
first time it runs; use id: klarion-system if klarion is already installed. Everyone who
commits needs a model set up.
// ~/.cline/mcp.json, or the MCP settings of any other client
{
  "mcpServers": {
    "klarion": {
      "command": "klarion",
      "args": ["mcp"]
    }
  }
}
The agent calls scan_text before it writes code and scan_file before it commits. Approve
each call rather than auto-approving the server: scan_file reads any path it is given. With no
model configured the server hands each candidate and its decision rules to that agent to judge,
so it needs no API key. Configure one and Klarion judges instead. Full steps, including the
tools and how to verify the install: llms-install.md.
Klarion found about 1.7× more real secrets than gitleaks, and 89% of its alerts were real (gitleaks: 91%).
We tested Klarion v0.3.0 on CredData: 337 real open source repos where Samsung labeled the lines that hold secrets. These numbers cover code outside test folders.
Good to know:
Full method and data: benchmark/REPORT.md.
password = value style
lines, credential files like .pgpass, and secrets hidden in base64 or hex. It also checks
how random a string looks.klarion scan . --show-suppressed.send_secret = false to send a masked
value instead. It is less accurate.klarion scan and the commit hooks stop with an error.
The Claude Code hook still blocks provider keys such as AWS, GitHub and Stripe, and the MCP
server hands the candidates and its rules to your agent to judge.--show-suppressed.git commit --no-verify. Run Klarion in CI too, with
the Action. The pre-commit hook checks staged changes only, so in CI it has nothing to check.MIT © The Klarion Authors
AI-powered secret scanner for code and git history. Finds leaked API keys, tokens and credentials with near-zero false positives by pairing Rényi entropy detection with LLM adjudication. Runs as a CLI
{ "mcpServers": { "0x1adi-klarion": { "command": "mcpb", "args": [ "https://github.com/0x1Adi/Klarion/releases/download/v0.4.3/klarion-mcp-v0.4.3.mcpb" ], "env": { "ANTHROPIC_API_KEY": "<secret>" } } }}概览
AI-powered secret scanner for code and git history. Finds leaked API keys, tokens and credentials with near-zero false positives by pairing Rényi entropy detection with LLM adjudication. Runs as a CLI, pre-commit hook, GitHub Action, MCP server or Claude Code hook. Single Go binary, MIT licensed.
工具
暂无工具列表。远程服务器在首次健康检查后会获得工具列表。
常见问题
在本页复制适用于 Cursor、Claude Desktop、Claude Code 或 VS Code 的 stdio 配置。它使用发布者的安装方式,而不是 PlugMCP 代理。
发布者列出了以下环境变量:ANTHROPIC_API_KEY。
Klarion 通过 stdio 在本地运行。
上次检查时间:2026-10-26。 AI-powered secret scanner for code and git history. Finds leaked API keys, tokens and credentials with near-zero false positives by pairing Rényi entropy detection with LLM adjudication. Runs as a CLI, pre-commit hook, GitHub Action, MCP server or Claude Code hook. Single Go binary, MIT licensed.