Security Audit Tool
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
接入你的智能体
发布者自己的命令。不是 PlugMCP 端点。
用我们的密钥与日志托管一份副本。
npx -y @iflow-mcp/[email protected]Claude Code 没有针对本地命令的安装链接。复制下方命令并在终端中运行。
claude mcp add qianniuspace-mcp-security-audit -- npx -y @iflow-mcp/mcp-security-audit@1.0.4在终端中运行。
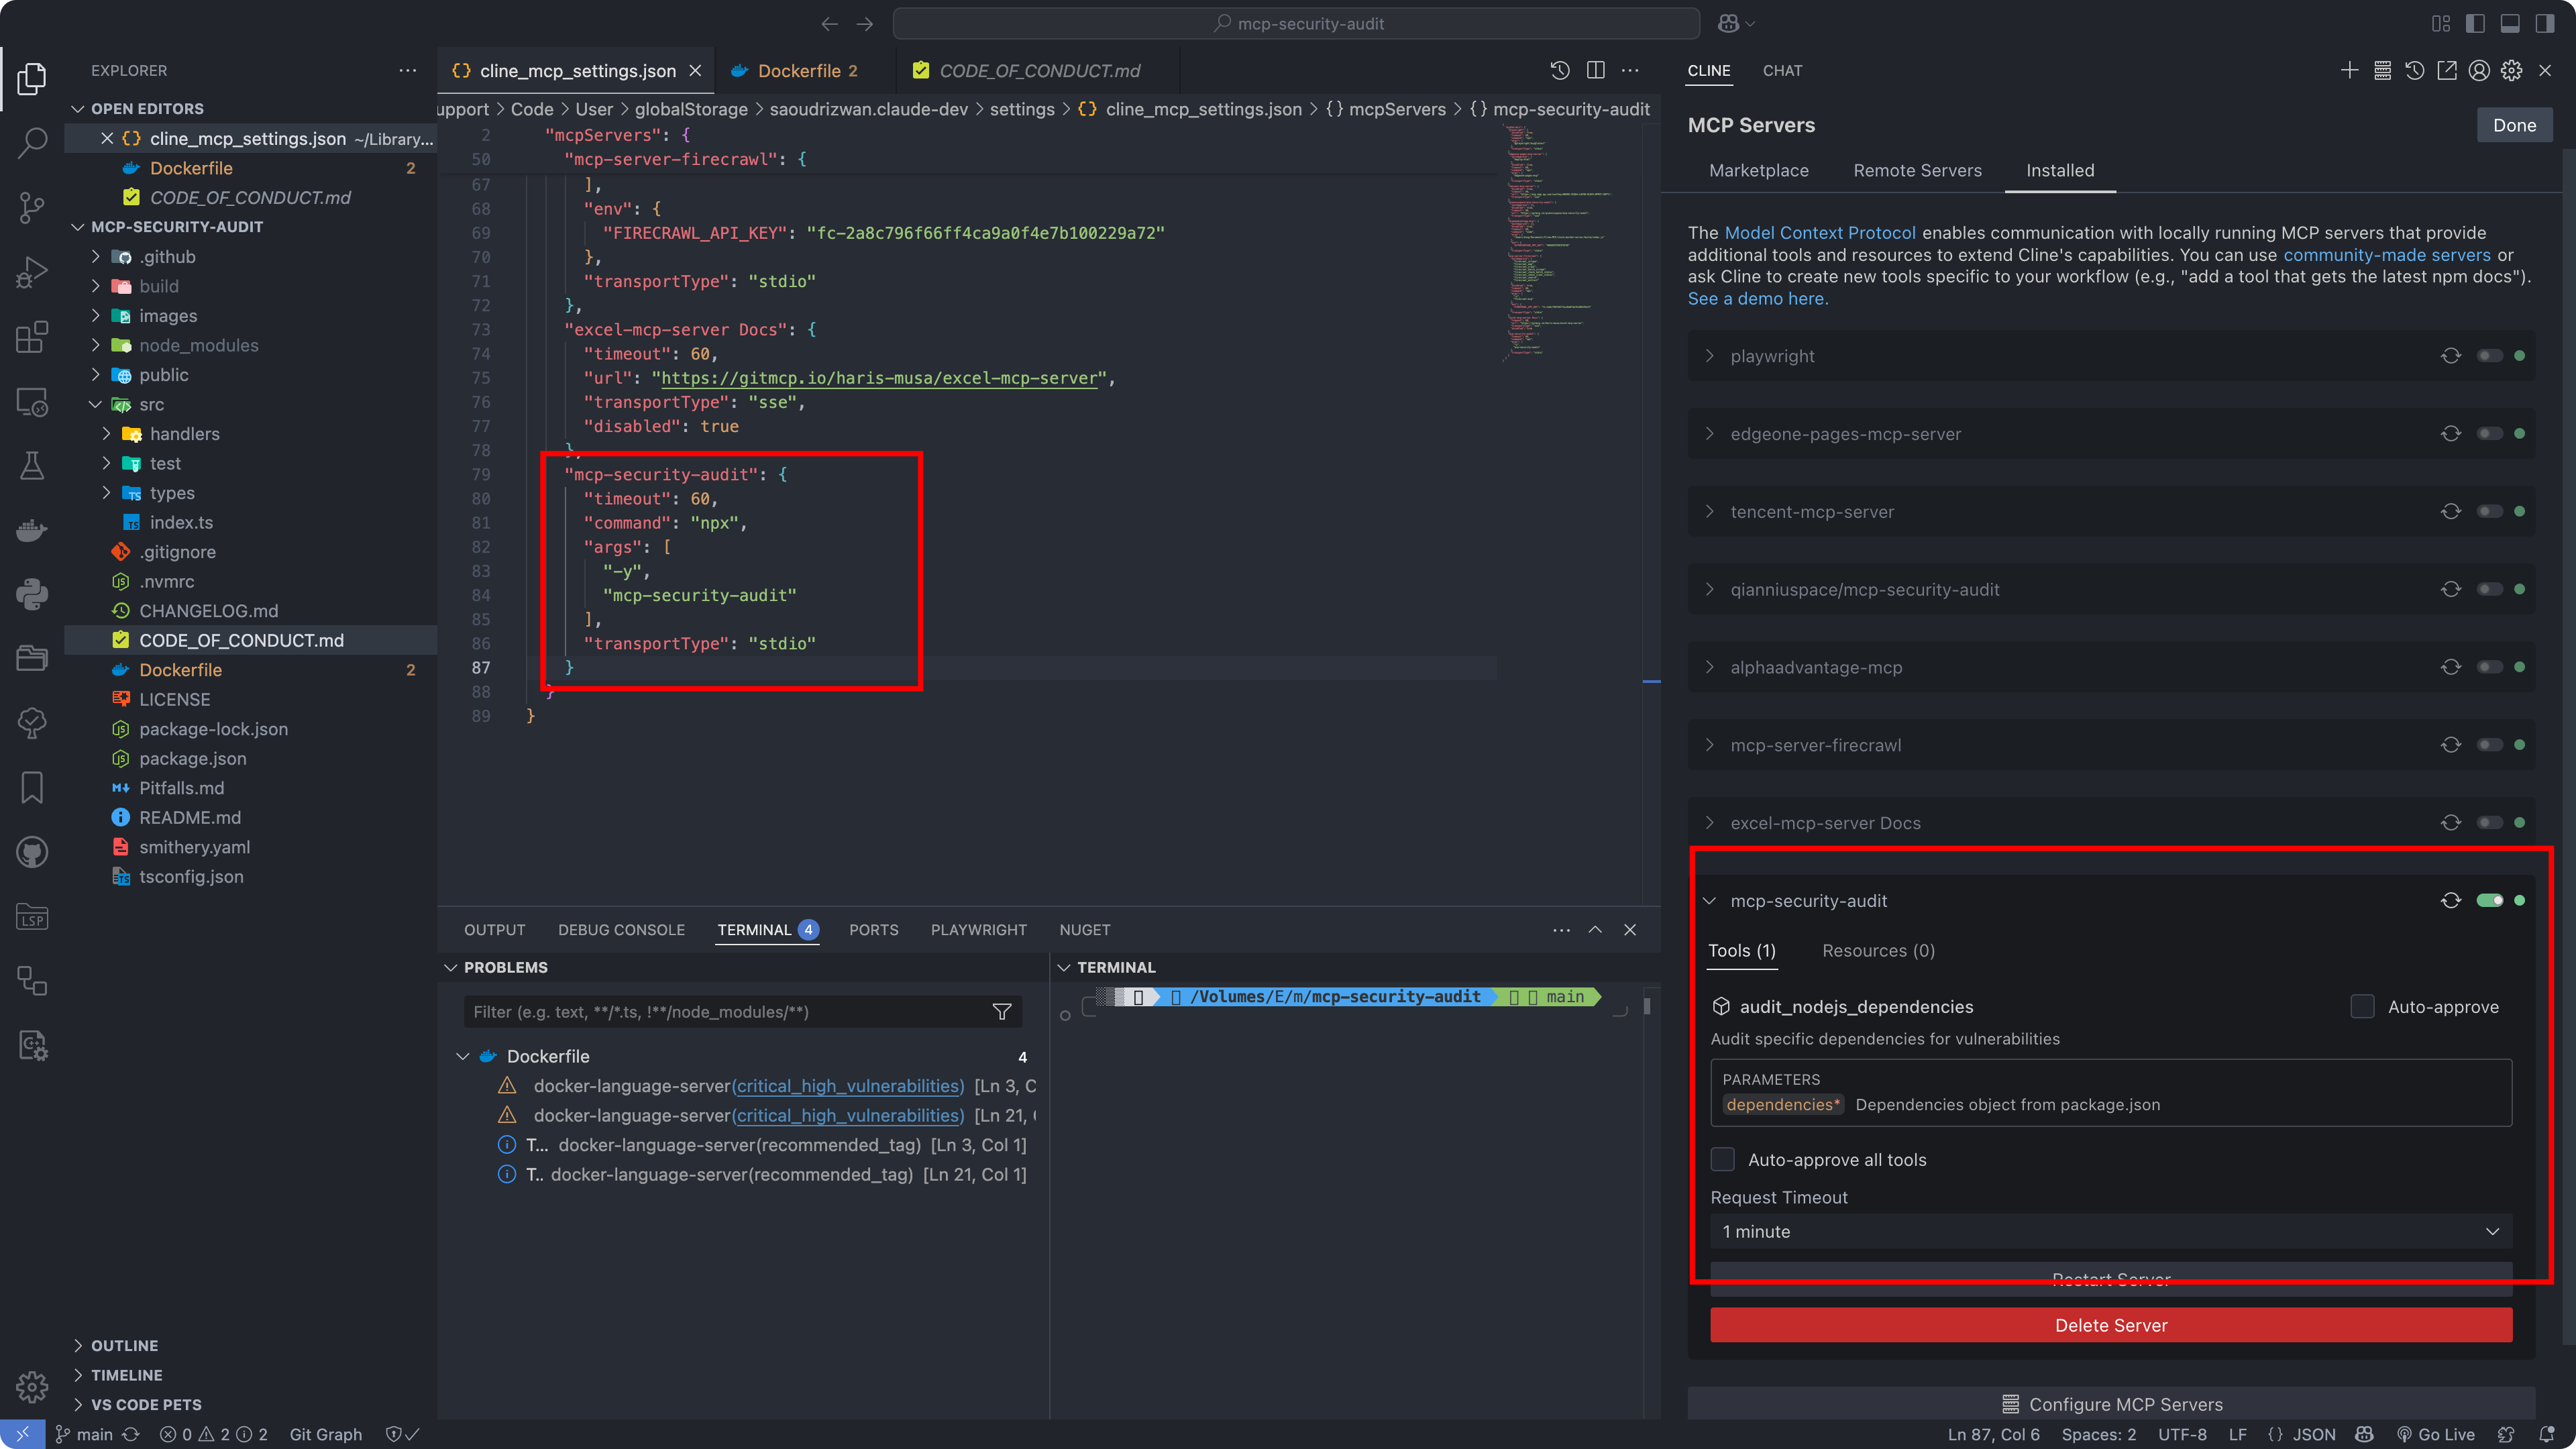
{ "mcpServers": { "qianniuspace-mcp-security-audit": { "command": "npx", "args": [ "-y", "@iflow-mcp/[email protected]" ] } }}claude_desktop_config.json
远程 URL 还是本机命令? 两种安装方式的区别
来自发布者
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
To install Security Audit Tool for Claude Desktop automatically via Smithery:
npx -y @smithery/cli install @qianniuspace/mcp-security-audit --client claude
{
  "mcpServers": {
    "mcp-security-audit": {
      "command": "npx",
      "args": ["-y", "mcp-security-audit"]
    }
  }
}
git clone https://github.com/qianniuspace/mcp-security-audit.git
cd mcp-security-audit
npm install
npm run build
{
  "mcpServers": {
    "mcp-security-audit": {
      "command": "npx",
      "args": ["-y", "/path/to/mcp-security-audit/build/index.js"]
    }
  }
}
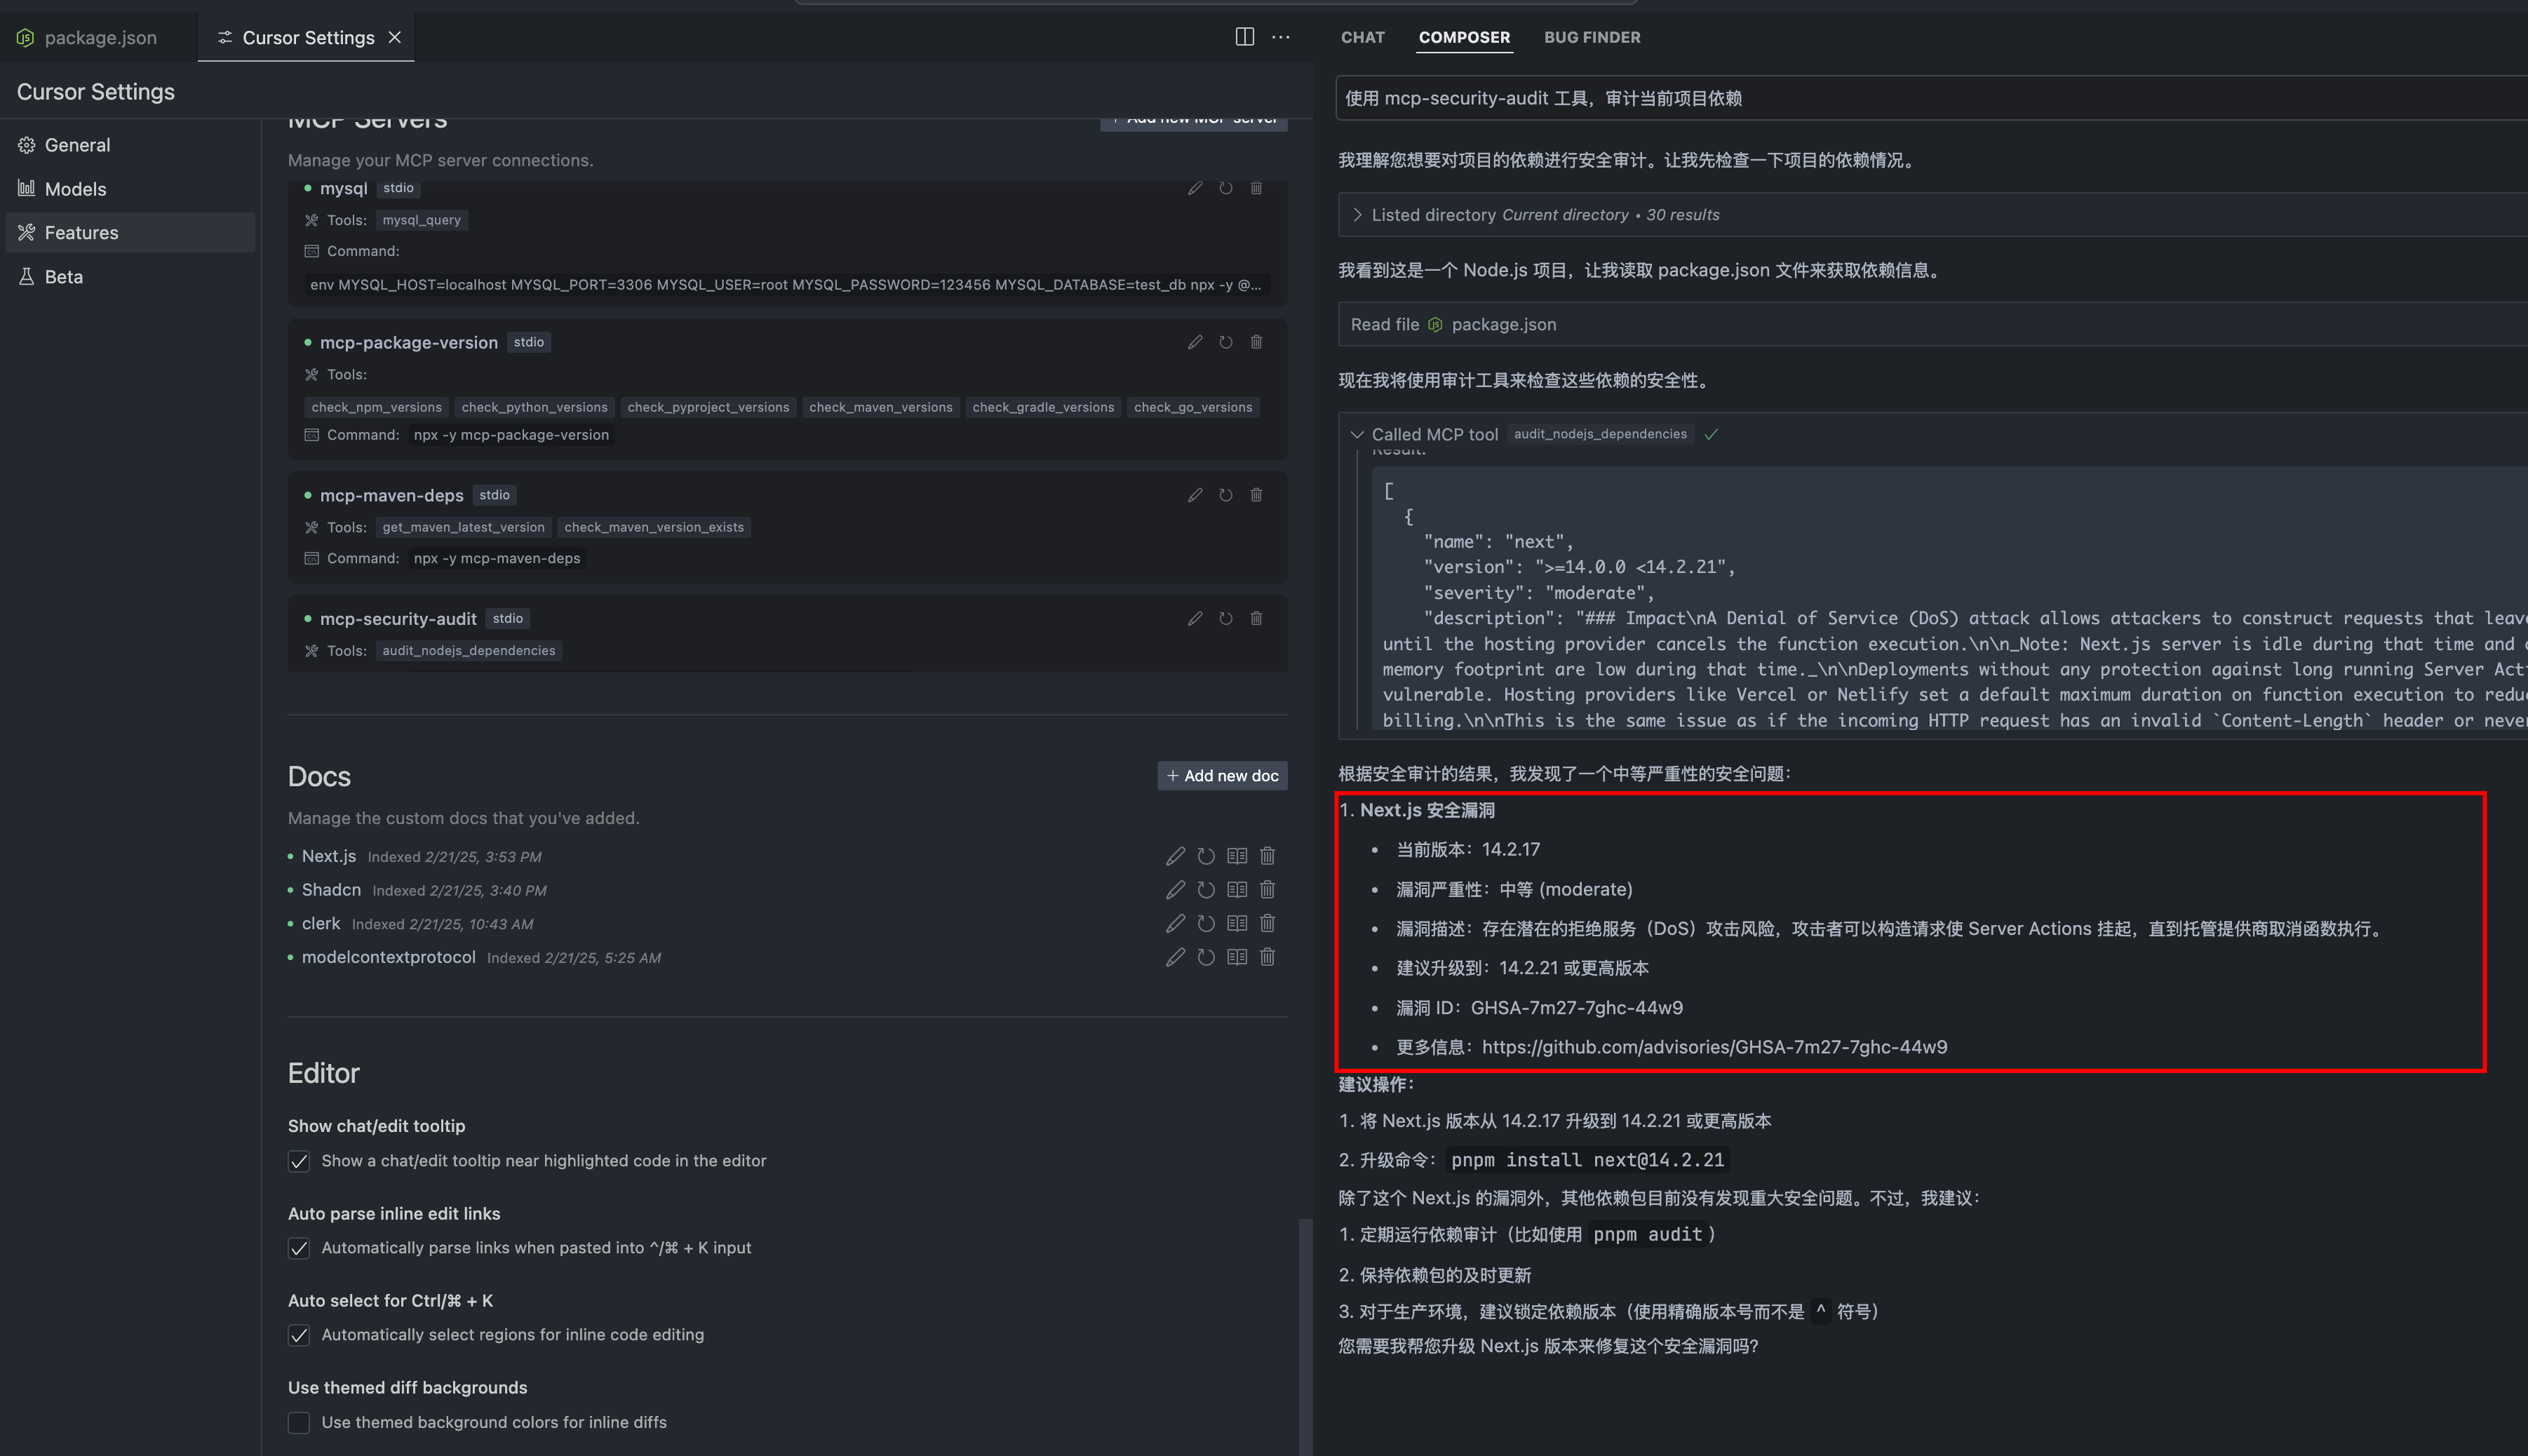
The tool provides detailed vulnerability information including severity levels, fix recommendations, CVSS scores, and CVE references.
{
  "content": [{
    "vulnerability": {
      "packageName": "lodash",
      "version": "4.17.15",
      "severity": "high",
      "description": "Prototype Pollution in lodash",
      "cve": "CVE-2020-8203",
      "githubAdvisoryId": "GHSA-p6mc-m468-83gw",
      "recommendation": "Upgrade to version 4.17.19 or later",
      "fixAvailable": true,
      "fixedVersion": "4.17.19",
      "cvss": {
        "score": 7.4,
        "vector": "CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N"
      },
      "cwe": ["CWE-1321"],
      "url": "https://github.com/advisories/GHSA-p6mc-m468-83gw"
    },
    "metadata": {
      "timestamp": "2024-04-23T10:00:00.000Z",
      "packageManager": "npm"
    }
  }]
}
{
  "content": [{
    "vulnerability": null,
    "metadata": {
      "timestamp": "2024-04-23T10:00:00.000Z",
      "packageManager": "npm",
      "message": "No known vulnerabilities found"
    }
  }]
}
For development reference, check the example response files in the public directory:
Note: The example responses shown above are transformed from the raw npm audit API responses to provide a more structured format. The original npm audit API responses contain additional metadata and may have a different structure.
Contributions are welcome! Please read our Contributing Guide for details on our code of conduct and the process for submitting pull requests.
This project is licensed under the MIT License - see the LICENSE file for details.
ESX ([email protected])
A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.
{ "mcpServers": { "qianniuspace-mcp-security-audit": { "command": "npx", "args": [ "-y", "@iflow-mcp/[email protected]" ] } }}工具
暂无工具列表。远程服务器在首次健康检查后会获得工具列表。
常见问题
在本页复制适用于 Cursor、Claude Desktop、Claude Code 或 VS Code 的 stdio 配置。它使用发布者的安装方式,而不是 PlugMCP 代理。
此记录未列出必需的环境变量。
MCP Security Audit 通过 stdio 在本地运行。
上次检查时间:2026-10-27。 A powerful MCP (Model Context Protocol) Server that audits npm package dependencies for security vulnerabilities. Built with remote npm registry integration for real-time security checks.