🛡️ ToolTrust Directory
This repo hosts tooltrust.dev — the website and pre-scanned report data. If you want to scan your own MCP servers, go to tooltrust-scanner.
A public registry of AI agent tools, continuously scanned for prompt injection, data exfiltration, and privilege escalation by ToolTrust Scanner.
🚨 Supply-Chain Incident Coverage (March 2026) ToolTrust now detects and blocks confirmed supply-chain incidents including the LiteLLM / TeamPCP compromise and the malicious axios npm publish (
[email protected],[email protected]). For npm-backed MCP servers, ToolTrust also scores dependency visibility, transitive lockfile evidence, lifecycle scripts, and IOC indicators such asplain-crypto-js.
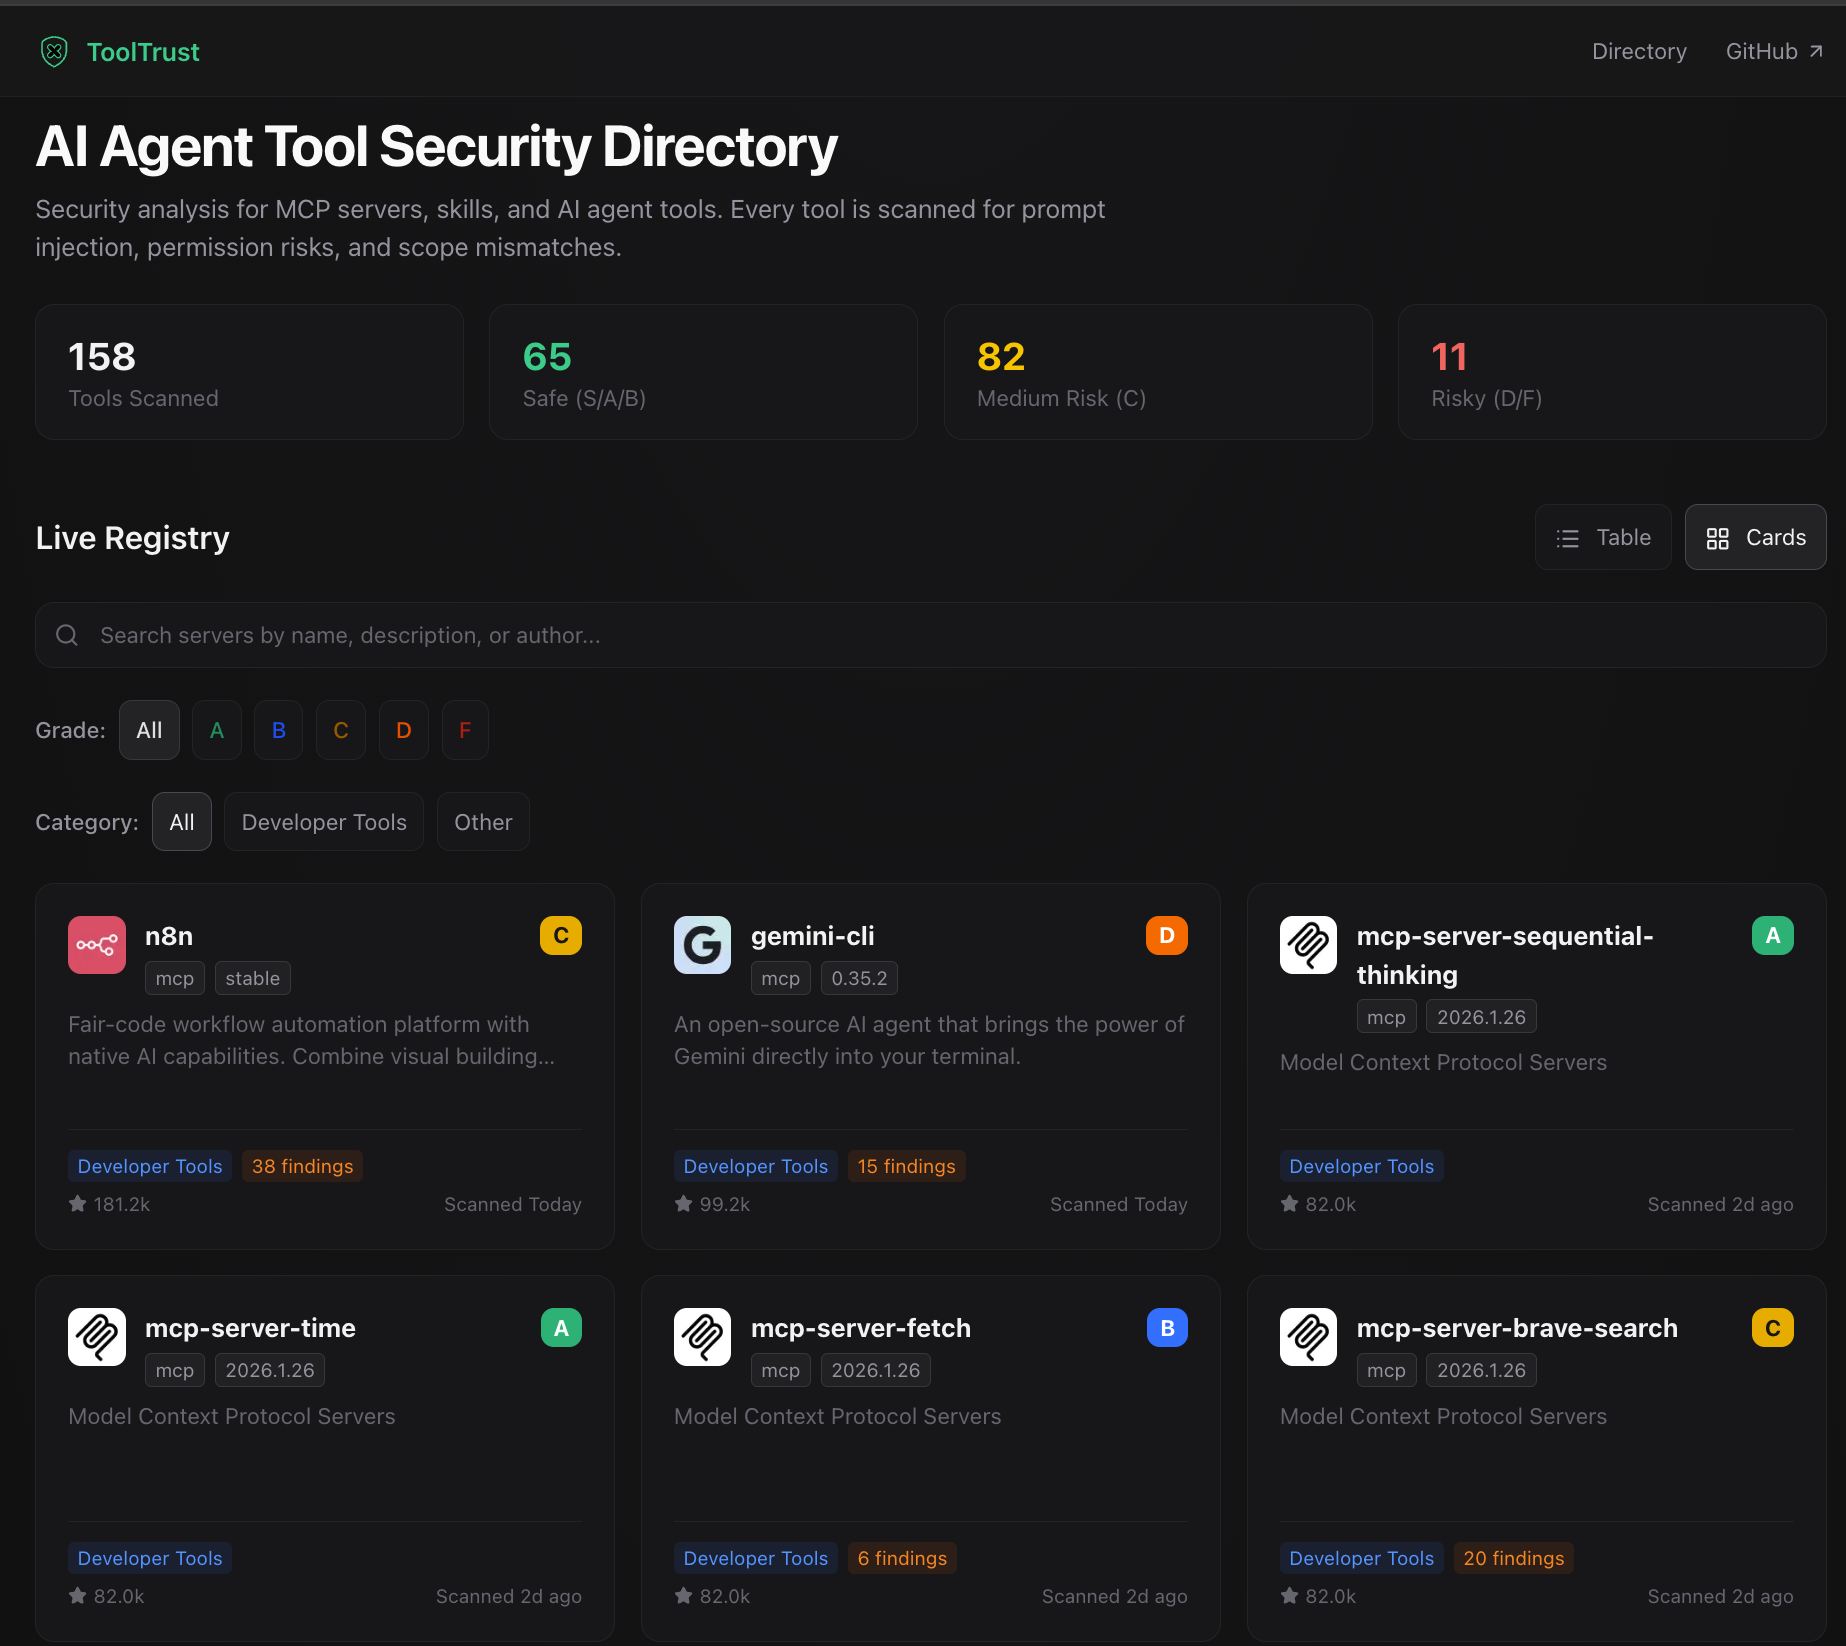
📊 Security Registry
Top 50 by popularity. View all 1946 tools → Full Directory · data/reports/ · docs/tools/
⚖️ Grading System
Full methodology: docs/methodology.md
🔍 Check Catalog
ToolTrust Scanner check IDs referenced in all reports:
Full details → docs/methodology.md
🤖 AI Agent Integration
Let your AI agent scan its own tools. Add ToolTrust as an MCP server in your .mcp.json or claude_desktop_config.json:
{
  "mcpServers": {
    "tooltrust": {
      "command": "npx",
      "args": ["-y", "tooltrust-mcp"]
    }
  }
}
This gives your agent five security tools:
Claude Code users: ask your agent to run tooltrust_scan_config to audit every MCP server in your project in one shot.
🤝 Contribute
Request a scan — open an issue with the tool's public URL and version.
Dispute a finding — open an issue referencing the finding ID (e.g. AS-002).
Integrate ToolTrust Scanner — see docs/dev.md for the data pipeline and schema spec.
📛 Add to your README
If your MCP server was audited and earned a grade, add our badge to your repo:
Grade A (recommended) — copy this into your README:
[](https://github.com/AgentSafe-AI/tooltrust-directory)
Other grades — replace grade-a with grade-s, grade-b, grade-c, grade-d, or grade-f:
Badges link to this directory. Generate SVGs locally: go run ./cmd/badge
⚙️ Automation
The registry table above is kept up to date by a daily GitHub Actions workflow:
.github/workflows/daily-audit.yml ← cron 00:00 UTC + manual dispatch
Each run:
- Discovers popular MCP servers via GitHub Search (50+ stars) plus Smithery-native servers (10+ uses)
- Scans new/updated tools with ToolTrust Scanner + OSV supply-chain analysis
- Publishes updated reports to
data/reports/and regenerates this README
Licensed MIT. Scanner engine: ToolTrust Scanner.