
agent-security-scanner-mcp
Security scanner for AI coding agents, MCP servers, prompts, and AI-suggested packages.
Run it before Claude Code, Cursor, Windsurf, Cline, OpenCode, or another agent trusts new code, tools, prompts, or dependencies.
Copy-Paste Start
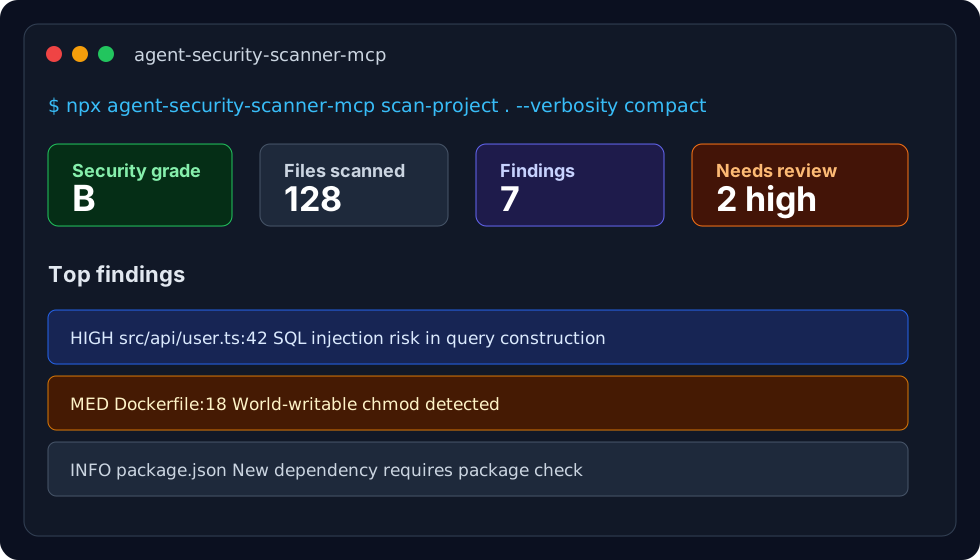
Scan any repo and get an A-F agent security grade:
npx agent-security-scanner-mcp scan-project . --verbosity compact
Install the scanner into your AI coding client:
npx agent-security-scanner-mcp init claude-code
Replace claude-code with cursor, claude-desktop, windsurf, cline, kilo-code, opencode, or cody.
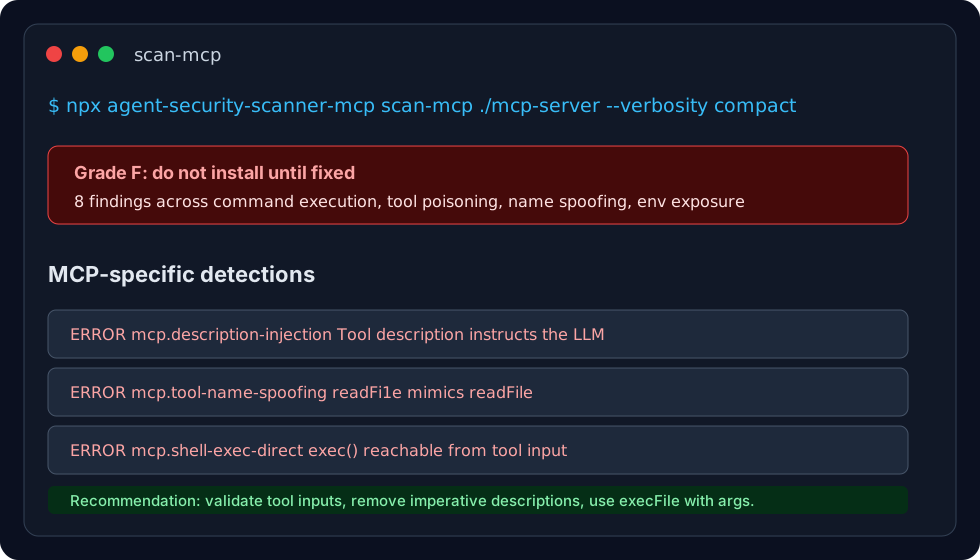
Audit an MCP server before adding it to an agent:
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
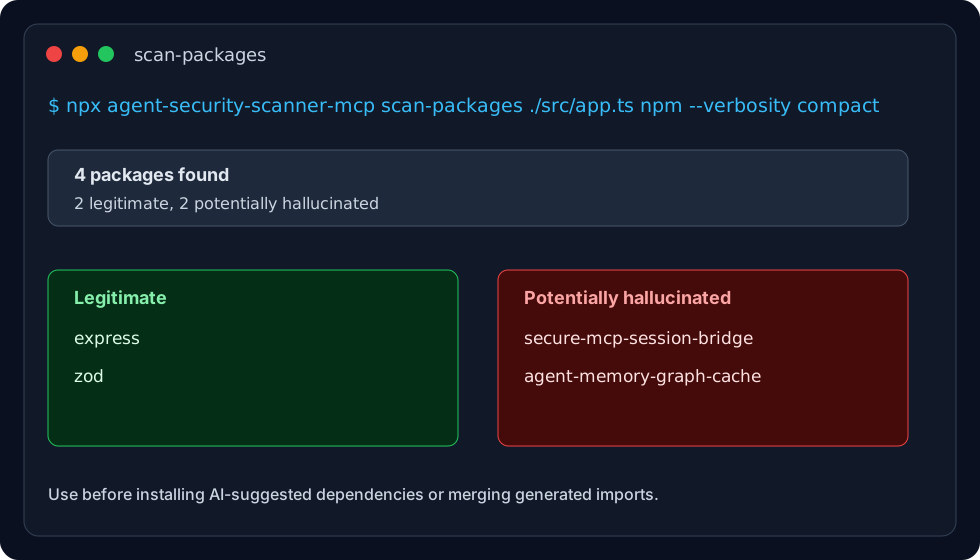
Check AI-generated imports for package hallucinations:
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
What It Catches
Screenshots
Project Scan
MCP Server Audit
Package Hallucination Detection
Demos
Run a safe local demo that creates intentionally vulnerable fixtures, scans them, and cleans them up.
# MCP audit demo: tool poisoning, spoofed tool name, command execution, secret exposure
npx agent-security-scanner-mcp demo --type mcp --no-prompt

# Package hallucination demo: real imports mixed with fake AI-generated package names
npx agent-security-scanner-mcp demo --type packages --no-prompt
Expected demo shape:
{
  "grade": "F",
  "findings_count": 8,
  "findings": [
    {
      "rule": "mcp.description-injection",
      "severity": "ERROR",
      "message": "Tool description contains imperative language directed at the LLM."
    },
    {
      "rule": "mcp.tool-name-spoofing",
      "severity": "ERROR",
      "message": "Tool name is close to a well-known MCP tool name."
    }
  ]
}
Install In Your Agent
npx agent-security-scanner-mcp init claude-code
Then restart the client. Your agent can call the scanner as an MCP tool.
Agent Playbook
Paste this into an agent task when you want it to work safely:
Before trusting new code, dependencies, prompts, or MCP tools, run:

1. npx agent-security-scanner-mcp scan-project . --verbosity compact
2. npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact when imports change
3. npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact before adding MCP servers
4. npx agent-security-scanner-mcp scan-diff --base main --target HEAD before opening a PR

Fix high-confidence security findings before continuing.
Common Workflows
Before You Trust An Agent-Written PR
npx agent-security-scanner-mcp scan-diff --base main --target HEAD --verbosity compact
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
Before Installing An MCP Server
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
Before Adding A Dependency Suggested By AI
npx agent-security-scanner-mcp check-package express npm
npx agent-security-scanner-mcp scan-packages ./package.json npm --verbosity compact
Add CI
npx agent-security-scanner-mcp init-ci github
Generate Share Copy From A Real Scan
npx agent-security-scanner-mcp scan-project . --verbosity compact > scan-result.json
npx agent-security-scanner-mcp share-kit --scan-result scan-result.json --output share-kit.md
CLI Reference
All scanner outputs support context-friendly verbosity:
--verbosity minimal   # counts only, best for CI
--verbosity compact   # default, best for agents and humans
--verbosity full      # audit/debug detail
MCP Tools For Agents
When installed as an MCP server, agents get these tool families:
Why Developers Install It
- One
npxcommand gives an A-F security grade for AI-written code. - MCP-specific checks catch risks that normal SAST tools miss.
- Package hallucination detection checks 4.3M+ package names across npm, PyPI, RubyGems, crates.io, pub.dev, CPAN, and raku.land.
- Output is compact by default so coding agents can read it without burning the context window.
- Works as a CLI, MCP server, GitHub Action workflow, Apify Actor, and semantic review agent.
- MIT licensed.
Semantic Code Review
cr-agent is bundled with the npm package for LLM-powered semantic review. It reads project intent, then looks for code that violates that intent.
npx cr-agent analyze ./path/to/project -p claude-cli --verbose
npx cr-agent analyze ./path/to/project -p openai --format sarif
Use it when rule-based scanning is not enough and the question is, "Does this code make sense for what this project is supposed to do?"
SBOM And Compliance Evidence
npx agent-security-scanner-mcp sbom-generate .
npx agent-security-scanner-mcp sbom-vulnerabilities .
npx agent-security-scanner-mcp sbom-check-hallucinations .
npx agent-security-scanner-mcp evaluate-compliance . --framework soc2-technical
Useful before releases, SOC 2 evidence collection, vendor reviews, and AI-generated dependency changes.
Apify Actor
Run the scanner as an Apify Actor when you want a hosted API or scheduled scans:
{
  "actorId": "folkloric_morale/agent-security-scanner",
  "input": {
    "target": "repository",
    "repoUrl": "https://github.com/your-org/your-agent.git",
    "repositoryScanMode": "quick",
    "includeTestFiles": false,
    "maxRepositoryFiles": 150,
    "severityThreshold": "medium"
  }
}
Latest Release
v4.5.8 adds diff-scoped cr-agent semantic review, fixes nested repository diff lookups, and filters semantic findings to changed hunks so PR reviews stay focused on code that actually changed.
Detailed release history lives in CHANGELOG.md. The older README-embedded changelog is archived at archive/README_CHANGELOG_ARCHIVE.md.
FAQ
Is this only for MCP servers? No. It scans normal repos, diffs, prompts, actions, packages, SBOMs, MCP servers, and AI skills.
Does it send my source code anywhere?
Rule-based CLI and MCP scans are local. cr-agent uses the provider you choose for semantic review.
Is it a replacement for npm audit? No. It complements npm audit by catching AI-specific risks: hallucinated packages, prompt injection, MCP tool poisoning, unsafe agent actions, and vulnerable generated code.
What should I run first?
Run npx agent-security-scanner-mcp scan-project . --verbosity compact.
Links
License
MIT