
🛡️ DocGuard
English · Português (BR) · Español
The enforcement layer for Spec-Driven Development. Validate. Score. Enforce. Ship documentation that AI agents can actually use.
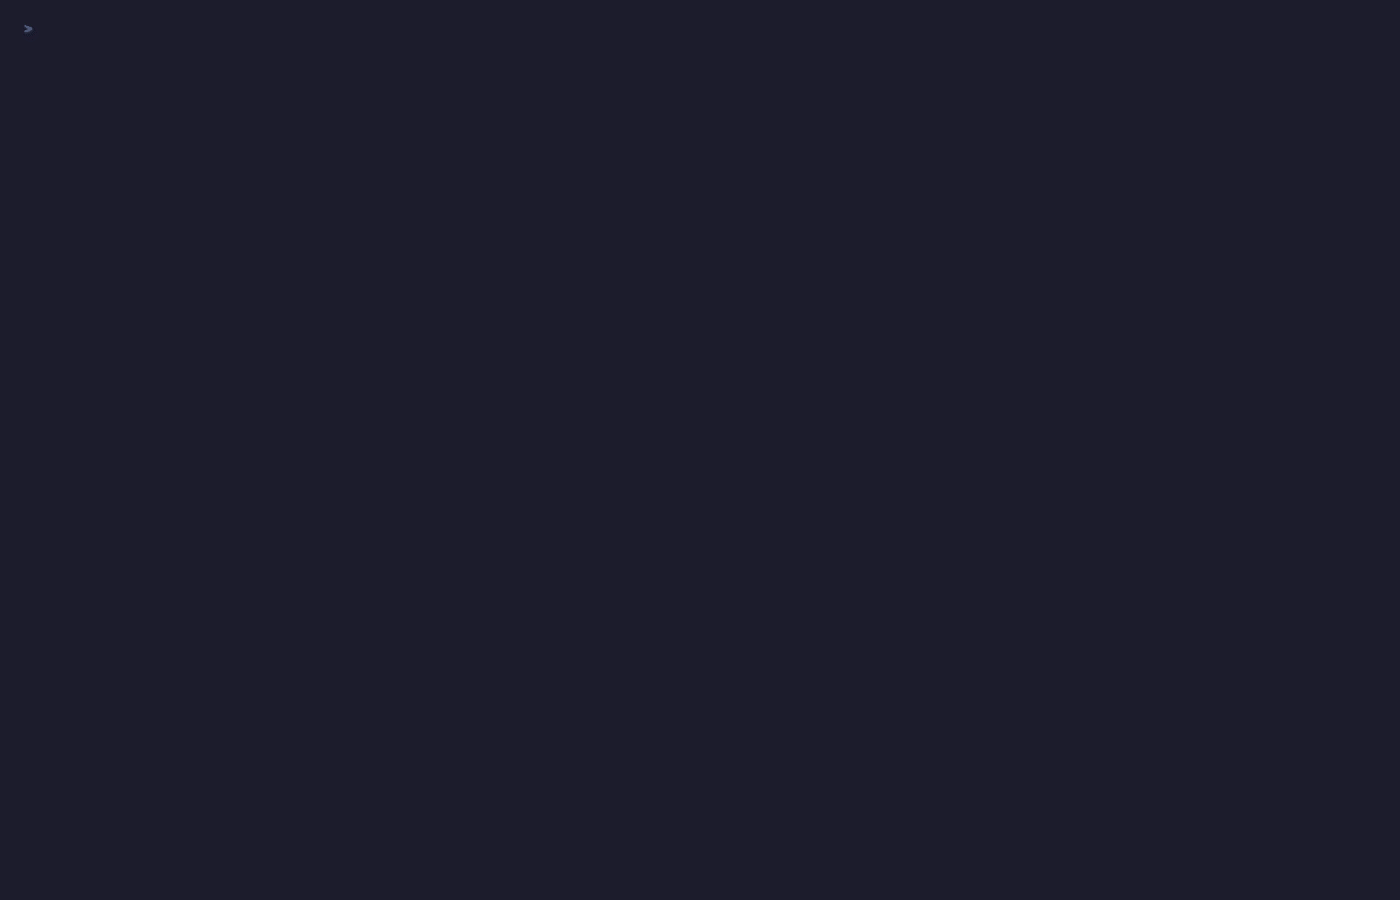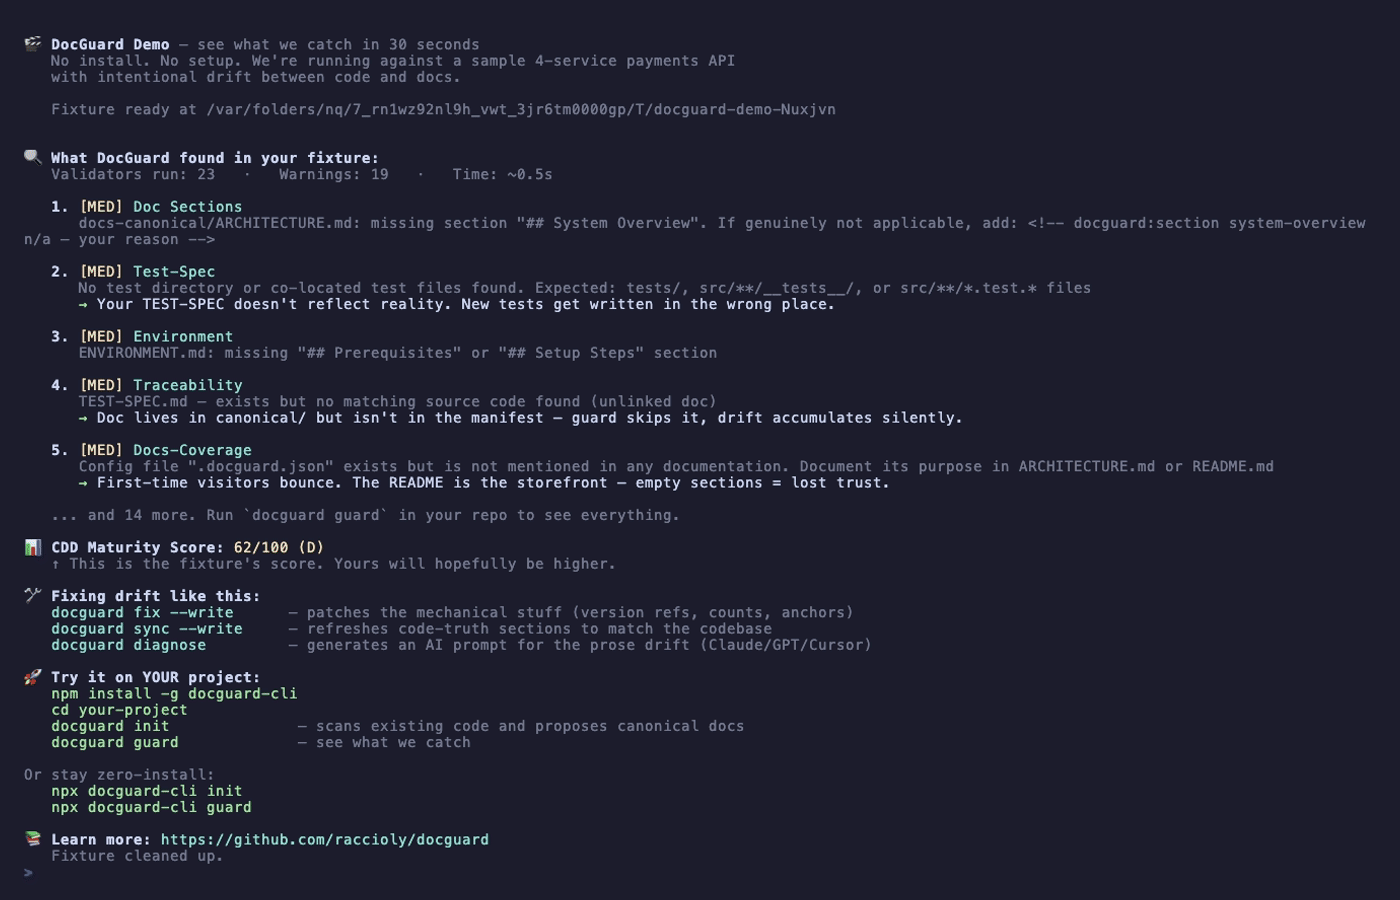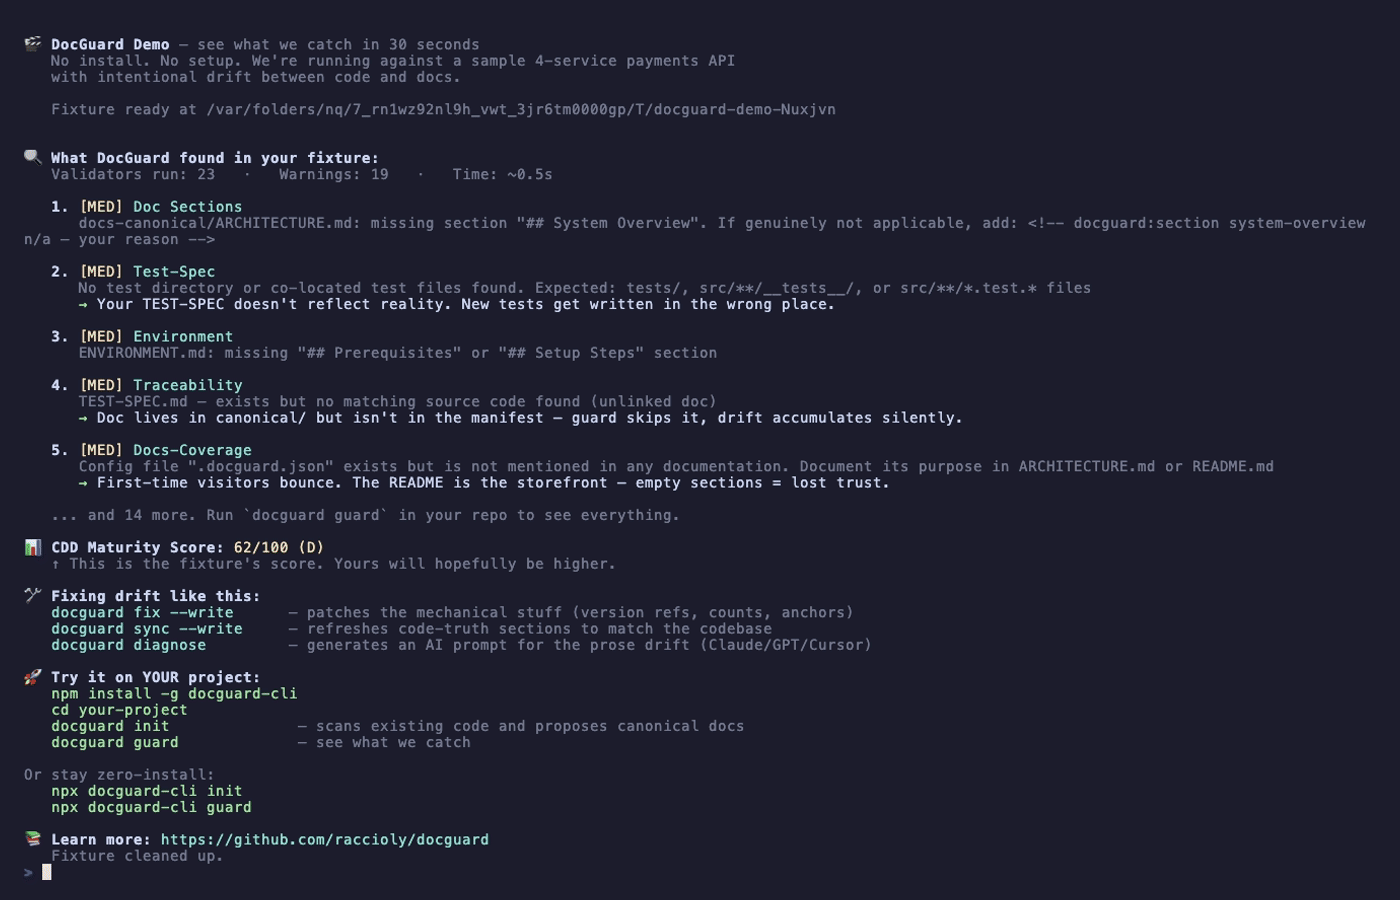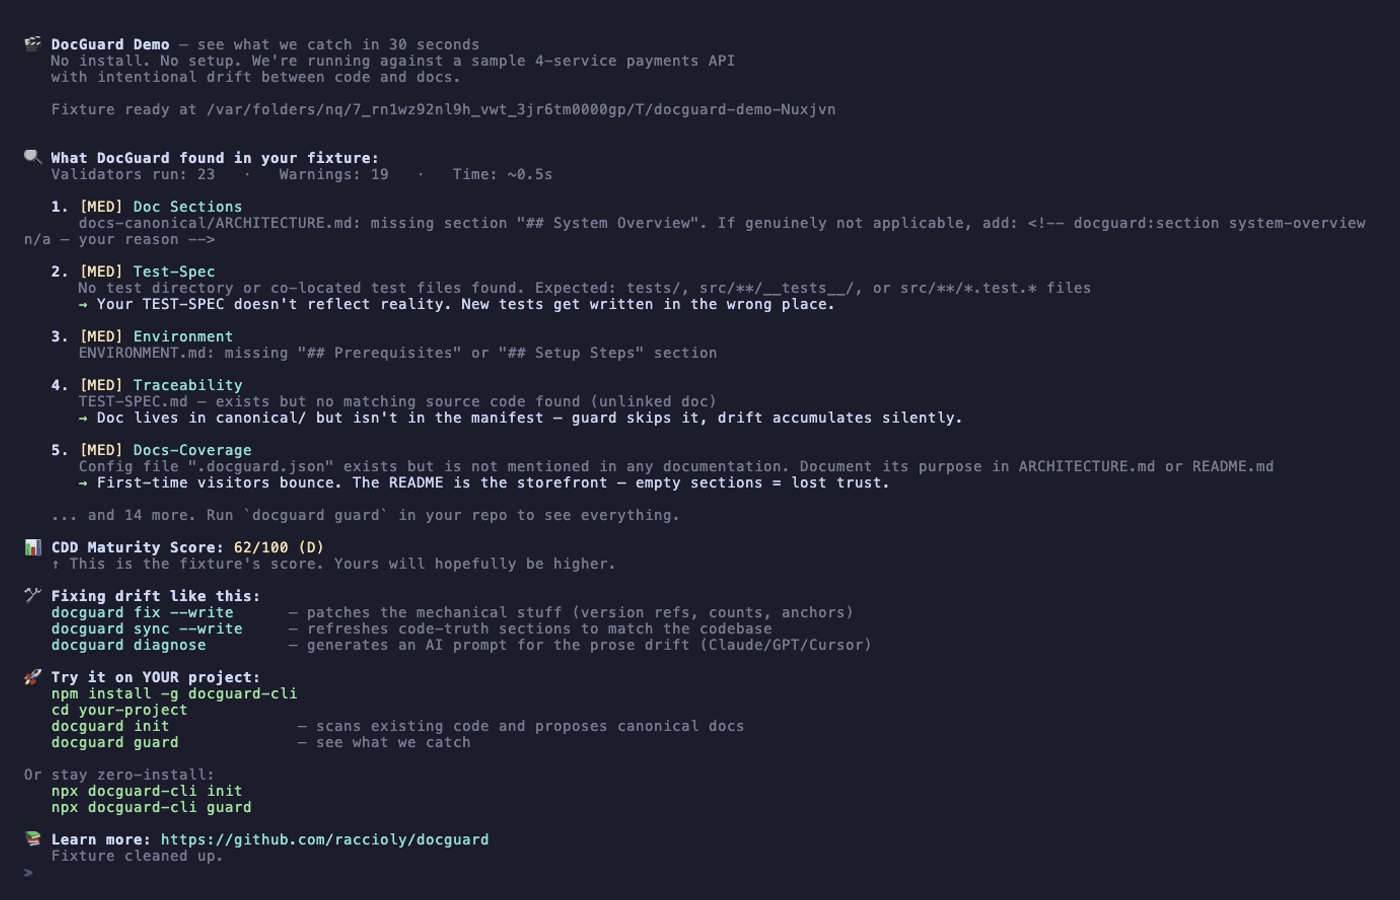
✨ See what DocGuard catches in 30 seconds — no install, no setup:
npx docguard-cli demoRuns against a baked-in sample project with intentional drift and shows you the findings + a clear path to fixing them.
📚 Documentation: Installation · Existing projects · Spec Kit · CI · Languages and frameworks · Coding agents · Finding codes · Troubleshooting
Table of Contents
- What is DocGuard?
- Why DocGuard?
- Quick Start
- Spec Kit Integration
- Usage
- Validators
- Reading a finding
- Templates
- AI Agent Support
- Slash Commands
- Examples
- Testing
- Enterprise Adoption
- CI/CD Integration
- What's New
- File Structure
- Configuration
- Research Credits
What is DocGuard?
DocGuard enforces Canonical-Driven Development (CDD) — a methodology where documentation is the source of truth, not an afterthought. AI writes the docs, DocGuard validates them.
DocGuard is an official GitHub Spec Kit community extension. It validates the artifacts that Spec Kit creates, ensuring your specs stay high-quality throughout the development lifecycle.
🧭 How it works (9-page brief) (PDF) · 📖 Philosophy · 📋 CDD Standard · ⚖️ Comparisons · 🔬 Validation · 🗺️ Roadmap
Architecture
graph TD
    CLI["CLI Entry<br/>docguard.mjs"] --> Commands["Commands (27)"]
    Commands --> guard["guard"]
    Commands --> generate["generate"]
    Commands --> score["score"]
    Commands --> diagnose["diagnose"]
    Commands --> setup["setup wizard"]
    Commands --> other["diff · init · fix · trace · impact · sync · reconcile · retire · specs · ignore<br/>explain · memory · upgrade · agents · hooks · badge · ci · watch"]

    guard --> Validators["Validators (34)"]
    generate --> Scanners["Scanners (4)<br/>routes · schemas · doc-tools · speckit"]
    score --> Scoring["Weighted Scoring<br/>8 categories"]
    diagnose --> Validators
    diagnose --> AIPrompts["AI-Ready<br/>Fix Prompts"]

    Validators --> Output["Output"]
    Scanners --> Output
    Scoring --> Output
    Output --> Terminal["Terminal"]
    Output --> JSON["JSON"]
    Output --> Badge["Badge"]

    style CLI fill:#2d5016,color:#fff
    style Validators fill:#1a3a5c,color:#fff
    style Scanners fill:#1a3a5c,color:#fff
    style Output fill:#5c3a1a,color:#fff
Distribution: Node.js core (npm) · Python wrapper (PyPI) · GitHub Action (
action.yml) · Spec Kit Extension (ZIP)
Why DocGuard?
DocGuard checks declared documentation facts against repository evidence and gives agents structured repair tasks. Deterministic checks cover supported facts, references, and generated sections. Human-authored requirements and architectural decisions retain their authority when implementation diverges.
A guard result describes the checks performed. The CDD grade measures structural maturity. Exact declarations in .docguard-evidence.json can verify selected statements against current local evidence; every other statement remains unverified. Coverage and unresolved claims remain visible, so teams can choose an appropriate enforcement policy.
Research motivates evaluation of this approach. A 2026 study found that repository context files did not generally improve task success and increased inference cost in its evaluated settings. It also found agents generally followed the instructions. These results support testing concise, relevant context and measuring actual task outcomes; they do not establish DocGuard's effectiveness. Evaluating AGENTS.md, revised June 2026.
The current roadmap prioritizes accurate detection, reproducible evidence, document lifecycle management, and contributor-supplied regression cases. Released plans and superseded specifications are removed from active AI context and remain recoverable from Git.
⚡ Quick Start
Package naming: this repo is
raccioly/docguard; the published package isdocguard-clion both npm and PyPI; the installed command isdocguard. Same project — the-clisuffix is just the registry name. The package runs no install scripts, sonpm i -g docguard-cli --ignore-scriptsis equivalent.
Node.js (npm)
# No install needed — run directly
npx docguard-cli diagnose

# Or install globally
npm i -g docguard-cli
docguard diagnose
Python (PyPI)
pip install docguard-cli
docguard diagnose
Note: The Python package is a thin wrapper that delegates to
npx. Node.js 18+ is required on the system.
Docker (MCP server)
The MCP server ships as a container image on GHCR — no Node.js install required. Public image, so no authentication is needed to pull it:
# Run the MCP server against the current directory
docker run -i --rm -v "$PWD":/workspace ghcr.io/raccioly/docguard:latest
The entrypoint is the stdio MCP transport: stdout is the JSON-RPC channel, so don't pipe anything else into it. Mount the project you want inspected at /workspace; tools inspect it by default, and a projectDir in a tool call must be /workspace or a directory inside it (add --root <dir> after the image name to serve another mounted tree).
Pin a version rather than tracking latest in CI:
docker run -i --rm -v "$PWD":/workspace ghcr.io/raccioly/docguard:0.34.9
The server is read-only — it never writes to the mounted project.
More ways to integrate
- pre-commit — changed-only guard on every commit:
repos: - repo: https://github.com/raccioly/docguard rev: v0.45.1 hooks: [{ id: docguard-guard }] # docguard-guard-full for pre-push - MCP (Claude, Cursor, any MCP client) —
claude mcp add docguard -- npx -y docguard-cli mcp; read-only tools to check docs (guard, score, diagnose, …) and to navigate them one bounded section at a time — the full list is in docs/ai-integration.md. Registry manifest ships in-repo (server.json, Smithery-ready). - GitLab CI — component staged at
templates/ci/gitlab-component.yml(guard/score/ci job with a SARIF artifact). - Homebrew —
brew install raccioly/tap/docguard. The release workflow renders the formula template inpackaging/homebrew/from the published npm tarball and pushes it to the tap.
Core Workflow
# 1. Initialize docs for your project
npx docguard-cli init

# 2. Or reverse-engineer docs from existing code
npx docguard-cli generate

# 3. AI diagnoses issues and generates fix prompts
npx docguard-cli diagnose

# 4. Validate — use as CI gate
npx docguard-cli guard

# 5. Check maturity score
npx docguard-cli score
The AI Loop
diagnose  →  AI reads prompts  →  AI fixes docs  →  guard verifies
   ↑                                                       ↓
   └───────────────── issues found? ←──────────────────────┘
diagnose is the primary command. It runs all validators, maps every failure to an AI-actionable fix prompt, and outputs a remediation plan. Your AI agent runs it, fixes the docs, and runs guard to verify.
Mechanical vs. agent fixes
DocGuard splits drift into two kinds and is explicit about which is which:
docguard fix --write only touches docs marked `` (override with --force), is idempotent, and prints exactly what changed. It never rewrites prose — that stays with the agent.
Continuous documentation workflow
guard ──▶ fix --write (mechanical, auto) ──▶ guard ──▶ diagnose (agent prompts for the rest)
- CI / pre-commit:
docguard hooks --type pre-commit --auto-fixinstalls a hook that applies mechanical fixes, re-stages the docs, then runsguard; anything left is surfaced as agent prompts. - Agent-driven:
docguard diagnose --autoscaffolds missing docs and applies mechanical fixes, then emits prompts for the content rewrites that remain. - JSON for automation:
guard/diagnose --format jsoninclude amechanicalFixesarray and tag each issuemechanicalvsagent, so an agent can apply or delegate precisely.
🌱 Spec Kit Integration
DocGuard is a community extension for GitHub's Spec Kit framework. While Spec Kit focuses on creating specifications (via AI slash commands like /speckit.specify and /speckit.plan), DocGuard focuses on validating their quality.
How They Work Together
┌─────────────────┐          ┌──────────────────┐
│    Spec Kit      │          │    DocGuard       │
│                  │          │                   │
│  /speckit.specify│ ──────→  │  docguard guard   │
│  Creates specs   │          │  Validates specs  │
│  (AI-driven)     │          │  (automated)      │
└─────────────────┘          └──────────────────┘
What DocGuard Validates in Spec Kit Projects
- spec.md — Mandatory sections (User Scenarios, Requirements, Success Criteria), FR-xxx IDs, SC-xxx IDs
- plan.md — Summary, Technical Context, Project Structure sections
- tasks.md — Phased task breakdown (Phase 1, 2, 3+), T-xxx task IDs
- constitution.md — Detected at
.specify/memory/constitution.mdor project root - Requirement traceability — FR, SC, NFR, US, AC, UC, SYS, ARCH, MOD, T IDs
Installing as a Spec Kit Extension
docguard init does this for you: when the specify CLI (Spec Kit ≥ 0.11.2, the floor the
extension declares) is on your PATH, it initializes Spec Kit for the coding agent the repository
already uses, then registers the DocGuard extension shipped inside the installed package. Nothing
is downloaded for the registration. If a project's registered extension is from another DocGuard
release, init re-registers it when the versions differ (keeping its priority), and
docguard upgrade --apply does the same. init says the workflow hooks are active only after each mandatory hook
(speckit.docguard.brief before specify, speckit.docguard.preflight before tasks,
speckit.docguard.guard after implement) resolves to a command file your agent can run; otherwise
it names the missing one. Spec Kit registers no extension commands for its generic integration,
so for generic DocGuard writes them next to Spec Kit's own commands (.agent/commands/ by
default). Every failure is printed with Spec Kit's own error and the command to run by hand. Only
init and upgrade --apply touch Spec Kit; other commands print a one-line hint at most.
DocGuard's own skills go where your agent reads them: .claude/skills/ for Claude Code (or the
skills directory of another skills-based integration), .agent/ for the generic integration or
an agent DocGuard cannot place. A commands-only integration such as Gemini gets Spec Kit's
speckit.docguard.* commands and no extra copies. The command and skill files run docguard from
your PATH when it is installed, and otherwise npx --yes docguard-cli@<version>, pinned to the
release they shipped with; they never fetch @latest.
Suggestions DocGuard prints (Next: …, Fix: …) name a slash command only when its file exists
for your agent, in its form (/speckit-docguard-guard in Claude Code, /speckit.docguard.guard
for generic); otherwise they print the CLI command.
docguard init registers the copy of the extension inside the installed package. To register
it yourself, use a release ZIP or a local checkout. A bare specify extension add docguard does
not work on a default Spec Kit setup: DocGuard is in Spec Kit's community catalog, which Spec Kit
uses for discovery only.
specify extension add docguard --from https://github.com/raccioly/docguard/releases/download/vX.Y.Z/spec-kit-docguard-vX.Y.Z.zip
specify extension add ./node_modules/docguard-cli/extensions/spec-kit-docguard --dev
See the Spec Kit guide for the hooks, the spec lifecycle registry and an end-to-end flow.
This registers the speckit.docguard.* commands listed in
extension.yml (invoked as
/speckit-docguard-guard and so on in skills-based agents such as Claude Code) and the
workflow hooks that run them.
Usage
DocGuard ships 27 commands (the "Daily 5" + 22 situational tools, including lifecycle reconciliation, doc dependency review, requirement anchors, agent-rule resolution, the suppression listing, retirement and spec tracking, the zero-install demo, the mcp server, and the ci pipeline gate). Six additional one-shot scaffolders are accessed via docguard init --with <name>. Legacy command forms remain compatible until v1.0 and print their replacements.
The Daily 5 — what you'll reach for 95% of the time:
Tools (situational, but day-to-day useful):
init --with <name> scaffolders — picked at init time:
Run them solo (docguard init --with hooks) or stacked (docguard init --with agents,hooks,badge,ci).
To declare an exact fact, copy templates/evidence-manifest.json to
.docguard-evidence.json, point its literal Markdown template at one unique
statement, and bind that value to a supported local source. Run
docguard verify --evidence --format json before enabling the guard in CI.
External compatibility declarations consume saved oasdiff or Buf output and
require current SHA-256 identities for every declared repository input.
Deprecation aliases — setup · agents · hooks · badge · llms · publish · impact remain compatible until v1.0 with a yellow stderr warning. audit → guard is permanent and silent; ci is a current first-class pipeline command.
CLI Flags
When run from a nested package without --dir, DocGuard checks only that
selected directory. If a bounded ancestor scan finds a .docguard.json or an
npm/pnpm workspace declaration that owns the package, stderr shows an exact
repository-scope rerun command. DocGuard never changes scope automatically. JSON,
SARIF, and JUnit stdout remain valid; machine runs receive one typed
docguard.repository-root-guidance JSON diagnostic on stderr. A local config,
an explicit --dir, an unmatched workspace, or a nested Git boundary suppresses
the suggestion.
Example Output
$ npx docguard-cli generate

🔮 DocGuard Generate — my-project
   Scanning codebase to generate canonical documentation...

  Detected Stack:
    language: TypeScript ^5.0
    framework: Next.js ^14.0
    database: PostgreSQL
    orm: Drizzle 0.33
    testing: Vitest
    hosting: AWS Amplify

  ✅ ARCHITECTURE.md (4 components, 6 tech)
  ✅ DATA-MODEL.md (12 entities detected)
  ✅ ENVIRONMENT.md (18 env vars detected)
  ✅ TEST-SPEC.md (45 tests, 8/10 services mapped)
  ✅ SECURITY.md (auth: NextAuth.js)
  ✅ REQUIREMENTS.md (spec-kit aligned)
  ✅ AGENTS.md
  ✅ CHANGELOG.md
  ✅ DRIFT-LOG.md

  Generated: 9  Skipped: 0
🔍 Validators
DocGuard runs 34 automated validators on every guard check. Source-facing validators are language-aware where their evidence model applies; repository and document validators operate independently of source language.
Counting note:
guardprints 30 result rows, not 29.Structureemits a second check result (Doc Sections) under the same validator key, so rows are checks, not validators. The published number is the count of shippedcli/validators/*.mjsmodules and is enforced by tests — don't derive it by counting output rows.
Per-validator controls (in .docguard.json):
{
  "validators": {
    "test-spec": false,                 // disable (kebab-case OR camelCase both accepted)
    "freshness": true
  },
  "severity": {
    "todoTracking": "high",             // warnings fail CI
    "freshness": "low"                  // warnings ignored for exit code
  },
  "findingSeverity": {
    "TRC004": "low",                    // only this finding becomes informational
    "SEC001": "high"                    // this exact code always blocks
  }
}
Exact findingSeverity entries take precedence over validator severity. Guard
JSON, SARIF, and JUnit retain the detector's intrinsic severity and add the
effective severity plus the policy source. Intrinsic errors stay blocking unless
their exact stable code is explicitly configured.
🎚️ Reading a Finding
A finding used to answer one question — "how worried should you be?" — with one
confidence field, which meant the field was doing three incompatible jobs at
once. DocGuard now separates them. These axes are independent: a blocking
error can be an escalation, and a high-confidence finding can still be one a
human must judge.
act — DocGuard asserts a defect and names the correction. Safe to apply,
including through docguard fix or an agent.
escalate — DocGuard observed a signal; the judgement is yours. Freshness
FRS002 ("13 code commits since the document was reviewed") is the canonical
case: the count comes from git log, so it is exact and confidence: high —
and it establishes only that a review is due, never that the document is
wrong. Editing a document until an escalation stops printing destroys the signal
and fixes nothing. A judged-and-left escalation is a correct outcome.
evidence.status tells you what a confidence label is worth. measured
quotes the reviewed precision corpus with n and a Wilson lower bound;
not-measured means the label is a maintainer's prior and nothing more. Most
codes are unmeasured — that does not make their findings wrong, only unverified,
and docguard feedback samples them for exactly that reason.
parserTier tells you what the detector could see. js-ast and py-ast
mean a syntax tree. regex-fallback means the language has one (JS/TS, Python)
but it was unavailable for that file. fallback-language means DocGuard has no
parser for the language at all — Go, Java, Kotlin, Ruby, Rust, PHP, C# — so
routes and env reads there are matched by pattern. Either way the absence of
a finding there is weak evidence, and the owning validator reports
applicability: partial with a reason that names the language and the file
count. Environment variables are matched by pattern in every supported
language; a source language with no env patterns (Swift, Scala, …) makes the
Environment check partial rather than a silent pass.
Every channel appears on every finding in guard --format json, in SARIF
result.properties, and per-issue in diagnose --format json (which also emits
a dispositionCounts summary). guard, diagnose, ci and report all print
the act/escalate split beside the verdict; report adds a column per channel to
its findings table. Run docguard explain <CODE> for one code's evidence.
📄 Templates
DocGuard ships 18 professional templates with metadata, badges, and revision history:
🤖 AI Agent Support
One-click MCP install
- Claude Code:
claude mcp add docguard -- npx docguard-cli mcp - Claude Desktop: download
docguard-v<version>.mcpbfrom the latest release and drag it into Settings → Extensions — you'll be asked which project folder to analyze. No npm, no JSON editing. - Anything MCP: DocGuard is a verified namespace on the official MCP registry (
io.github.raccioly/docguard).
DocGuard works with every major AI coding agent. All canonical docs are plain markdown — no vendor lock-in.
Always-on nudge hook (Claude Code)
docguard hooks --claude # install (remove: docguard hooks --claude --remove)
Registers a PostToolUse hook in the project's .claude/settings.json. After the
agent edits a canonical doc it is nudged to run docguard guard --changed-only;
after it edits a code file the docs reference, it is nudged toward docguard impact.
Merge-safe (only DocGuard's own entry is ever added/removed), throttled to one nudge
per file per 30 minutes, and the hook runtime can never break a session (errors are
silent by contract). Explicit opt-in — init never installs it for you.
⚡ Slash Commands
DocGuard ships four slash commands (commands/ in this repository):
Where they go depends on your agent. With a Spec Kit integration that uses skills (Claude Code,
Codex, Cursor, Copilot), DocGuard installs its skills instead, and Spec Kit installs the
speckit.docguard.* extension commands. The /docguard.* files are written to .agent/commands/
only for Spec Kit's generic integration, or when no Spec Kit integration is present. The
Coding Agents reference lists the
exact paths for each agent.
🧠 AI Skills (Enterprise)
Beyond slash commands, DocGuard provides 5 enterprise-grade AI skills — deep behavior protocols that tell AI agents not just what to run, but how to think, validate, and iterate. Skills are modeled after Spec Kit's skill architecture.
Workflow Hooks
DocGuard integrates into the spec-kit workflow as an automated quality gate:
Orchestration Scripts
For advanced users and CI/CD pipelines, DocGuard includes bash scripts with --json output:
📁 Examples
Three real-world projects to see DocGuard in action:
See examples/README.md for step-by-step instructions.
🧪 Testing
Test Suite
npm test # 3,283 tests (node:test, zero test dependencies)
Covers all 27 commands, every validator, project type detection, compliance profiles, JSON/SARIF/JUnit output, the packed npm tarball, and downstream field reports replayed as regression cases. Static test-case declarations are a lower bound of that number: Metrics-Consistency flags this line if it ever falls below what the test files declare.
CI Matrix
Self-Validation (Dogfooding)
DocGuard runs its own guard, score, diff, diagnose, and badge commands against itself in CI — ensuring the tool passes its own checks.
🏢 Enterprise Adoption
Everything runs local or in your CI — no SaaS, no data leaving your infra. The pieces that matter at company scale:
⚙️ CI/CD Integration
Full recipes: see
docs-canonical/CI-RECIPES.mdfor guard, auto-fix (commits mechanical fixes back to PRs), nightly sync, score-on-PR, and pre-commit configs.
GitHub Actions — Guard (most common)
name: DocGuard Guard
on: [pull_request, push]
permissions: { pull-requests: write }   # for the sticky PR comment (optional)
jobs:
  docguard:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
        with: { fetch-depth: 0 }
      - uses: raccioly/[email protected]
        with:
          command: guard
The action installs the docguard-cli version it was released with, so pinning
the action pins the CLI too. Set docguard-version: latest (or an exact
x.y.z) to override.
On pull requests, guard mode also gives inline PR feedback (both default on):
Both run even when guard fails — that's when the feedback matters. Prefer native
code-scanning integration? docguard guard --format sarif uploads straight to
GitHub Code Scanning via github/codeql-action/upload-sarif.
GitHub Actions — Auto-Fix (commits mechanical fixes back)
name: DocGuard Auto-Fix
on: { pull_request: { types: [opened, synchronize, reopened] } }
permissions: { contents: write, pull-requests: write }
jobs:
  autofix:
    runs-on: ubuntu-latest
    if: github.event.pull_request.head.repo.full_name == github.repository
    steps:
      - uses: actions/checkout@v4
        with:
          ref: ${{ github.event.pull_request.head.ref }}
          token: ${{ secrets.GITHUB_TOKEN }}
          fetch-depth: 0
      - uses: raccioly/[email protected]
        with: { command: fix, auto-commit: 'true', comment-on-pr: 'true' }
Pre-commit Hook
npx docguard-cli hooks --type pre-commit
Workflow starters (copy directly)
Two ready-to-use templates ship with the Spec Kit extension and as standalone files:
extensions/spec-kit-docguard/templates/github-workflows/docguard-guard.yml— mandatory CI gateextensions/spec-kit-docguard/templates/github-workflows/docguard-autofix.yml— PR auto-fix
✨ What's New
Highlights from recent releases:
- Calibrated finding channels —
disposition,evidence.statusandparserTiernow sit besideseverityandconfidenceon every finding, so "does CI block", "who decides", "how sure is the detector", "has this code ever been measured" and "which analyzer saw it" stop being one overloaded field. See Reading a Finding. - Adoption baseline —
guard --update-baselinefreezes a legacy repo's existing findings into a committed.docguard.baseline.json; guard/ci then gate only NEW drift, with suppression always visible. Adopt today, burn down at your own pace. docguard report— commit-stamped compliance-evidence bundle (guard verdict, findings by code, CDD score, ALCOA+ attributes, fix history) with a tamper-evident sha256 integrity hash. Also exposed as thedocguard_reportMCP tool.- Score history +
score --trend—docguard cirecords every run to.docguard/history.jsonl; the trend view shows the sparkline and delta over time. - Three machine formats for guard —
--format json,--format sarif(GitHub Code Scanning), and--format junit(GitLab, Jenkins, Azure DevOps, CircleCI). - MCP server, stdio + team HTTP — guard, score, verify, report, doc navigation and task
context as read-only agent tools:
claude mcp add docguard -- npx docguard-cli mcp. - Agent-file family sync —
agents --synctreats AGENTS.md as canonical and regenerates CLAUDE.md /.cursor/rules/ Copilot / Gemini variants with drift-proof source-hash markers. verify --evidence,verify --semantic, andverify --instructions— check exact local evidence declarations first, extract remaining numbers/limits/enums as agent tasks, and audit agent-instruction files for contradictions and stale pointers.docguard agent— one-shot ordered task graph with pre-filled code-truth, collapsing ~10 agent round-trips into one call.docguard agent --task <text>— opt-in task context from approved current specs and canonical docs, with hashed excerpts, source/test pointers, strict budgets, and honest abstention. The frozen 27-run evaluation preserved every tested behavior and cut median steps by 50% and latency by 17% versus the context pack, while using 80% more uncached input tokens.
See CHANGELOG.md for the full history.
📁 File Structure
your-project/
├── .specify/                        # Spec Kit (if using specify init)
│   ├── specs/
│   │   └── 001-feature/
│   │       ├── spec.md              # Requirements (FR-IDs, user stories)
│   │       ├── plan.md              # Implementation plan
│   │       └── tasks.md             # Task breakdown
│   ├── memory/
│   │   └── constitution.md          # Project principles
│   └── templates/
│
├── docs-canonical/                  # CDD canonical docs (the "blueprint")
│   ├── ARCHITECTURE.md              # System design, components
│   ├── DATA-MODEL.md                # Database schemas
│   ├── SECURITY.md                  # Auth, permissions, secrets
│   ├── TEST-SPEC.md                 # Required tests, coverage
│   ├── ENVIRONMENT.md               # Environment variables
│   └── REQUIREMENTS.md              # Spec-kit aligned FR/SC IDs
│
├── docs-implementation/             # Current state (optional)
│   ├── KNOWN-GOTCHAS.md
│   ├── TROUBLESHOOTING.md
│   ├── RUNBOOKS.md
│   └── CURRENT-STATE.md
│
├── AGENTS.md                        # AI agent behavior rules
├── CHANGELOG.md                     # Change tracking
├── DRIFT-LOG.md                     # Documented deviations
├── llms.txt                         # AI-friendly summary
└── .docguard.json                   # DocGuard configuration
⚙️ Configuration
Create .docguard.json in your project root (auto-generated by docguard init):
{
  "projectName": "my-project",
  "version": "0.4",
  "profile": "standard",
  "projectType": "webapp",
  "validators": {
    "structure": true,
    "docsSync": true,
    "drift": true,
    "changelog": true,
    "testSpec": true,
    "security": true,
    "environment": true,
    "docQuality": true,
    "specKit": true
  }
}
See Configuration Guide for all options.
🔬 Research Credits
DocGuard's quality evaluation and documentation generation patterns are informed by peer-reviewed research from the University of Arizona and the Joint Interoperability Test Command (JITC), U.S. Department of Defense:
- AITPG — AI-driven Test Plan Generator using Multi-Agent Debate and RAG (Lopez et al., IEEE TSE 2026)
- TRACE — Telecom Root Cause Analysis through Calibrated Explainability (Lopez et al., IEEE TMLCN 2026)
Lead researcher: Martin Manuel Lopez · ORCID 0009-0002-7652-2385
See CONTRIBUTING.md for full citations.
What the labels measure. DocGuard borrows TRACE's HIGH/MEDIUM/LOW vocabulary as deterministic strata (a validator's check pass-ratio). Detector precision is the quantity DocGuard actually measures: on a labelled, deliberately balanced benchmark corpus, published with sample sizes and Wilson 95% bounds in benchmarks/baseline.json (contract: schemas/docguard-benchmark-baseline.schema.json). Every number there carries a caveat explaining that benchmark precision on a balanced corpus differs from the base rate of stale claims in your repository. See VALIDATION.md.
⭐ Star History
🔒 Privacy & Supply Chain
DocGuard is local-first: no telemetry, no analytics, no phone-home — the full (short) policy is in PRIVACY.md. npm releases are published with provenance attestation, so you can verify each tarball was built by GitHub Actions from this repository.
📄 License
MIT — Free to use, modify, and distribute.
Made with ❤️ by Ricardo Accioly